
Topic
This article explains how to set up multi-factor authentication (MFA) for your technicians and end users in NinjaOne. It also explains how technicians use recovery codes when they cannot access their MFA method.
Environment
NinjaOne Platform
Description
Multi-factor authentication (MFA) provides an additional layer of security for your NinjaOne account by requiring multiple forms of verification before granting access to specific features, product areas, or administrative actions.
- All NinjaOne users are required to perform MFA both at login and when performing administrative actions.
- NinjaOne supports text-based (SMS) and time-based authentication and security keys.
- Technicians can download single-use recovery codes to log in and to change their MFA methods if they lose access to a registered MFA method.
Index
Select a category to learn more:
- Setting up Primary MFA for Your NinjaOne User
- Changing Authentication Methods
- Recovery Codes for Technicians
- Configuring Global Administrative Idle Time
- Technician MFA Requirements
- Additional Resources
Setting up Primary MFA for Your NinjaOne User
NinjaOne will prompt all users to enable MFA upon first login after accessing NinjaOne through the emailed account invitation. Once you enter your NinjaOne login credentials for the first time, NinjaOne will prompt you to set up a primary MFA method.
You must choose whether you want to use time-based, SMS-based, or hardware-based security key authentication as a primary MFA method and then continue through the required setup steps.
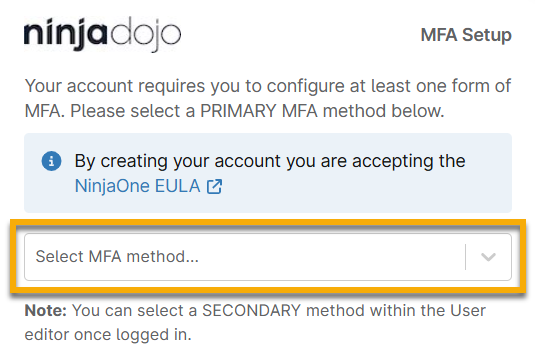
- To learn about time-based authentication, refer to the following section of this article titled Setting up an Authenticator App for Primary MFA.
- To learn about SMS-based authentication, refer to the section of this article titled Setting up SMS for Primary MFA.
- To learn about hardware-based security key authentication, refer to the section of this article titled Adding Hardware-based Keys or Additional Primary Authentication Method.
Setting up an Authenticator App for Primary MFA
To set up an authenticator app for your primary MFA, perform the following steps:
-
Download an authenticator app on an easily accessible endpoint, such as a local computer or mobile device. Any Time-Based One-Time Password (TOTP) application that supports QR code scanning and generates six-digit pins may work. NinjaOne has tested and confirmed that the following applications will work:
- Apple Passwords (for iOS 18)
- Authy
- Two-factor Authentication (2FA)
NinjaOne also supports browser plug-ins or desktop applications for time-based authentication. - Select Authenticator App from the Select MFA method drop-down menu. Then, scan the barcode with the device that has the authenticator app downloaded, or manually enter the code listed under the barcode to configure MFA.
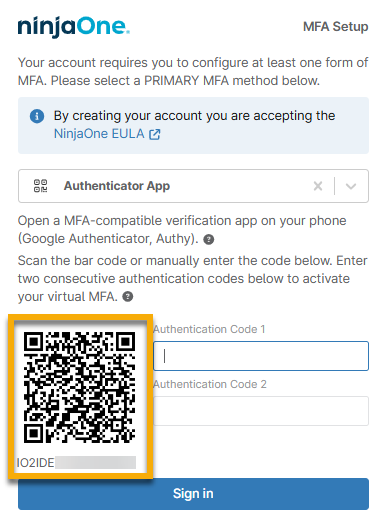
- Use the QR code or number in the authenticator app to set up the codes.
- Most authenticator apps will provide one code for several seconds and then refresh to provide another code. Enter the first code provided into the Authentication Code 1 field and then wait for the second code to appear. Enter the second code into the Authentication Code 2 field.
- Click Sign In to complete the setup process.
Setting up SMS for Primary MFA
As soon as you select SMS as your primary authentication method, NinjaOne will send an SMS message to the phone number currently associated with your user account. Enter the code into the available text field and click Sign In to complete setup.
If the user does not have access to the phone number set up for them, you can update it on their NinjaOne account configuration page or by clicking Change phone on the MFA Setup dialog. NinjaOne will prompt you to enter the correct phone number and send a code to this number.
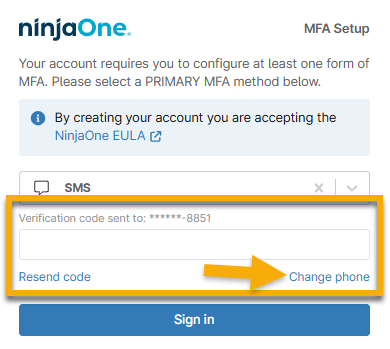
If you receive a prompt indicating your phone country code is not supported for SMS MFA, choose an alternative MFA option. MFA setup includes restrictions so users cannot register SMS MFA if they have a phone number with a country code that NinjaOne cannot support. For a full list of these restrictions, refer to NinjaOne SMS Phone Numbers.
Adding Hardware-based Keys or an Additional Primary Authentication Method
We recommend setting up a secondary backup MFA option to account for potential compatibility or implementation issues that may arise with the hardware key. For example, the hardware-based security key will not work if the user replaces their laptop and attempts to use the same NinjaOne account.
- Select Hardware-Based Security Key from the Select MFA method drop-down menu.
- Enter a unique identifier in the Security key name field.
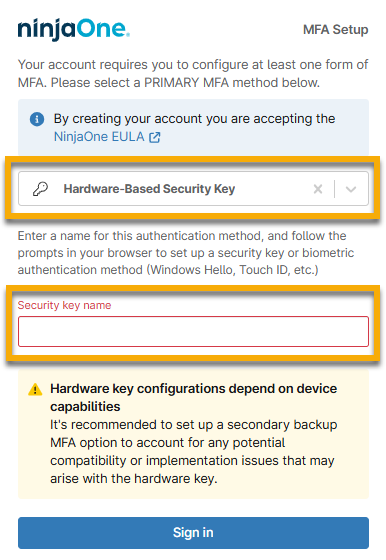
- Click Sign in.
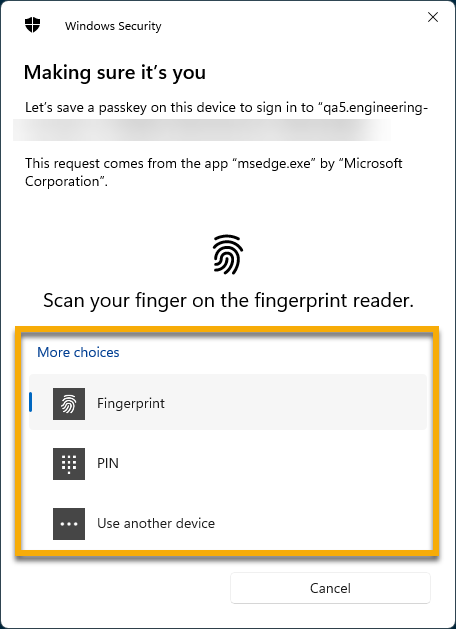
- The default option for Fingerprint may appear if your device is compatible. If your device does not have a fingerprint reader or you prefer to use an alternative method, select PIN or Use another device. Otherwise, follow the on-screen prompts.
Changing Authentication Methods
If a user cannot log in due to errors with their MFA, you can change the authentication method in NinjaOne. To do so, perform the following steps:
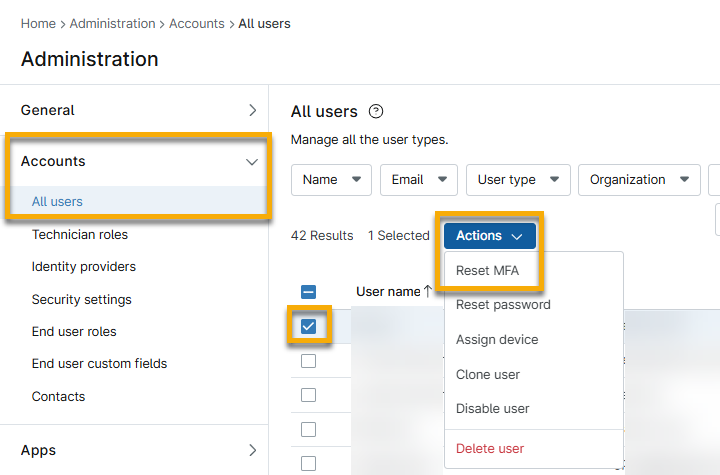
- Navigate to Administration → Accounts → All users.
- Select the checkbox for the technician or end user and then click Actions.
- Select Reset MFA and then click Reset in the confirmation dialog.
The next time the user logs in, NinjaOne will prompt them to set up their MFA.
Technicians who saved recovery codes can regain access without an administrator reset. To learn more about recovery codes, refer to Recovery Codes for Technicians.
NinjaOne will log the user out of all open sessions when:
- Configuring self-MFA
- Resetting password
- Configuring email
- Configuring phone number
Recovery Codes for Technicians
Recovery codes are single-use codes that a technician can use in place of a registered MFA method. Each technician receives 10 codes, and each code contains 10 letters and numbers. Recovery codes are available to technicians only, so end users do not receive them. Select a topic to continue:
- Saving Your Recovery Codes
- Generating New Recovery Codes
- Logging in with a Recovery Code
- Changing MFA Methods with a Recovery Code
Saving Your Recovery Codes
The NinjaOne platform displays your recovery codes in the Recovery codes window after you register MFA for a new account. It also displays them the first time you log in after your organization activates recovery codes. The NinjaOne platform shows the codes only once, so save them before you close the window. To save your recovery codes, perform the following steps:
- Review the codes in the Codes section of the Recovery codes window.
- Click Download file to save the codes in a .txt file, or copy the codes into a secure password manager.
The NinjaOne platform will not show these codes again. If you lose them, generate new codes.
Generating New Recovery Codes
If you lose your recovery codes or they are compromised, you can generate a new set. Generating new codes invalidates all of your earlier codes. You can generate new codes once every 24 hours. To generate new recovery codes, perform the following steps:
- Navigate to your user account settings and select Security.
- Click Generate new codes in the Recovery codes section.
- Complete the MFA prompt with a registered MFA method. You cannot use a recovery code to complete this prompt.
- Click Download file to save the new codes, or copy the codes into a secure password manager.
The NinjaOne platform will not show the new codes again, and the Generate new codes button will be unavailable for 24 hours. The NinjaOne platform records each regeneration in the activity log.
Logging in with a Recovery Code
If you cannot use your registered MFA method, you can use a recovery code to complete your login. Each code works one time. To log in with a recovery code, perform the following steps:
- Enter your username and password.
- Click Enter recovery codes under Having trouble verifying your chosen MFA method? on the MFA prompt.
- Enter one of your 10-character recovery codes in the Enter recovery code field.
- Submit the code.
The NinjaOne platform will log you in and will invalidate the code that you used. The following behaviors also apply:
- If you enter an incorrect code three times in one login session, the NinjaOne platform blocks further attempts in that session. Start a new login session to try again.
- The NinjaOne platform records each successful and failed recovery code login in the activity log.
If you do not have recovery codes, you can click Request MFA reset after you enter your username and password. This option is available only after a system administrator activates the Allow MFA reset requests toggle. To learn how, refer to Technician MFA Requirements.
Changing MFA Methods with a Recovery Code
You can use a recovery code to add, change, or remove one of your own MFA methods after you log in. When the MFA prompt appears in your account settings, click Enter recovery codes and enter one of your recovery codes. Each code works one time.
Configuring Global Administrative Idle Time
The global administrative idle time is the interval before NinjaOne prompts a user to re-authenticate their MFA when attempting to perform an administrative task, including initiating remote connections to devices. Idle time will determine how often technicians must re-authenticate.
Your global administrative idle time applies to all users in your NinjaOne environment, and a system administrator can configure it by following these steps:
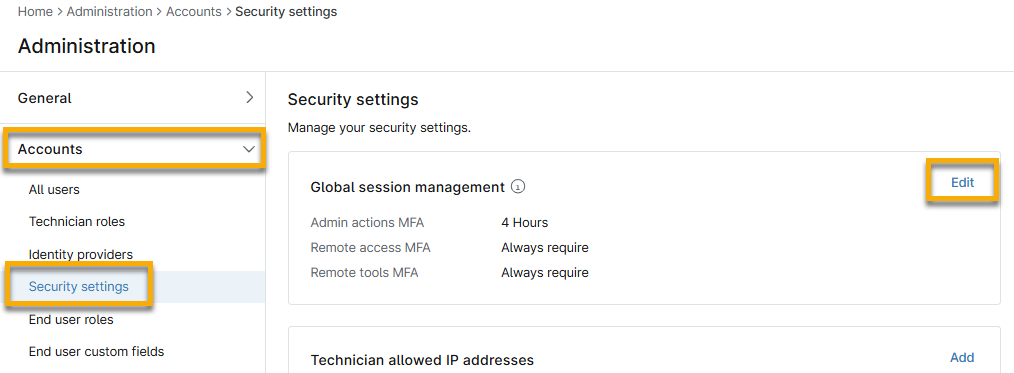
- Navigate to Administration → Accounts → Security Settings.
- Click Edit in the Global session management section.
- Configure the following settings:
| Setting | Description |
|---|---|
| Administrative actions MFA | If a user attempts an administrative task outside the selected window of time, NinjaOne prompts the user to re-authenticate with one of their MFA methods. |
| Remote access MFA | This setting determines the MFA idle timeout for NinjaOne Remote, Splashtop, and Cloud RDP. |
| Remote tools MFA | This setting determines the MFA timeout for command line tools, such as CMD and PowerShell. |
Technician MFA Requirements
Technicians and System administrators can send a request to System administrators to notify them that their MFA needs to be reset. This built-in notification system allows technicians to regain access to NinjaOne via assistance from their IT Team, rather than having to reach out to NinjaOne Support.
You can customize your notifications to be sent via SMS, email, Notification Channels, or create tickets. To learn how, refer to NinjaOne Endpoint Management: Notification Channels and Alerts.
- Navigate to Administration → Accounts → Security Settings.
- Click Edit in the Technician MFA requirements section.
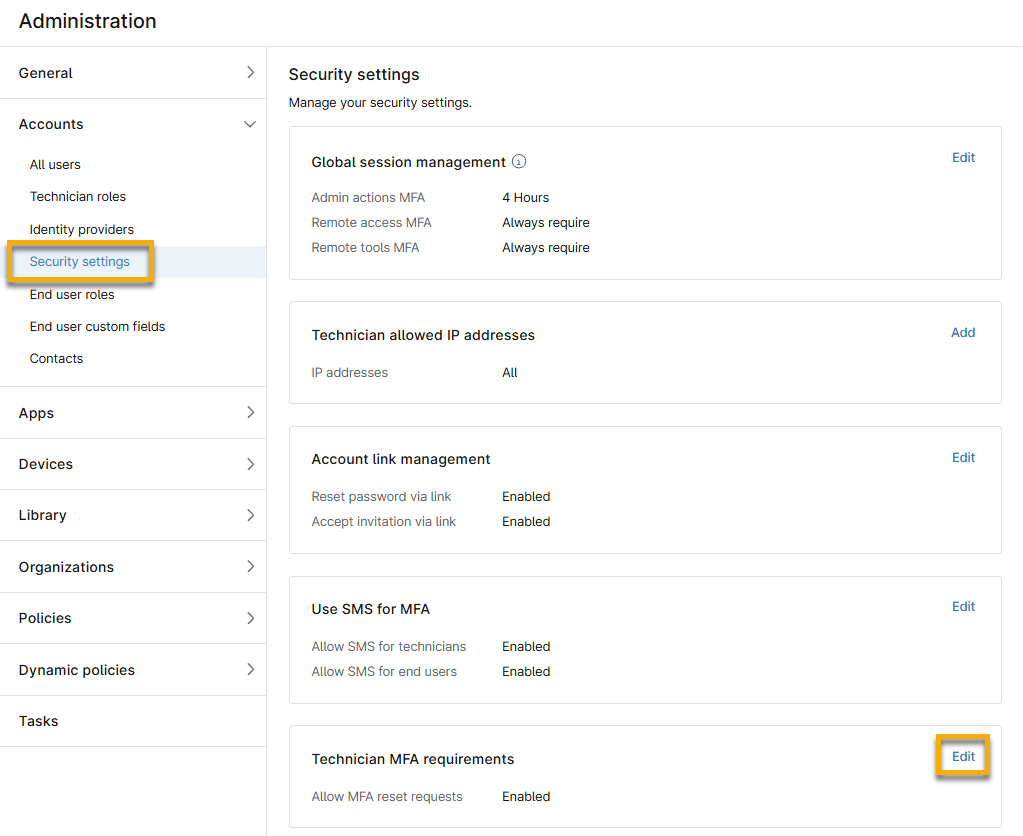
- Activate the Allow MFA reset requests toggle.
- Click Update.
To perform the MFA reset request:
During login, after submitting your username and password, click the Request MFA reset hyperlink.

Activating or Deactivating Technician Recovery Codes
A system administrator controls whether technicians receive recovery codes for your organization. The Allow technician recovery codes setting appears in the same Technician MFA requirements section.
To activate or deactivate recovery codes, perform the following steps:
- Navigate to Administration → Accounts → Security Settings.
- Click Edit in the Technician MFA requirements section.
- Activate or deactivate the Allow technician recovery codes toggle. If you deactivate it, confirm the warning that appears.
- Click Update.
After you activate the setting again, the NinjaOne platform will prompt technicians to save new recovery codes the next time they log in. The NinjaOne platform records each change to the setting in the activity log.
Additional Resources
For a list of frequently asked questions about MFA in NinjaOne, refer to Multi-Factor Authentication: Frequently-Asked Questions (FAQ).