


Key Points
- Vulnerability management is a continuous, proactive process that follows four steps: locate and identify, evaluate, remediate and monitor, and confirm.
- The vulnerability management lifecycle has five stages (assessment, prioritization, resolution, verification and monitoring, and reporting and improving), plus an optional planning stage that defines stakeholders, resources, and success metrics.
- Prioritization ranks each known vulnerability (CVE) by its Common Vulnerability Scoring System (CVSS) score, potential impact, and likelihood of exploitation, and filters out false positives.
- Common program components include asset discovery and inventory, vulnerability scanning, configuration management, penetration testing, threat intelligence, patch management, IT automation, and reporting tools. Teams adapt the mix to the needs of their organization.
- A vulnerability management program supports compliance with frameworks such as PCI DSS, HIPAA, NIST, ISO 27001, and GDPR, and helps reduce incident recovery time.
Vulnerability management is the ongoing process of finding, prioritizing, fixing, and verifying security weaknesses across your IT environment. Teams repeat it as a cycle because new vulnerabilities appear whenever software changes. This guide covers the core steps, the five lifecycle stages, the main components, and the benefits for IT teams and MSPs.
Explore NinjaOne Endpoint Management
Unify visibility and control across all devices to reduce complexity, improve efficiency, and strengthen security all from a single console.
Learn more
What is vulnerability management
Vulnerability management is a proactive, evolving practice that scales with your IT stack and emerging threats. Four key steps exist in every successful vulnerability management process:
- Locate and identify: Find vulnerabilities across your assets.
- Evaluate: Assess gaps and prioritize them.
- Remediate and monitor: Remediate the threat and monitor impacted systems.
- Confirm: Validate whether the vulnerability has been contained or mitigated as intended.
These procedures are all essential to planning and implementation. You can learn more about them in this comprehensive “4 Key Steps of a Vulnerability Management Process” guide.
Understanding the vulnerability management framework
A vulnerability management system isn’t just a tool or set of procedures to be used in an emergency; it’s proactive and ongoing. It’s a lifecycle as much as it is a framework, which begins, like all great schemes, with planning and improves upon it with continuous application and documentation. Then, of course, all of that work feeds into a fresh round of assessment and adaptation. Together, these stages form a cycle.
Some of the core features to consider for your vulnerability management system are as follows:
- Asset discovery and inventory
- Vulnerability scanning
- Configuration management
- Penetration testing
- Threat protection and intelligence
- Patch management
- IT automation system
- Dashboards and reporting tools
These features may be adapted or changed according to your organization’s needs. An Endpoint Management solution, which consolidates many of these features in a single platform, is also available to make the integration easy for complex or distributed IT networks.
5 stages of a vulnerability management lifecycle
Adding to that, a typical round of a vulnerability management lifecycle has five stages.
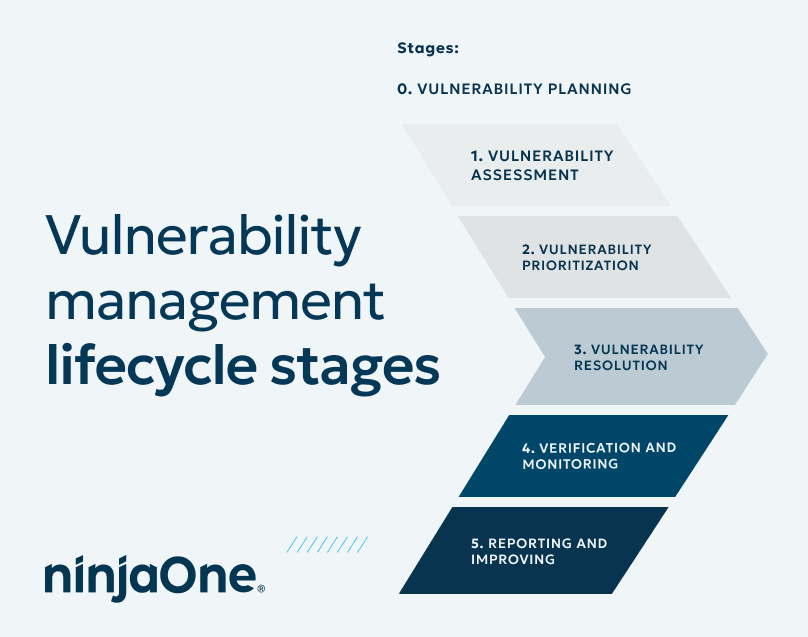
0. Vulnerability planning
During this ideation stage, you and your IT team discuss the details of your vulnerability management process, including which stakeholders will be involved, the resources required, your action plans and response strategies, and any metrics for success.
We’ve labeled this as the “0” step because this stage does not need to be repeated before every round of the cycle. That said, regularly revisiting vulnerability planning is still a good practice to ensure your vulnerability management framework remains effective.
1. Vulnerability assessment
The cycle formally kicks off with vulnerability assessment, including an asset inventory of all hardware and software in your IT network. After identifying your assets, you can assess each for its vulnerabilities using vulnerability scanners, pen tests, and external threat intelligence.
2. Vulnerability prioritization
To rank vulnerabilities by criticality, score each one on four factors: its Common Vulnerabilities and Exposures (CVE) record, its Common Vulnerability Scoring System (CVSS) severity score, its potential impact on the business, and the likelihood that attackers will exploit it. Remove false positives before you assign remediation work.
During this stage, your security team will prioritize the vulnerabilities analyzed from the previous stage. This step ensures that the most critical vulnerabilities are remediated first. To measure high criticality, consider its patch common vulnerabilities and exposures (CVE), its potential impact, the likelihood of exploitation, and weeding out any false positives.
3. Vulnerability resolution
After you prioritize, you have three options for each vulnerability: remediate it (for example, by applying a patch), mitigate or contain it with a compensating control, or accept the risk. Accept the risk only when the impact is low or the fix costs more than the exposure, and document the decision.
4. Verification and monitoring
The security team rescans and retests the assets they’ve just worked on. This process verifies that your resolution efforts worked as intended and ensures that they did not introduce new problems.
This stage also implements regular monitoring, which creates opportunities to look for undiscovered vulnerabilities, old resolution actions that may have grown obsolete, and any other actions that may require changes or updates.
5. Reporting and improving
At the end of each vulnerability management cycle, your security team must document its results, including any identified vulnerabilities, resolutions taken, and their outcomes. These reports must be shared with relevant stakeholders.
More importantly, you must use this new data to strengthen your processes and address emerging threats.
Why is vulnerability management important?
Threat actors continuously attempt to exploit weaknesses in IT environments. Though managing these IT vulnerabilities may take a lot of time and effort, it is essential for your organization’s cybersecurity.
Although most companies may survive a data breach incident, the repercussions remain costly when customer data is involved. A ransomware attack on an MSP can lead to years of litigation and a hefty fine from regulators if proven liable.
Having a vulnerability management system should be among the highest priorities of organizations, especially within IT environments. Skybox Security reports, “Vulnerabilities have more than tripled over the past ten years.” They also report that cybercrime continues to evolve and become more complex.
Verizon’s 2026 Data Breach Investigations Report found that exploiting vulnerabilities is now the leading way attackers gain initial access, ahead of phishing and credential abuse, at about 31%. The same report found that organizations fully remediated only about 26% of the vulnerabilities in the Cybersecurity and Infrastructure Security Agency’s (CISA) Known Exploited Vulnerabilities (KEV) catalog, down from 38% the year before.
Key benefits of vulnerability management
A vulnerability management system enables businesses of all sizes across all industries to identify and address potential security issues before they have any significant organizational impact.
By preventing data breaches and other security weaknesses, a vulnerability management system can prevent financial and reputational damage to the organization. Some other benefits include:
Improved security and control
Creating an effective vulnerability management plan can improve your overall security posture. For one, it helps establish an adaptable threat prevention strategy, which should identify and diagnose vulnerabilities before attackers can exploit them. Furthermore, the system can be leveraged to enforce internal policies and meet regulatory compliance.
Visibility and reporting
Vulnerability management provides centralized, up-to-date reporting on the status of your current security protocols and infrastructure. In addition, security automation can provide a comprehensive and real-time look at your IT network, boosting your coverage and response times to IT-related incidents.
Operational efficiencies
Businesses can strengthen their operational efficiency by decreasing the amount of time required to recover from an incident if it occurs. Having a system that can identify threats early means there will be fewer reactive and urgent fixes, which are both prone to risks.
Automation opportunities also significantly contribute to this area, as these solutions help streamline workflows and facilitate resource optimization.
Regulatory and standards compliance
A vulnerability management system supports frameworks like PCI DSS, HIPAA, NIST, ISO 27001, and GDPR. As a result, it provides great value for multinational organizations and those working in tandem with global partners. This approach also boosts brand reputation and actively helps in avoiding fines and sanctions.
Understand risk before it strikes. Watch: What is vulnerability management? How to reduce vulnerabilities (Video) now.
Start a free trial of the #1 endpoint management software on G2
No credit card required, full access to all features.
How NinjaOne fits into your vulnerability management process
NinjaOne unifies IT to simplify work for nearly 40,000 customers in 140+ countries. The NinjaOne Vulnerability Management solution shows CVE data for managed endpoints on NinjaOne dashboards, and NinjaOne Autonomous Patch Management helps teams remediate those vulnerabilities with automated patching across Windows, macOS, and Linux from one console. Teams that already run a supported third-party vulnerability scanner can import its scan data into NinjaOne with the Vulnerability Importer.
If you’re ready, request a free quote, sign up for a 14-day free trial, watch our vulnerability importer demo, or watch an autonomous patch management demo.