MDM software for Android with NinjaOne MDM
NinjaOne MDM configures and secures Android devices at scale, with remote actions to protect company data if a device is lost or compromised.
NinjaOne MDM configures and secures Android devices at scale, with remote actions to protect company data if a device is lost or compromised.

The following problems describe common friction points in managing Android devices at scale, and how NinjaOne MDM addresses them.
Problem | How NinjaOne resolves it |
Manually configuring each Android device one at a time doesn’t scale as a fleet grows, especially across a mix of company-owned and BYOD devices. | Once enrolled, managed Android devices are configured through policies that scale across the fleet, allowing consistent configuration, including installed software, regardless of how many devices are added. |
A lost or stolen Android device puts company data at risk for as long as it takes IT to notice and respond. | NinjaOne MDM lets administrators remotely lock or wipe an Android device the moment it’s reported lost or stolen, limiting the window of exposure. |
Allowing employees to install any app on a company-connected Android device increases the risk of malware or data leakage, but blocking all installs makes devices harder to use. | NinjaOne MDM lets administrators control which apps can be installed, blocking or removing unauthorized apps while deploying approved ones through Google Play. |
Supporting a remote or field employee’s Android device without physical access to it can turn a simple fix into a lengthy back-and-forth. | Android Remote Control in NinjaOne MDM lets technicians remotely control a managed Android device, similar to a managed laptop, to resolve issues without needing the device in hand. |
The following features describe how NinjaOne MDM supports Android device management.
Once enrolled, Android devices are configured through policies that scale across the fleet, keeping settings and installed software consistent regardless of how many devices are added.
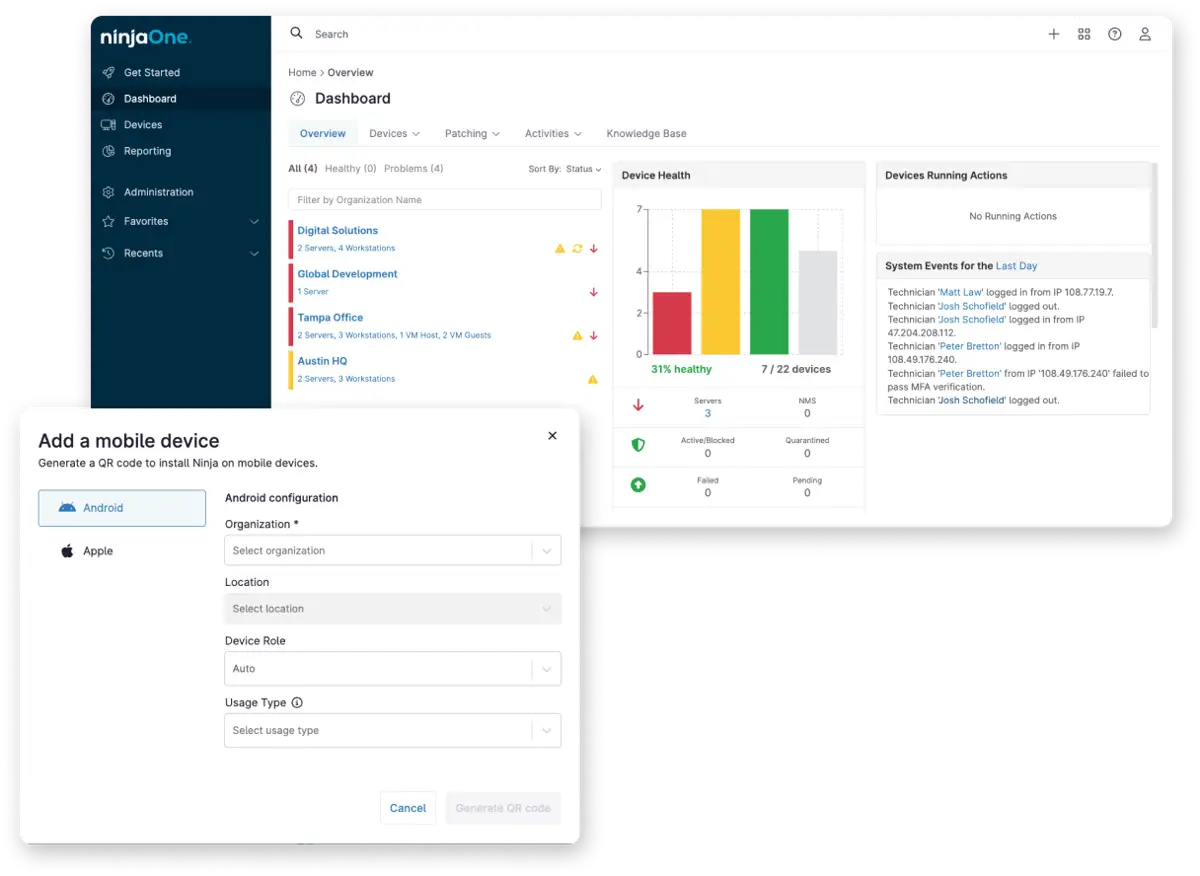
Android devices can be enrolled manually by scanning a QR code, through zero-touch enrollment for devices registered by an authorized reseller, or via Samsung Knox Mobile Enrollment for supported Samsung devices. Each enrollment uses one of three default profiles, for an end-user device with personal use allowed, an end-user device with no personal use allowed, or a dedicated device with no specific user, or a custom profile based on them.
Administrators can block or remove unauthorized apps and deploy approved ones through Google Play, keeping installed software consistent with company policy. Administrators can also enforce device restrictions and app-level encryption, reducing the risk of unauthorized access to company data.
Administrators can remotely lock or wipe an Android device the moment it’s reported lost or stolen, limiting how long company data stays exposed.
Technicians can remotely control a managed Android device, similar to a managed laptop, to resolve issues without needing the device in hand.
Administrators can see a managed Android device’s last known location to support recovery efforts or inform a lock or wipe decision; location tracking requires the NinjaOne Assist app installed and running on the device. For company-owned or supervised devices, administrators can also put the device into Lost Mode, locking it and displaying a custom message or contact information on the screen.

Because devices are configured through policy once enrolled, settings and installed software stay consistent no matter how many devices join the fleet.

Zero-touch enrollment and Samsung Knox Mobile Enrollment get new or factory-reset Android devices into policy without configuring each one by hand. (Zero-touch enrollment requires eligible devices to be registered by an authorized reseller.)

Because IT controls which apps can be installed through Google Play, the fleet stays free of software that could introduce security or compliance risk.

Combining location tracking, remote lock/wipe, and Lost Mode lets IT act within minutes of a device going missing, rather than leaving data exposed indefinitely.

Android Remote Control lets technicians resolve issues on a managed device remotely, cutting down on time lost coordinating with the end user or waiting for the device to be brought in.

The following practical applications describe how NinjaOne MDM supports Android device management in real-world IT and MSP environments.

When a company orders a batch of new Android phones or tablets for a new office or department, zero-touch enrollment and policy-based configuration get every device fleet-ready without IT touching each one individually.

Employees using Android devices in the field, such as delivery drivers or retail staff, can get remote troubleshooting through Android Remote Control without having to bring the device back to IT.

When an employee reports an Android device missing, IT can locate it, lock it with Lost Mode, or wipe it outright, depending on the situation and how sensitive the data on it is.
Here’s how Android device management is set up and used in NinjaOne MDM, at a high level.
Administrators enable NinjaOne MDM and connect it to Android Enterprise using a managed Google account.
Administrators configure policies covering app restrictions and deployment through Google Play, encryption, passcode requirements, and other settings, before enrolling devices.
Devices are enrolled manually by scanning a QR code, through zero-touch enrollment for new or factory-reset devices registered by an authorized reseller, or through Samsung Knox Mobile Enrollment for supported Samsung devices, using one of the three default NinjaOne MDM enrollment profiles or a custom profile based on them.
IT tracks device status, location, and health from the same console used for other endpoint types.
Administrators can enable Lost Mode, remotely lock or wipe a device, or use Android Remote Control to resolve issues. Software and restrictions are also added, removed, or adjusted on an ongoing basis as needs change.
As mobile devices became a bigger part of the employee ecosystem, Vetcor turned to NinjaOne MDM to manage the tablets used by its marketing and recruiting teams. If a tablet goes missing, IT can quickly lock it down or wipe it clean.
"Continuing to have our tools in a single pane saves my technicians time,"
said Ernie Turner, Director of IT, Vetcor.
Source: Vetcor – NinjaOne Customer Story
100,000
Endpoints managed
“NinjaOne is a scalable solution. It’s built on a modern SaaS architecture and it’s future-proof.”
40%
More Cost Effective
“NinjaOne’s price point is 40% less than any other endpoint management tool on the market, while being more powerful and easy to use.”
10-15
Tools Replaced
“Before, I needed 10-15 different tools to execute what NinjaOne does in its centralized, single pane of glass.”
30%
Less time for patching
“We observed a 30% reduction in the time taken for patch deployments compared to our previous solution.”
2,000
Endpoints managed
“NinjaOne gives me much more flexibility and security in my work”
30%
Annual ROI
“[NinjaOne] has already shown its value in ROI…it’s at least a hundred thousand dollars annually.”
24x
Faster Endpoint Management
“Our processes have become 24x faster with NinjaOne.”

20-40
Hours Saved Each Week
“Leveraging the automations feature within NinjaOne has enabled me to save upwards of what would likely be 20 to 30 to even 40 hours per week.”
See how NinjaOne MDM configures and secures Android devices from one console.
NinjaOne MDM enrolls, configures, and secures Android devices through policy, keeping settings and installed software consistent across the fleet. Administrators can also take remote action, such as locating, locking, or wiping a device, from the same console used for other endpoint types.
Devices can be enrolled manually by scanning a QR code, through zero-touch enrollment for new or factory-reset devices registered by an authorized reseller, or through Samsung Knox Mobile Enrollment for supported Samsung devices.
Yes. Administrators can block or remove unauthorized apps and deploy approved ones through Google Play, keeping installed software consistent with policy.
Yes. Administrators can remotely lock or wipe the device, or use Lost Mode to lock it and display a custom message or contact information on the screen. Lost Mode itself is limited to company-owned or supervised devices.
Yes. NinjaOne MDM shows a device’s last known location, helping IT decide whether to attempt recovery or move straight to locking or wiping it. This requires the NinjaOne Assist app installed and running on the device. On BYOD devices, the end user must manually grant location permission to the Assist app before tracking will work.
Yes, through Android Remote Control. Technicians can remotely control a managed Android device, similar to a managed laptop, without needing the device in hand.
Yes. NinjaOne MDM includes default enrollment profiles suited to different ownership models: an end-user device profile that allows personal use (fits BYOD), an end-user device profile with no personal use allowed, and a dedicated device profile with no specific user (fits company-owned, single-purpose devices). Administrators can also create custom profiles based on these three.
On a BYOD device, NinjaOne MDM creates and manages an isolated work partition on the device, keeping company apps and data separate from personal apps and data. Administrators can only see and manage what’s inside that work partition. On a company-owned device, NinjaOne MDM manages the entire device, giving administrators full visibility and control rather than being limited to a work partition.