Key Points
- Server patching is the process of applying patches to update or fix server software.
- Patching a server system is important because it ensures it successfully stores, sends, and receives data over the network and into your connected endpoints.
- Unpatched servers leave the network open to security vulnerabilities, productivity loss, and risk of non-compliance.
- IT teams often use endpoint management platforms with autonomous patch management, such as NinjaOne, to detect, prioritize, and deploy updates across servers and other endpoints.
Patch management is a critical process in IT-powered environments. Server patching, in particular, is crucial to keeping these endpoints performing well and secure. Follow this guide to learn how server patch management works and how to best execute it at scale within regulatory compliance.
Want to understand server patching more? Watch our visual guide: What is Server Patching & Why It’s Important.
What is server patching?
Server patching is the process of applying patches to update or fix your server software. Patching is needed to support the successful operation of your servers and verify that they’ll be able to perform their specific functions.
It’s an iterative process that’s often completed upon availability, though it may also be delayed or ignored with varying risks and consequences.
Read: Check out this deeper look at the risks of delayed patching.
Streamline your server patch deployment process with NinjaOne.
Why is server patch management important?
Patching a server system ensures it successfully stores, sends, and receives data over the network and into your connected endpoints. A server with poor health and tuning will be unable to provide its designated services or functions.
Security protection
Attackers are known to exploit vulnerable servers and other endpoints. Regular patching closes these gaps that could otherwise be an entry point for malware, ransomware, or rogue users.
System stability
Patches don’t just address security gaps; they also fix bugs and defects that can cause crashes, performance degradation, or downtime. As far as servers go, high availability is a must for business continuity and compliance.
Read: Check this guide on minimizing downtimes for more tips.
Regulatory compliance
Many industries (e.g., finance, healthcare, government) need up-to-date patching as a key component of data protection and security frameworks. Failure to meet IT compliance can lead to hefty fines and reputational damage.
Operational continuity
Automated patching mitigates the risk of outages caused by known software issues, ensuring servers run smoothly with minimal disruption.
At scale, this is typically achieved with enterprise IT management tools or an RMM with autonomous patch management capabilities like NinjaOne.
Apart from operational integrity and compliance, patches enhance efficiency, optimize processes, or improve software compatibility among various systems. Regular patch management also significantly minimizes the number of entry points that threat actors can exploit across servers.
Common risks of unpatched systems
Risks that are associated with an unpatched server are the same risks that other types of unpatched software face, including:
- Loss of data
- Lost productivity
- Security vulnerabilities and weakened security posture
- Suboptimal network conditions
- Non-compliance with regulatory and industry standards
When the server is unpatched, it is less resistant to cyber threats. Unpatched software can also have a noticeable impact on productivity, especially in industries or environments that have fully integrated IT workflows.
Tip: Check out these IT horror stories and learn how unpatched software can hurt your business.
3 keys to a successful server patching process
Servers are more heavily configured and more sensitive, which means that the impact of them going down is much worse. If a patch breaks a user’s machine, the user might lose a day of work, but it’s not the end of the world. If you break a server with a patch, all members of your organization might be unable to work for an entire day. The effects are much larger, so server patching has much higher stakes.
There are three keys to a successful server patch. We’ll go through each in this section, but you can refer to the table below for a quick summary:
| Key | What it does | When it applies |
| Combine automatic and manual processes | Automation tracks and scans available patches, while humans validate and implement them | Every patch cycle |
| Use a sandbox to test server patches | Evaluates patches in a non-production environment before they touch live servers | Before each server deployment |
| Implement server failovers | A standby server automatically takes over if a patch breaks the production server | Always-on safeguard |
1. Combine automatic and manual processes
Patch management benefits from automation, though not every step should be automated.
Automation can be used for tasks such as tracking available patches and scanning them, but manual testing and implementation remain key to ensuring patches positively affect server performance.
2. Use a sandbox to test server patches
Before you deploy a patch to your server, you want to make sure it actually improves the system rather than breaking it. Sandbox testing allows you to evaluate any available patches without disrupting the live environment.
A sandbox is a non-production environment that allows you to safely test potential patches before they’re applied to production, which in this case is a server.
3. Implement server failovers
As a general rule of thumb, you should have backups in your IT environment wherever possible. Server backup is a server failover.
The server failover or failover cluster is programmed to automatically take control and replace the original server if it goes down, is offline, or another disaster breaks the system.
The general approach to server patching is very different from the approach to patching end-user devices. With end-user devices, the goal is to get them protected as quickly and efficiently as possible.
Server patching, in comparison, thrives in a more conservative approach. Likewise, it’s typically more difficult and time-consuming. Autonomous and manual processes are also both required to deliver consistent and stable outcomes.
Tip: For additional insights, check out this collection of patch management best practices.
Thousands of customers worldwide trust NinjaOne for their patching needs.
Learn more about NinjaOne Server Patching.
Patch your servers with confidence using NinjaOne
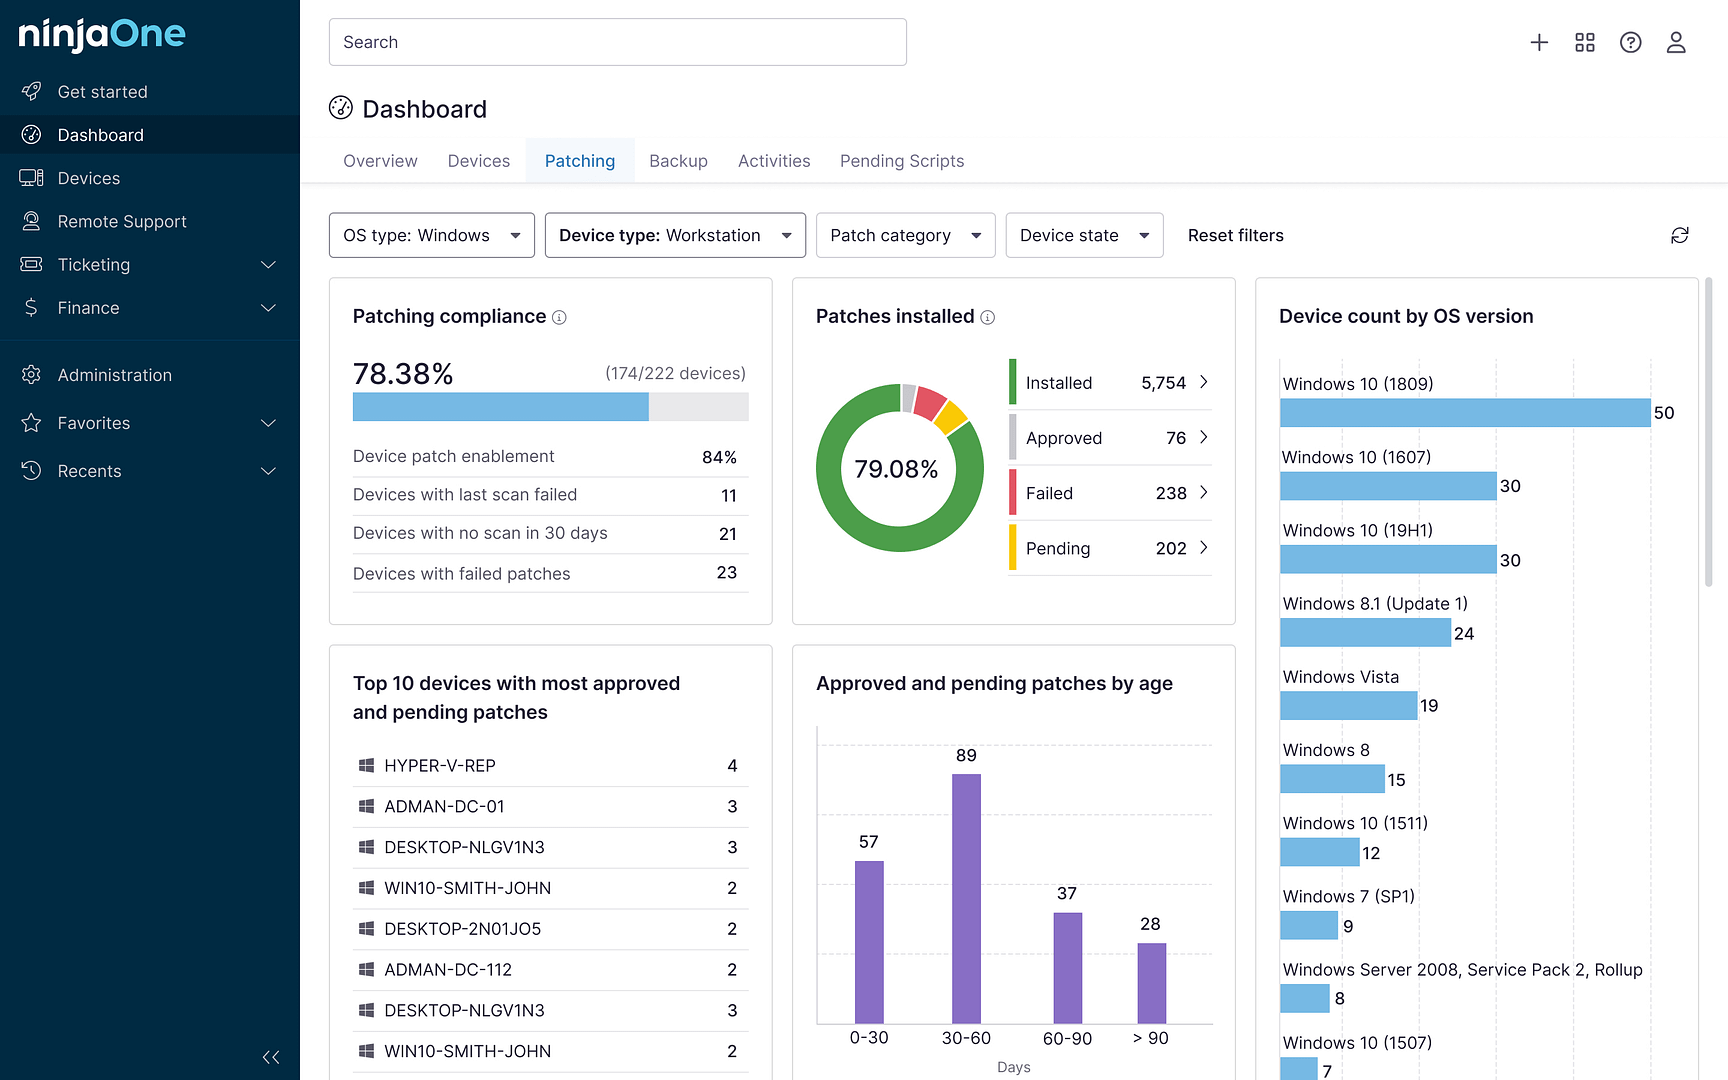
NinjaOne provides patch management software that gives you the tools for effective server patching at scale. It enables automated remote patch management, monitors your servers’ patch status on a unified dashboard, and provides regular patch reporting and visibility over servers and endpoints across your IT environment.