


Key Points
- Cybercrime costs are surging globally, projected to reach $10.5 trillion in 2025 and up to $12.2 trillion by 2031, with ransomware and data breaches driving the majority of financial and operational damage.
- Ransomware and phishing dominate cyber threats, with ransomware present in 44% of breaches and phishing accounting for up to 85% of attacks on UK businesses, making them the most critical risks to mitigate.
- Cyberattacks are constant and escalating, with 450,000+ new malware samples detected daily and predictions that a ransomware attack will occur every two seconds by 2031, highlighting the scale of global cybersecurity threats.
- UK and US organizations face high-frequency, high-cost attacks, including millions of annual cybercrimes in the UK and average US data breach costs exceeding $10 million, the highest globally.
- Cybersecurity readiness gaps remain widespread, as many SMBs lack cyber insurance or adequate defenses, leaving businesses vulnerable to phishing, malware, and repeat attacks that cause significant financial loss and reputational damage.
In 2025, the cost of cybercrime is estimated to have reached $10.5 trillion and is expected to increase to $12.2 trillion by 2031, according to Cybersecurity Ventures. In Verizon’s latest Data Breach Investigations Report, 44% of data breaches reviewed have ransomware present, up from 32% the previous year. This demonstrates the widespread and severe challenge of cyber threats that businesses and individuals around the world must contend with. These incidents often lead to substantial financial losses, reputational damage, and significant operational disruptions.
This article examines the latest statistics on cybersecurity threats in the UK and the US, exploring costs, methods, emerging trends, and discovering the prevalence of these types of crimes.
Minimize exposure from cyber threats with real-time endpoint visibility.
Cybersecurity statistics: Editor’s picks
- Businesses in the UK are targeted by an average of 1,988 cyberattacks daily during the first quarter of 2026. While this represents a 2% decrease from the previous quarter, this figure is still high and almost equal to that recorded in the same period in 2025. (Beaming)
- Over 41 million phishing emails have been reported to the Suspicious Email Reporting Service (SERS) of Action Fraud, the UK’s national fraud center, since its launch in April 2020 (Action Fraud; Bitdefender; WiredGov).
- About 1 in 5 consumers fell victim to scams, particularly phishing links (Norton).
- The average cost of the most disruptive breach or attack for each business in 2025 was £1,600. Excluding those with £0 in losses, this figure rises to £3,550. (UK Government cyber security breaches survey 2025).
- The US has the highest data breach costs of all countries worldwide, averaging $22 million in 2025, a record high and a 9% increase from 2024 (IBM Cost of a Data Breach Report 2025).
- 82% of US businesses with 500 or fewer employees do not have a dedicated cyber insurance policy (Insurance Business).
Global cybercrime statistics: how many cyber attacks happen per day worldwide?
Increasingly often, we hear about large companies having their data breached in the news. But just how regularly do these types of attacks take place? And what does this look like in the US vs the UK?
- More than 450,000 new pieces of malware are detected every day worldwide (AV-TEST).
- Around 6 billion malware attacks were detected worldwide in 2023 (Statistica).
- By 2031, a ransomware attack will occur on a business, consumer, or device every two seconds (Cybersecurity Ventures).
How common is cybercrime in the UK?
Do cybercrimes occur regularly in the UK? How often are they reported? And what’s the average financial loss of a cybercrime victim? Here’s everything you need to know:
- The UK government’s most recent report estimates that in 2024-25, UK businesses experienced approximately 58 million cybercrimes of some form.
- Even still, the year ending September 2025 saw approximately 686,000 reports of computer misuse* in England and Wales (down 21% from 867,000 in 2024) (Office of National Statistics).
*A Computer Misuse Offense refers to the deliberate or reckless obtaining, disclosing, procuring and retention of personal data without the consent of the data controller (Crown Prosecution Service)
Cybercrime attacks on individuals in the UK
As well as targeting businesses, many cyberattacks also target individuals, taking the form of phishing emails, malware-laden attachments, and social engineering tactics designed to steal personal information, financial data, or identities. Our analysis of cyber-enabled crime data from Action Fraud (the UK’s national reporting center for fraud and cybercrime) found that:
- From June 2022 to May 2023, there were 200,000 reports of cyber-enabled crimes against individuals in the UK.
- These crimes resulted in financial losses of over £890 million (an average of £4,500 per individual).
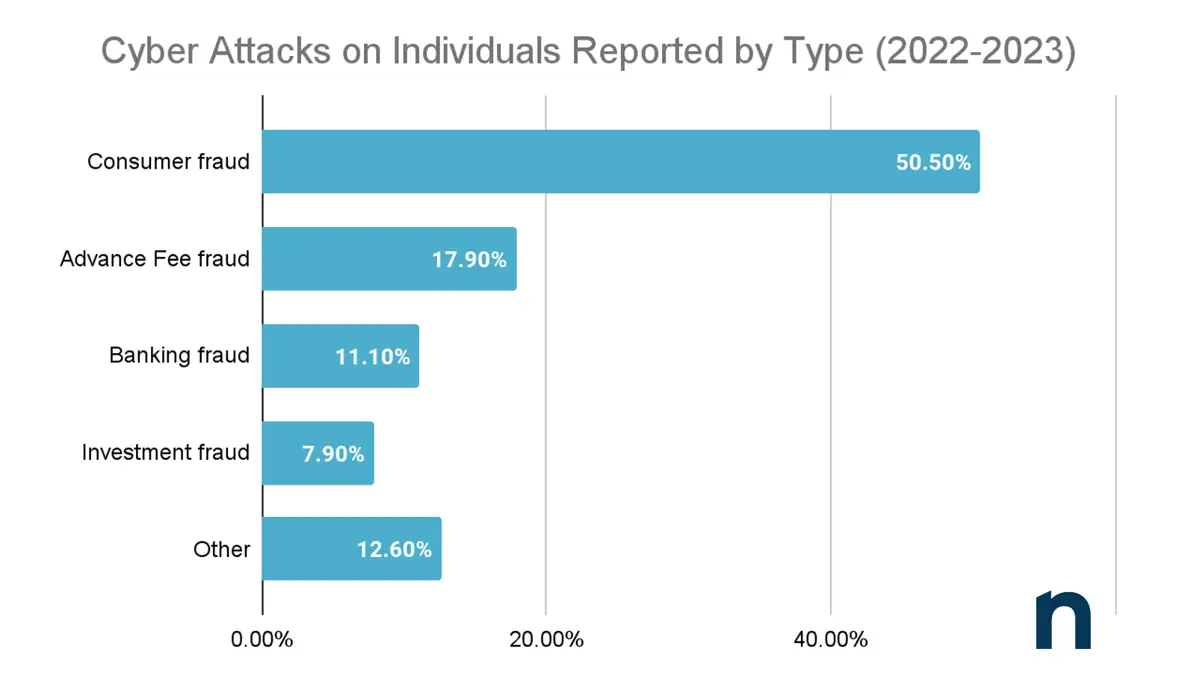
- The most common types of cyber attack reported to Action Fraud by individuals between June 2022 and May 2023 were consumer fraud (50.5%), advance fee fraud (17.9%), and banking fraud (11.1%).
- 20-29 year-olds were the most likely to file reports of cybercrimes, with more than 1 in 5 people in this age group (20.4%) making a report of some kind.
Repeat cyber attacks
Our analysis of data from the Crime Survey for England and Wales found that many individuals who fall victim to cyber attacks do so on multiple occasions. In fact:
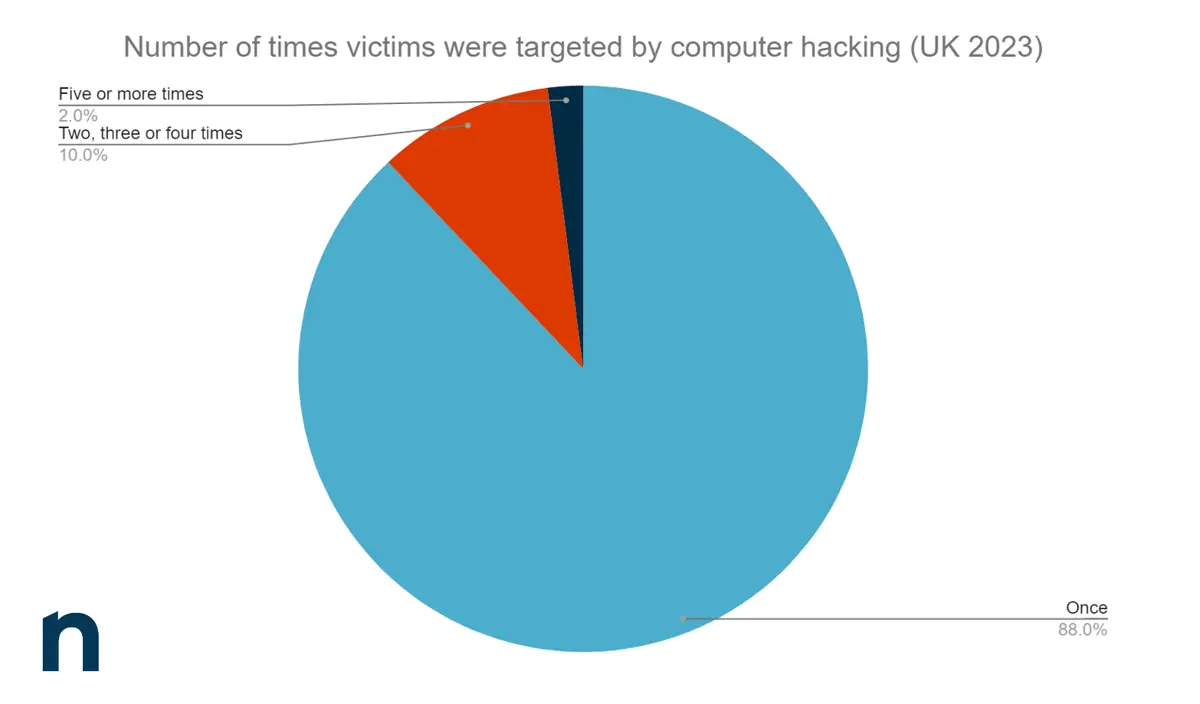
- When it comes to individuals who’ve had their personal information breached or hacked by an unauthorized person, 10% experience this again 2, 3, or 4 times, and 2% experience this on 5 or more occasions.
| Unauthorized access to personal information (including hacking) | |
| Number of times targeted | Percentage |
| Once | 88 |
| Two, three or four times | 10 |
| Five or more times | 2 |
- A similar story can be seen with cyber attacks in the form of computer viruses, with 12% of victims experiencing repeat offenses 2, 3, or 4 more times after the initial attack.
| Computer virus attacks | |
| Number of times targeted | Percentage |
| Once | 88 |
| Two, three or four times | 12 |
| Five or more times | 0 |
Cybercrime attacks on UK businesses: the statistics
How many UK businesses are affected by cybercrime? And what impact does this have? Our research found:
- The government’s most recent report revealed that in 2024, nearly a quarter of businesses (20%) and 14% of charities experienced at least one cybercrime within the 12-month period.
- Medium and large businesses were found to be the worst affected (42% and 52%, respectively).
| Business size | Percentage that experienced cybercrime in the 12 months leading up to December 2024 |
| Micro businesses | 18% |
| Small businesses | 25% |
| Medium businesses | 42% |
| Large businesses | 52% |
- The most common form of cyber attack on UK businesses in 2024-25 is phishing, with 85% of businesses that experienced cybercrime reporting incidents of this nature.
How common is cybercrime in the US?
So how about the United States? What impact has cybercrime had on businesses and individuals across the country? Let’s jump straight into the numbers:
- According to IBM’s latest Cost of Data Breach report, in 2023, the United States had the highest data breach costs of all countries worldwide for the 14th consecutive year.
- This averaged $22 million (up 9% from the previous year), and was followed by the Middle East, Canada, Germany, and Japan.
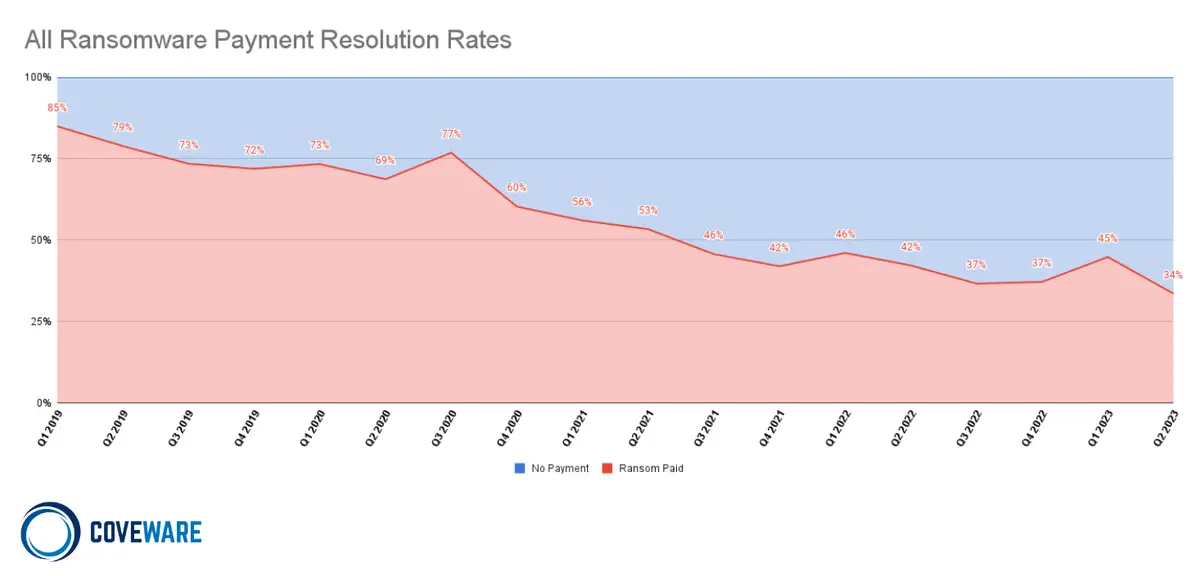
- Interestingly, though, 63% of ransomware victims did not pay the ransom (an increase from 59% in 2024), while 37% of them did (a decrease from 41% in 2024).
Cybercrime attacks on individuals in the US
Although they tend to be on a much smaller scale, cybercrimes against individuals can have a significant emotional impact. The fear of identity theft, loss of personal data, and frustration of dealing with compromised accounts can really take its toll. But just how much are people in the US affected by these types of attacks?
- A survey conducted on behalf of Anomali by The Harris Poll found that over a fifth of US adults (21%) have experienced a ransomware attack on a personal and/or work device.
- Amongst those who experienced an attack on a work device, 46% say their company paid the ransom.
- The survey found that just 51% of US adults believe the government is effectively addressing the issue of cybersecurity.
- And that 61% would support a federal income tax increase to help fund government efforts to defend against cyberattacks.
Cybercrime on US businesses and organizations: the statistics
Now let’s talk business. Just how many US businesses have been subject to cyber attacks? And what impact does this have?
- Emsisoft’s The State of Ransomware in the U.S. report revealed that in 2024 alone, 1,031 hospitals, 116 K-12 school districts, and 117 government entities were directly impacted by ransomware, alongside thousands of private sector businesses.
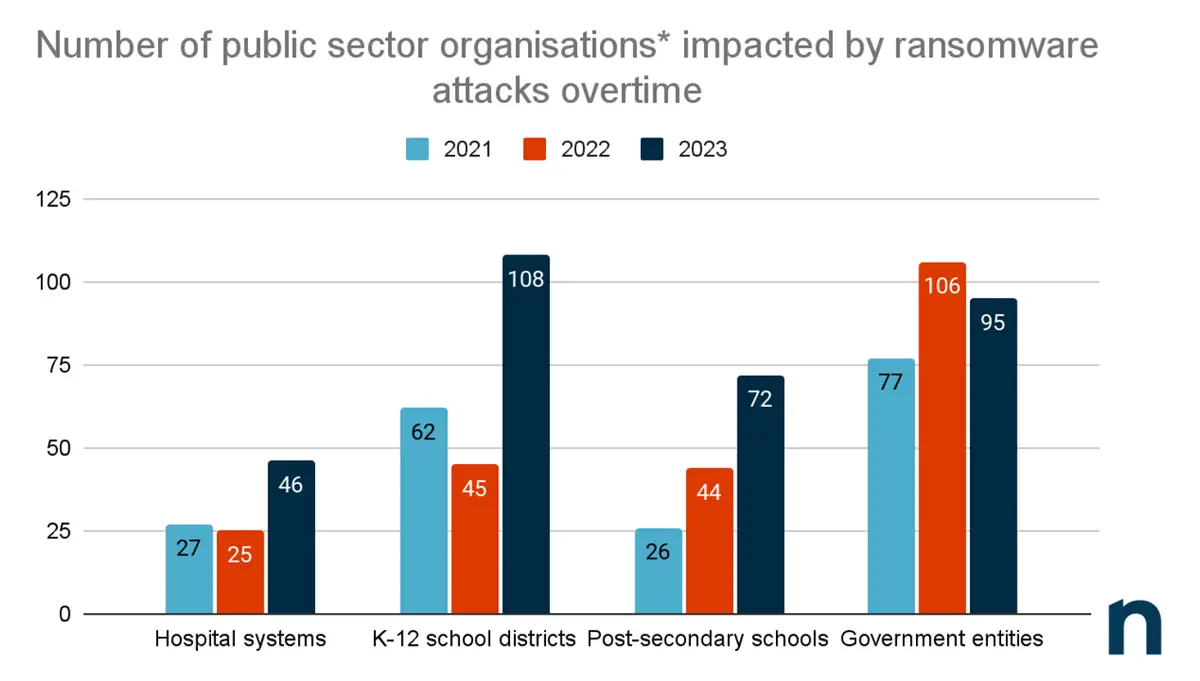
*Hospital systems are comprised of multiple hospitals and school districts of multiple schools. The total number of hospitals and schools impacted is explained in the sector-specific sections below.
- One of the most recent, largest-scale data breaches in the US was that of the State of Maine, who suffered a data breach in May 2023 that led to the loss of over a million citizens’ data.
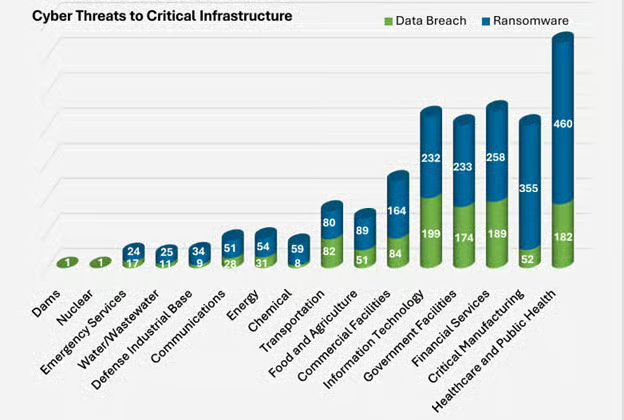
- According to the FBI IC3 2025 Annual Report, healthcare is the most vulnerable infrastructure sector by far, with 460 reported ransomware incidents and 182 data breach incidents; this is followed by critical manufacturing (355 ransomware, 52 data breach), financial services (258 ransomware, 182 data breach), and government facilities (233 ransomware, 174 data breach).
- Change Healthcare was the victim of a ransomware attack in April 2024, with an initial ransom of $22 million in Bitcoin. It is estimated that more than 90% of 70,000 pharmacies across the United States were compromised. This prompted Senators Elizabeth Warren, Bill Cassidy, and Richard Blumenthal to release a public demand to the Cybersecurity and Infrastructure Security Agency (CISA) to reveal their plans to prevent further attacks.
NationalPublicData.com hack
In 2024, reports have come out of a cybersecurity incident involving the National Public Data, an online background check and fraud prevention service in the United States. It is alleged that a cybercriminal group, USDoD, instigated the data leak, which exposed the personally identifiable information (PII), such as Social Security Numbers, names, and addresses, of around 2.9 billion people. The ransom was set for $3.5 million, but has since been offered for free in a dark web forum.
This has naturally sparked outrage for billions of people whose PII has now been compromised. As of the time of writing, there is now a class action lawsuit from the law firm, Schubert, Jonckheer & Kolbe.
Secure your reputation and your systems. Learn how to embed a security-first approach into your IT operations.
Are businesses prepared to defend against cybersecurity threats?
In 2022, BlackBerry and Corvus Insurance surveyed 415 IT and cybersecurity business decision-makers in North America and Canada, to find out more about how prepared they were to defend their business’ cybersecurity. The survey found:
- 45% of businesses do not have any cyber insurance cover whatsoever.
- Of those who do have coverage, more than a third (37%) aren’t covered for ransomware payments.
- Even amongst businesses that do have ransomware payment coverage, just 1 in 5 (19%) have limits greater than the median ransomware demand of $600,000.
- This figure drops even lower for SMBs with fewer than 1,500 employees (14%).
Most common types of cyber attacks
Given that so many individuals and businesses choose not to report incidents of cyber attacks to the authorities, it can be extremely difficult to determine just how often they occur and which types happen most frequently.
Regardless, reports such as the FBI’s annual Internet Cybercrime Report can still share insights as to what cybercrimes are most commonly reported to authorities.
In 2025 alone, the Internet Crime Complaint Center (IC3) received 1,008,597 complaints, marking the first time that the FBI division has received more than a million complaints in a single year.
Most reported cybercrime complaints by type
- Based on the IC3 report, phishing/spoofing is the most commonly reported cybercrime, with 191,561 complaints.
- This is followed by extortion (89,129), investment (72,984), and personal data breach (67,456).
| Cybercrime | No. of complaints |
| Phishing/spoofing | 191,561 |
| Extortion | 89,129 |
| Investment | 72,984 |
| Personal data breach | 67,456 |
| Non-payment/non-delivery | 56,478 |
| Tech/customer support | 47, 794 |
Note: The IC3 report emphasizes that complaint figures for ransomware (3,611) only represent those who have reported to the FBI via the IC3, and not to FBI field offices. Likewise, losses from ransomware are often underreported or not recorded at all in complaints, so figures in the report are estimated to be low.
Another alternative is keyword research. As we all know, when most of us (especially us tech heads) are unsure of something, what do we do?… That’s right, Google it! Therefore, we headed over to our trusty search volume analysis tool, Keyword Finder, to do some digging into which types of cyber attacks are Googled most often.
Note: Although people are searching for these terms, it doesn’t necessarily mean they’ve been targeted by these scams. They may simply be wishing to find information on the topic.
Most-searched cyber attack types in the US
- Our analysis found that in the US, the most-Googled type of cybersecurity threat in 2024 is phishing, with an average of 75,600 searches made for the term every month.
- This is followed by denial of service (40,200) and malware (38,700).
- With ransomware (30,800) and spoofing following close by (27,100).
| Keyword | Avg. Monthly Search Volume (US) |
| phishing | 75,600 |
| denial of service | 40,200 |
| malware | 38,700 |
| ransomware | 30,800 |
| spoofing | 27,100 |
| smishing | 24,200 |
| pretexting | 14,600 |
| vishing | 14,200 |
| dos attack | 11,100 |
| insider threat | 5,100 |
Top 10 most-Googled types of cyber attacks in the US (as of April 2024)
Most-searched cyber attacks in the UK
- Phishing is also the most-searched form of cyber threat in the UK, averaging 22,200 monthly searches.
- However, malware is the second-most searched (15,100), followed by ransomware (9,900).
- Closely behind are denial of service (9,600) and spoofing (5,200).
| Keyword | Avg. Monthly Search Volume (UK) |
| phishing | 22,200 |
| malware | 15,100 |
| ransomware | 9,900 |
| denial of service | 9,600 |
| spoofing | 5,200 |
| dos attack | 3,800 |
| smishing | 3,800 |
| vishing | 2,900 |
| pretexting | 1,800 |
| insider threat | 840 |
Top 10 most-Googled types of cyber attacks in the UK (as of April 2024)
Most widespread branded scams
One of the most convincing ways hackers or cyber scammers succeed in tricking companies and individuals is by posing as brands they trust. This can take many forms, from texts pretending to be your energy provider to emails from a social media site or streaming platform you use on a regular basis. But which of these are most common?
To find out, we used the Keyword Finder tool once more to analyze searches for scams relating to some of the UK and USA’s biggest brands.
Biggest branded scams in the US
- According to our analysis, the most-searched branded scam in the US is Facebook Marketplace, with 18,100 searches being conducted for the term on a monthly basis.
- This is followed by PayPal scams (14,100), Facebook (8,600) and Amazon (6,600).
| Keyword | Avg. Monthly Search Volume (US) |
| facebook marketplace scam | 18,100 |
| paypal scam | 14,100 |
| facebook scam | 8,600 |
| amazon scam | 6,600 |
| instagram scam | 5,800 |
| microsoft scam | 2,800 |
| tiktok scam | 1,400 |
| netflix scam | 1,400 |
| youtube scam | 950 |
| dropbox scam | 390 |
Complement your cybersecurity defenses with a unified endpoint management solution.
Biggest branded scams in the UK
- Back across the pond in the UK, the most-searched branded scam is also Facebook Marketplace, receiving an average of 8,800 searches per month.
- PayPal appears second once again (4,600), whilst Royal Mail comes in third with 4,300 average monthly searches.
| Keyword | Avg. Monthly Search Volume (UK) |
| facebook marketplace scam | 8,800 |
| paypal scam | 4,600 |
| royal mail scam | 4,300 |
| vinted scam | 3,300 |
| facebook scam | 3,000 |
| amazon scam | 2,200 |
| microsoft scam | 1,200 |
| instagram scam | 1,200 |
| santander scam | 950 |
| banking scam | 660 |
How NinjaOne keeps your data secure from cybersecurity threats
NinjaOne’s #1 RMM software solution has built-in tools that improve your endpoint security in a single pane of glass. With its platform, you can easily manage applications, remotely edit registries, deploy scripts, and, most importantly, immediately detect and remediate vulnerabilities and threats.
If you’re ready, request a free quote, sign up for a 14-day free trial, or watch a demo.