

Key Points
- Endpoint security monitoring gives MSPs continuous visibility into device health, risk, and threat activity across all client environments.
- A strong endpoint management service combines monitoring, patching, remote remediation, security controls, and client reporting under one workflow.
- Endpoint monitoring tools should turn raw device data into actionable alerts, tickets, and remediation workflows.
- Multi-tenant MSP monitoring software enables providers to manage many clients from one place without mixing data or compromising visibility.
- Endpoint monitoring works best when it’s connected to EDR, patching, backup, ticketing, and compliance reporting.
For many people, the primary role of a managed services provider (MSP) is to keep their client devices safe. And while this is correct in broad strokes, it doesn’t account for what that actually entails. It’s similar to saying croissant is bread, and while yes, it is, it is also completely different from the standard loaf of bread you buy in the supermarket.
Similarly, endpoint security monitoring, or the practice of continuously watching every laptop, desktop, server, and mobile device, extends far beyond just “keeping client devices safe.”
SentinelOne reports that 70% of successful breaches begin at endpoints. That means the devices your clients use every day, the ones running Windows updates, connecting to hotel WiFi, or sitting unattended after hours, are the most targeted entry points for threat actors. Even worse, Cybersecurity Ventures predicted ransomware trends would worsen in the coming years, especially as cybercriminals become more sophisticated. In fact, they project that the global cost of ransomware will reach $275 billion annually by 2031.
In this guide, we explain what endpoint security really is and how its tools are crucial for any organization, but particularly MSPs.
What MSP endpoint tools do
Think of MSP endpoint tools as the control tower for all your clients’devices. From one centralized platform, a good endpoint tool allows you to discover devices, monitor their health and performance, track patch compliance, respond to threats, and report back to clients, all without physically touching a single machine.
The core functions break down into four major areas.
1. Visibility
You can’t monitor what you don’t know exists. Visibility means having a complete, real-time picture of every device across your client environments, including data such as:
- What devices are on the network
- What operating system and software versions they’re running
- Whether their security agents are active and reporting
- Whether anything has changed since the last check
As you can imagine, visibility is foundational to any of the best endpoint monitoring software. An endpoint you can’t see is an endpoint you can’t protect, and in MSP environments, managing hundreds or thousands of devices across multiple clients, blind spots are where incidents start.
2. Security
Once you have a good understanding of your client environments, you can then act on possible security vulnerabilities. The security function covers:
- Detecting suspicious behavior
- Confirming that endpoint protection is active and current
- Flagging unpatched vulnerabilities before they are exploited
- Identifying other risky conditions like unauthorized software, missing encryption, or accounts with excess privileges.
It is at this function that endpoint monitoring becomes endpoint security monitoring, moving from passive inventory to active risk identification.
Knowledge check: Endpoint security monitoring vs. endpoint management vs endpoint monitoring
These terms are often used interchangeably, but they aren’t the same thing, and confusing them can lead to gaps in service.
| Endpoint security monitoring | Endpoint management | Endpoint monitoring | |
| Focus | Risk and threat identification | Maintenance and control | Device health and status tracking |
| Core question | “Is anything happening on these devices that shouldn’t be?” | “Are my clients’ devices in good working order?” | “Are my clients’ devices online and performing as expected?” |
| Key activities | Watching for suspicious behavior, unauthorized software, failed backups, offline agents, encryption status, and excessive local admin accounts | Patching, software deployment, configuration enforcement, device inventory, and remote access | Uptime checks, performance tracking, agent status, disk space, and offline device alerts |
| When it acts | Continuous, real-time | Scheduled or on-demand | Periodic or continuous |
| Primary output | Actionable security alerts | Healthy, up-to-date devices | Operational status reports |
It’s worth noting that MSPs need all three. A patching system that doesn’t talk to your security alerting system means you might fix software vulnerabilities without knowing that a device was already compromised. The strongest MSP operations treat all these practices with the same amount of priority, not separate product categories.
3. Remediation
Remediation is how MSPs fix issues remotely. This can include:
- Deploying patches
- Running automated scripts to correct misconfigurations
- Isolating a compromised device from the network
- Removing unauthorized software
Fast, remote remediation is one of the clearest ways for MSPs to demonstrate operational value, as it directly reduces the time between detection and resolution.
4. Reporting
Everything your tools find and fix needs to be communicated to clients in a way they can understand. This is important: Leadership only appreciates what it can understand. We’ve discussed this in more depth in our guide, How to Communicate MSP Business Value to Non-Technical Decision Makers, but in essence, good reporting closes the loop between technical work and client trust.
Good reporting doesn’t just prove that work was done; it shows that the work made the client safer.
How endpoint security monitoring supports managed services
Endpoint security monitoring helps MSPs identify endpoint risks before they become client-impacting incidents. However, this is where some MSP leaders underestimate the term “monitoring.”
At a minimum, effective endpoint security monitoring tracks whether:
- Endpoint protection software is active and up to date
- Any suspicious behavior has been flagged
- Full-disk encryption is enabled
- Recent backups were completed successfully
- Local administrator accounts pose an unnecessary risk
- Any agents have gone offline or stopped reporting
- Any unusual remote access activity has occurred
Each of these signals tells a story. For example, a delayed (or failed) backup is an early warning sign that something may already be wrong. Effective monitoring surfaces these conditions as actionable alerts rather than burying them in a dashboard nobody checks.
Endpoint management service capabilities to include
The complete endpoint management service does more than watch for threats. It combines operational maintenance with security controls into a single, consistent service layer across all client environments.
- Operational maintenance: This means automated patch deployment with defined maintenance windows and rollback safety, device configuration enforcement to ensure endpoints meet baseline security standards, software inventory to track what’s installed and flag anything that shouldn’t be there, and remote remediation scripts that let technicians fix common issues without escalating to a site visit.
- Security: This means investing in endpoint hardening checks to reduce attack surface, endpoint protection management to ensure every device has active and current coverage, and role-based technician access so that the right people can act on the right clients without overreaching into environments they don’t manage.
Tying these together are two critical operational connectors: PSA and ticketing integration, which ensures that alerts automatically become tickets and that remediation is documented without manual logging, and reports that are comprehensive while still being easily understandable.
How MSPs use EDR and endpoint protection
Let’s have a quick definition first:
- Endpoint protection platforms: Think traditional antivirus, anti-malware, and firewall capabilities. While they’re excellent at blocking known threats based on recognized signatures, they may struggle with sophisticated or novel attacks.
- Endpoint detection and response (EDR): These take endpoint protection further. Rather than just blocking known threats, EDR continuously monitors endpoint behavior, looking for unusual process activity, lateral movement, privilege escalation, and other patterns that signature tools would miss.
Looking at the above definitions, you may assume that EDR tools are “better” than endpoint protection platforms. After all, anything that does something “further” means extended capabilities, right?
Well, not necessarily, and definitely not in the case of endpoint security.
The fact is that an effective MSP security workflow includes both, as each serves different but complementary purposes.
Endpoint protection is your first line of defense and a necessary baseline for every client environment. EDR then supplements this by looking for patterns that signature-based tools may miss.
For MSPs using EDR, the workflow looks something like this:
- When a behavioral alert fires, the IT admin prioritizes it by client impact.
- From there, the workflow moves to isolating the affected device, if necessary.
- IT admins then review the incident timeline to understand what happened and when.
- Further coordination with the client’s internal IT team (if one exists) may happen.
- Depending on the severity of the alert, MSP admins may escalate the issue through defined channels.
- MSPs must report all actions taken for client review.
What makes this workflow actually function is integration. EDR should not operate separately from your endpoint protection platform. When a behavioral alert fires, your team should be able to immediately see that device’s patch status, ownership, recent activity, and backup health, all in the same view.
That context is what separates a fast, informed response from a slow, fragmented one. The strongest MSP workflows connect security alerts with device context automatically, creating tickets in the PSA and pulling in the relevant endpoint data without requiring a technician to manually piece it together across multiple consoles.
What to look for in MSP monitoring software
Keep in mind that this isn’t an exhaustive list, nor should it be considered the “perfect” one. Every MSP is different, and its requirements will differ as well. Even so, here are some features to consider:
- Multi-tenant architecture: Each client should have their own data, their own alert thresholds, and their own reporting, while you maintain centralized visibility across all of them from a single dashboard.
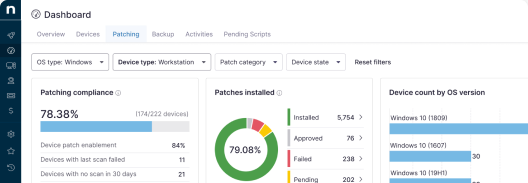
- Endpoint health and security visibility: Look for platforms that surface patch compliance, protection status, vulnerability exposure, encryption status, and backup health alongside standard performance metrics.
- Custom alert thresholds: Not every client has the same risk profile. For example, a healthcare client with strict HIPAA obligations needs different alert sensitivity than a small retail operation. Your platform should let you tune monitoring policies per client without rebuilding everything from scratch each time.
- Automated ticket creation: Look for direct, configurable PSA integration that creates, routes, and prioritizes tickets automatically.
- Remote remediation options: The best endpoint tools support remote script execution, patch deployment, and device isolation from within the same console. This helps reduce response time significantly, while also preventing tool sprawl.
- EDR and endpoint protection integrations: Your monitoring platform and your EDR solution should share data, not operate in separate silos.
- Client-level reporting: Look for platforms that make it easy to generate clean, plain-language reports by client, without requiring hours of manual formatting each month.
- Automation templates: These help you build a baseline service configuration once and apply it across multiple clients. Standardization is what allows MSPs to scale without adding headcount proportionally to every new client.
Common mistakes MSPs make
Mistake 1: Treating endpoint monitoring as basic uptime monitoring
Treating endpoint monitoring as basic uptime monitoring is probably the most widespread mistake. Remember: Uptime monitoring and endpoint security monitoring are not the same thing. A proper endpoint security monitoring policy includes protection status, patch exposure, behavioral anomalies, and backup health as first-class signals.
How to fix it: Expand your monitoring policy to include protection status, patch exposure, behavioral anomalies, backup health, and encryption status as first-class signals alongside performance metrics.
Mistake 2: Creating too many alerts without escalation logic
Creating too many alerts without escalation logic burns out technicians and trains them to ignore the queue. Every alert should have a defined owner, a defined response time, and a clear escalation path.
How to fix it: For every active alert, define an owner, a response time, and a clear escalation path. If you can’t answer “what happens when this fires?”, the alert isn’t ready to be active yet.
Mistake 3: Separating endpoint security monitoring from ticketing workflows
Security alerts that require manual ticket creation get missed, especially during high-volume periods or outside business hours. This is a structural gap that compounds over time.
How to fix it: Automate the connection between your monitoring platform and your PSA. Make sure to test it regularly to make sure alerts are routing and creating tickets as expected.
Mistake 4: Managing endpoint protection without device context
Knowing that a threat was detected is only useful if you also know what that device is, who owns it, when it was last patched, and whether its backup is current. Without that context, response decisions are made blindly.
How to fix it: Ensure your EDR and endpoint protection tools share data with your endpoint management platform.
Mistake 5: Ignoring patch status when investigating a security alert
Patch context often explains how a threat actor got in and what they exploited. Treating a security investigation without checking vulnerability history is like investigating a break-in without checking which windows were unlocked.
How to fix it: Make patch status one of the first data points visible when reviewing any security incident. Connect your patch management and EDR workflows so this context is pulled automatically.
Mistake 6: Reporting only ticket volume instead of risk reduction
Clients don’t care how many tickets were closed. They care whether their business is safer than it was last month. Showing them your ticket volume only tells them that you were busy, not how well you protected them.
How to fix it: Rebuild your client reports around risk indicators: reduction in unpatched vulnerabilities, improvement in protection coverage, and decrease in high-severity alerts over time.
Mistake 7: Choosing MSP monitoring software without validating multi-tenant workflows
Demo environments are designed to look good. A platform that works smoothly in a single-tenant demo may behave very differently when managing dozens of clients with different policies, alert thresholds, and reporting requirements.
How to fix it: Before committing to a platform, test it against your actual client structure.
The importance of MSP monitoring software
Endpoint security monitoring helps MSPs identify risk across client environments before it becomes an incident. That said, MSP security is not just about buying the right products; it’s about developing a culture of security. It is very important that you implement the right policies and develop the right workflows so that endpoint security monitoring becomes an ingrained practice in your organization.
Related topics: