Zero-intervention patch rollout in NinjaOne Patch Management
Zero-intervention patch rollout in NinjaOne Patch Management automatically deploys approved patches based on predefined policies after approval rules are configured.
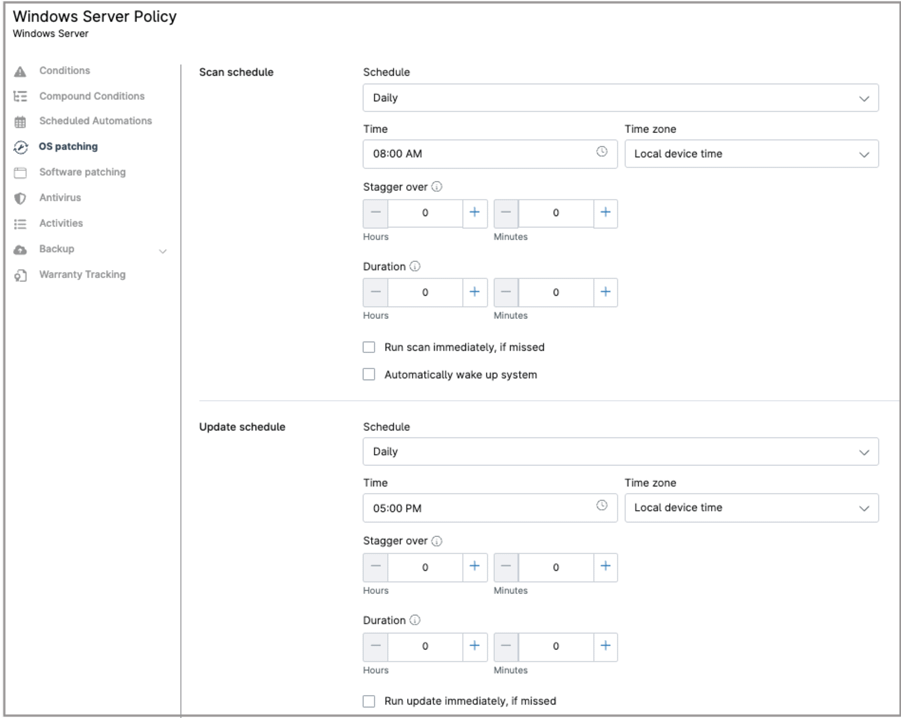
Zero-intervention patch rollout in NinjaOne Patch Management automatically deploys approved patches based on predefined policies after approval rules are configured.


The following table highlights common patch deployment challenges MSPs face and how zero-intervention patch rollout in NinjaOne addresses them.
| Problem | How NinjaOne resolves it |
| Manual patch deployments consume technician time. | Administrators configure patch settings in Agent Policies, allowing endpoints to scan, download, and install approved updates automatically according to the defined schedule. |
| Security updates are deployed inconsistently. Some endpoints may receive updates on time while others are delayed because they follow different patch settings. | Agent Policies apply standardized patch settings, approval rules, maintenance windows, and reboot behavior to groups of managed devices, helping ensure consistent configuration. |
| Missed maintenance windows due to manual scheduling. | Endpoints follow the maintenance windows defined in their assigned Agent Policy, enabling patch installation during scheduled deployment periods without requiring technicians to initiate each rollout. |
| Difficulties tracking deployment status. | After endpoints complete patch operations, the NinjaOne agent reports installation results to the platform, where administrators can review deployment status, failures, and compliance from a centralized console. |
| Large-scale deployments require repetitive administrative effort. | Once administrators define approval rules and deployment schedules, the agent enforces those settings across assigned endpoints, reducing the need for repeated manual deployment actions while allowing exceptions when needed. |
The following benefits describe the operational outcomes MSPs and IT teams can achieve by using zero-intervention patch rollout in NinjaOne Patch Management.
Once patch settings and deployment rules are configured, endpoints install approved updates automatically, reducing the need for technicians to start routine deployments.
Agent Policies apply standardized approval rules, maintenance windows, and reboot behavior to groups of endpoints, helping maintain a consistent deployment process.
Automated deployment enables IT teams and MSPs to roll out approved updates across many endpoints without managing each device individually.
Deployment results are reported to the NinjaOne console, where color-coded icons flag failed or missed deployments so administrators can spot and resolve issues at a glance.
The following capabilities describe how zero-intervention patch rollout in NinjaOne Patch Management is used to automate routine patch deployment activities.

Administrators define patch approval rules, maintenance windows, and reboot behavior in Agent Policies. Endpoints automatically follow those settings during patch deployment.

Patch installations occur only during the maintenance windows configured in the assigned Agent Policy. This helps prevent updates from installing outside approved deployment periods.

Updates can be approved automatically based on criteria such as classification, severity, or KB number. This enables routine updates to proceed without requiring technicians to review each patch individually.

NinjaOne records the outcome of patch deployments and displays installation status for managed endpoints in the central console. This enables administrators to review patch compliance and identify devices that require further attention or remediation.
The following examples illustrate how zero-intervention patch rollout in NinjaOne Patch Management is used in day-to-day patch deployment operations.
IT teams configure patch settings in an Agent Policy and assign it to remote devices regardless of their location. Endpoints install approved updates during scheduled maintenance windows without requiring technicians to initiate deployments individually, helping maintain a consistent deployment process for distributed workforces.
Organizations assign different Agent Policies to departments with different maintenance windows or reboot requirements while applying a consistent patch management approach. IT teams can automate patch deployment according to each department’s operational schedule without manually reconfiguring individual endpoints.
MSPs create separate Agent Policies for each customer, defining maintenance windows, approval rules, and reboot behavior that match each client’s requirements. Technicians can manage automated patch deployments for multiple customer environments from a single NinjaOne console while maintaining independent configurations for each organization.
Administrators identify which updates should be automatically deployed, determine the target endpoint groups, and define the deployment schedule, testing process, and approval strategy.
Administrators enable OS patching and define approval rules, maintenance windows, and reboot behavior in an Agent Policy.
Administrators assign the Agent Policy to the target endpoints that should receive automated deployment.
Assigned endpoints receive the policy settings and automatically scan for, download, and install approved updates according to the defined schedule, without technician intervention.
Administrators review deployment outcomes in the console to verify patch status and address failed or missed installations.
100,000
Endpoints managed
“NinjaOne is a scalable solution. It’s built on a modern SaaS architecture and it’s future-proof.”

40%
More Cost Effective
“NinjaOne’s price point is 40% less than any other endpoint management tool on the market, while being more powerful and easy to use.”

10-15
Tools Replaced
“Before, I needed 10-15 different tools to execute what NinjaOne does in its centralized, single pane of glass.”

30%
Less time for patching
“We observed a 30% reduction in the time taken for patch deployments compared to our previous solution.”

2,000
Endpoints managed
“NinjaOne gives me much more flexibility and security in my work”

30%
Annual ROI
“[NinjaOne] has already shown its value in ROI…it’s at least a hundred thousand dollars annually.”

24x
Faster Endpoint Management
“Our processes have become 24x faster with NinjaOne.”

20-40
Hours Saved Each Week
“Leveraging the automations feature within NinjaOne has enabled me to save upwards of what would likely be 20 to 30 to even 40 hours per week.”

"We observed a 30% reduction in the time taken for patch deployments compared to our previous solution. NinjaOne's efficient patching mechanisms allowed for quicker and more streamlined updates."
— Manoj Gopalakrishnan, Director of IT at Al Abbar Group
Source: AI Abbar Group – NinjaOne
Before NinjaOne, the City of Vidalia, LA had an employee spend 20–30 hours a week traveling between locations to manually update endpoints. After automating deployment through NinjaOne, the city shifted most of that time from patching to other IT priorities.

Patching vulnerable software and systems is more important and challenging to keep up with than ever. Here’s how IT pros can make their patch management process more efficient, eliminate disruption, and keep their networks secure.
NinjaOne introduced Patch Intelligence AI within its automated patch management platform to address these risks. The tool helps IT teams manage patches proactively and with greater confidence.
A zero-intervention patch rollout is an automated deployment process within NinjaOne Patch Management. Endpoints install approved updates according to the patch settings defined in their assigned Agent Policy, without requiring technician intervention during routine deployments.
Administrators configure scan schedules, deployment schedules, patch approvals, and reboot behavior in an Agent Policy. The NinjaOne agent applies those settings on assigned endpoints and automatically deploys approved updates according to the configured schedule.
NinjaOne Patch Management supports automated deployment of operating system updates and supported third-party application updates. Administrators control which updates are deployed through the patch approval settings configured in the Agent Policy.
Automated deployment helps ensure approved updates are installed according to consistent schedules across managed endpoints. NinjaOne also records deployment results, allowing administrators to review patch status and demonstrate patch compliance.
Yes. Different Agent Policies can be assigned to different organizations or sites, each with its own patch approval settings, maintenance windows, deployment schedules, and reboot behavior. This allows organizations to tailor automated patch deployment to different operational requirements.
Endpoints automatically scan for and deploy approved updates according to the schedule defined in their assigned Agent Policy. The patch dashboard highlights missed or failed deployments with color-coded icons, so administrators can spot and remediate issues at a glance.
Administrators can use Patch Intelligence AI to review AI-generated summaries of updates, including known issues reported by Microsoft, the community, and anonymized failure and rollback telemetry from NinjaOne deployments, before approving patches. Combined with configurable approval settings, maintenance windows, and separate Agent Policies for pilot and production devices, this helps organizations make more informed deployment decisions.
Yes. Patch approval settings, deployment schedules, and maintenance windows are configured together within an Agent Policy. Endpoints deploy only approved updates during the defined maintenance window.
Routine patch deployments occur automatically after administrators configure the required patch settings. This reduces the need to manually initiate deployments while allowing IT teams to manage patch deployment from a centralized console.
The NinjaOne platform collects deployment results from managed endpoints and displays installation status, failed deployments, pending updates, and patch compliance information. Administrators can use this information to monitor deployment progress and identify endpoints that require attention.


