



Key Points
- WAFs refer to security controls that filter and block malicious HTTP traffic before it reaches a web application
- Cybersecurity teams can choose between cloud-based, hardware, and software WAFs depending on traffic patterns, infrastructure, and compliance needs.
- Configure rules for specific attack types, then test and tune them against real traffic to reduce false positives.
- Monitor WAF alerts and apply updates and security patches regularly to counter new attack vectors.
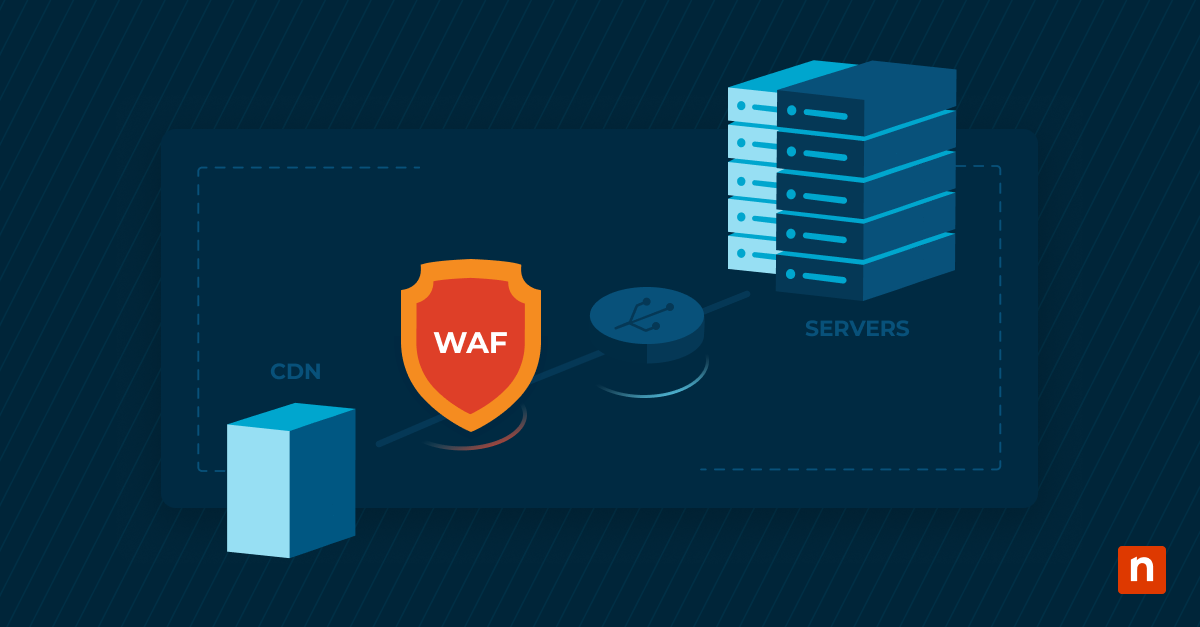
A Web Application Firewall (WAF) is a security control that monitors, filters, and blocks malicious HTTP traffic between a web application and the internet. It operates at the application layer, so it can stop cyberattacks such as SQL injection and cross-site scripting that traditional network firewalls typically do not inspect.
This article explores Web Application Firewalls (WAFs), what they are, how they work, their benefits, and the crucial role they play in fortifying web applications and networks against cyber threats.
What is a WAF?
WAFs sit between a web application and the internet, inspecting HTTP traffic against a set of security rules. A traditional network firewall typically filters traffic by IP address and port, while WAFs read the content of web requests at the application layer. Requests that match a known attack pattern, such as a SQL injection payload, are blocked before they reach the application.
WAFs come equipped with a range of features and capabilities that contribute to their effectiveness. These include real-time monitoring, access control, and the ability to enforce security policies.
Additionally, WAFs often include features such as SSL/TLS termination, bot mitigation, and content filtering, which add further layers of protection.
WAFs work by inspecting and filtering HTTP traffic between a web application and the internet. They analyze this traffic for suspicious patterns or malicious payloads, preventing potential threats from reaching the web application endpoint. WAFs use predefined rules to identify and block common attack vectors, making them an essential component of a robust cybersecurity strategy.
WAF rules define criteria for identifying and mitigating potential threats and are tailored to specific types of attacks, such as SQL injection or cross-site scripting. Configuring and maintaining these rules is crucial for ensuring the WAF’s effectiveness in safeguarding web applications against a diverse range of cyber threats.
Build on traffic filtering with a plan to identify and remediate vulnerabilities
Download NinjaOne’s Essential Guide to Vulnerability Management
Types of WAF
WAFs come in various forms, including cloud-based, hardware, and software solutions. Here’s a summarized table of each type:
| Type | Key characteristics |
| Cloud-based | Scalable and flexible, suits dynamic web traffic, applies automatic updates, and requires attention to data sovereignty and compliance |
| Hardware | Physical appliance that provides dedicated protection |
| Software | Deployed as an application within the organization’s infrastructure |
Cloud-based WAFs offer scalability and flexibility, making them suitable for organizations with dynamic web traffic patterns.
Hardware WAFs, on the other hand, are physical appliances that provide dedicated protection, while software WAFs are deployed as applications within the organization’s infrastructure.
Deploying a WAF in the cloud offers several benefits, including automatic updates, scalability, and ease of management. Cloud-based WAFs provide a centralized solution for organizations with distributed web applications, simplifying deployment and ensuring consistent security across all assets.
However, considerations such as data sovereignty and compliance must be addressed when opting for a cloud-based WAF.
How to implement a WAF
Before implementing a WAF, organizations must assess their specific web application security needs. This involves identifying potential vulnerabilities, understanding traffic patterns, and prioritizing the types of threats the WAF should address. From there, WAF implementation is a three-phase process:
- Select the right WAF solution for your organization: Evaluate factors such as scalability, compatibility, and the level of customization required. Organizations should select a WAF solution that aligns with their infrastructure, budget, and security requirements.
- Configure the WAF: Once a WAF solution is selected, proper configuration is crucial. This includes defining security rules, specifying allowed and blocked traffic, and configuring settings such as SSL termination and logging.
- Test and fine-tune WAF rules: After initial configuration, thorough testing is necessary to ensure the WAF operates effectively. Fine-tuning rules based on real-world traffic and attack scenarios helps optimize the WAF’s performance and minimize false positives.
Successful integration of a WAF requires compatibility with existing infrastructure components such as web servers, content management systems, and APIs. Ensuring seamless communication between the WAF and these elements is crucial for maintaining operational efficiency:
- Ensure smooth data flow while maintaining security: Integration should not compromise data flow. Organizations must strike a balance between security and usability, ensuring the WAF effectively protects web applications without disrupting legitimate data flow.
- Monitor and manage the WAF: Continuous monitoring is essential for detecting and responding to potential threats in real time. The WAF should generate alerts for suspicious activities, enabling timely incident response to mitigate potential risks.
- Apply updates and security patches regularly: To stay ahead of emerging threats, organizations must keep their WAF up to date and patched. This ensures that the WAF remains equipped to counter new attack vectors and vulnerabilities.
Stop web attacks before they reach your app. Watch What Is WAF (Web Application Firewall) to see how it protects you.
Connect vulnerability findings with patch remediation from a single console
Strengthen cybersecurity strategies with timely WAF implementation
As organizations increasingly rely on web applications for their day-to-day operations, WAFs have become more crucial for cybersecurity, especially as a frontline defense against common web threats.
Now, while WAFs protect the application layer, the operating systems and applications on the servers underneath it still need regular patching. This is where patch management tools, such as NinjaOne, come in: they track patch compliance across operating systems and applications on managed endpoints, helping IT teams reduce the attack surface around the systems a WAF protects.






