Key Points
- MSPs can overcome initial compliance hurdles by resolving fragmented governance, poor documentation, and insecure system configurations.
- IT partners align your network with federal standards by establishing clear data boundaries, enforcing strict access controls, and standardizing device configurations.
- Continuous network monitoring helps detect security drift and generates historical, timestamped records that support compliance validation during audits.
- Creating a highly detailed Shared Responsibility Matrix is essential to clearly dividing specific security duties between internal staff and external IT partners.
- A successful formal assessment depends on accurate, customized documentation, like a precise System Security Plan, that perfectly matches your environment’s actual technical reality.
- By treating cybersecurity as a persistent operational discipline rather than a temporary IT project, defense contractors can confidently secure and retain their eligibility to win federal contracts.
Retaining defense contracts requires organizations to continuously operate and demonstrate cybersecurity controls, which can be difficult to manage without dedicated expertise.
By delivering comprehensive Cybersecurity Maturity Model Certification (CMMC) Level 2 Managed Service Provider (MSP) support, IT partners bridge the gap between theoretical rules and proven security.
In this guide, you will learn how managed services actively transition businesses to validated compliance.
Initial state: Common challenges before MSP involvement
Organizations pursuing a CMMC level 2 implementation often begin with fragmented or incomplete security practices. These early gaps make achieving compliance difficult and significantly increase the risk of an assessment failure.
Before bringing in CMMC Level 2 MSP support, defense contractors typically face five critical hurdles:
Unclear ownership of responsibilities
Many businesses lack dedicated internal experts to manage complex federal security rules. This can lead to unclear ownership, inconsistent processes, and poorly defined compliance responsibilities.
Lack of documented control implementation
Instead of accurate System Security Plans, companies often rely on generic templates. This documentation may fail to accurately reflect the actual IT environment and can create issues during formal assessments.
Inconsistent system configurations
Organizations frequently struggle to identify where Controlled Unclassified Information (CUI) is stored or processed. This can contribute to security gaps, such as inconsistent multi-factor authentication (MFA) enforcement or the use of insecure shared accounts.
Limited visibility into compliance status
Without proper documentation and clear data boundaries, IT leaders cannot accurately gauge their true security posture. This often results in inaccurate self-assessments and a false sense of audit readiness.
Gaps in monitoring and reporting
A lack of centralized logging or active threat monitoring reduces visibility into security events and limits an organization’s ability to demonstrate that security controls are operating effectively.
Understanding the importance of CMMC Level 2 often leads defense contractors to seek specialized compliance and security support. Managed service providers can help organizations address common security and compliance challenges, improve audit readiness, and support federal contract requirements.
Related topic: What Is CMMC? A Beginner-Friendly Overview
Aligning IT services with CMMC level 2 requirements
The first step in any successful CMMC level 2 implementation is aligning your IT services directly with federal security requirements.
To support CMMC Level 2 compliance, managed IT services should focus on implementing, monitoring, and documenting security controls rather than only providing traditional IT support. This requires a structured approach to move from inconsistent or undocumented practices to validated security processes and controls.
Organizations achieve this alignment by executing four primary steps:
Map existing systems
- Identify where sensitive data lives and moves across your network. A compliance managed service maps your current software and hardware to the required federal security rules to establish clear data boundaries.
Identify security gaps
- Compare your current setup against the federal standards. This step uncovers missing technical requirements, such as inconsistent multi-factor authentication (MFA), weak data encryption, or a lack of active network monitoring.
Define responsibility boundaries
- Establishing a clear division of labor is a core part of CMMC level 2 MSP support. This formalizes exactly which security tasks your internal team handles versus what your external IT partners manage.
Prioritize fixes
- Uncovered security gaps are organized into a structured action plan. Because compliance carries hard deadlines, managed services for CMMC prioritize these updates based on risk severity and technical difficulty.
Implementing and enforcing security controls
Once security gaps are identified, the next step in implementing CMMC level 2 is deploying and strictly enforcing the necessary security controls. Managed service providers help organizations implement, monitor, and document these controls as part of an ongoing compliance and security process.
To support security and compliance objectives, MSPs typically focus on four main operational activities:
- Standardizing computer configurations
Applying secure, baseline settings to all company computers and servers to block unauthorized software and prevent risky changes. OS hardening ensures that every device adheres to standardized security policies, minimizing the attack surface across your entire organization.
- Patch and vulnerability management
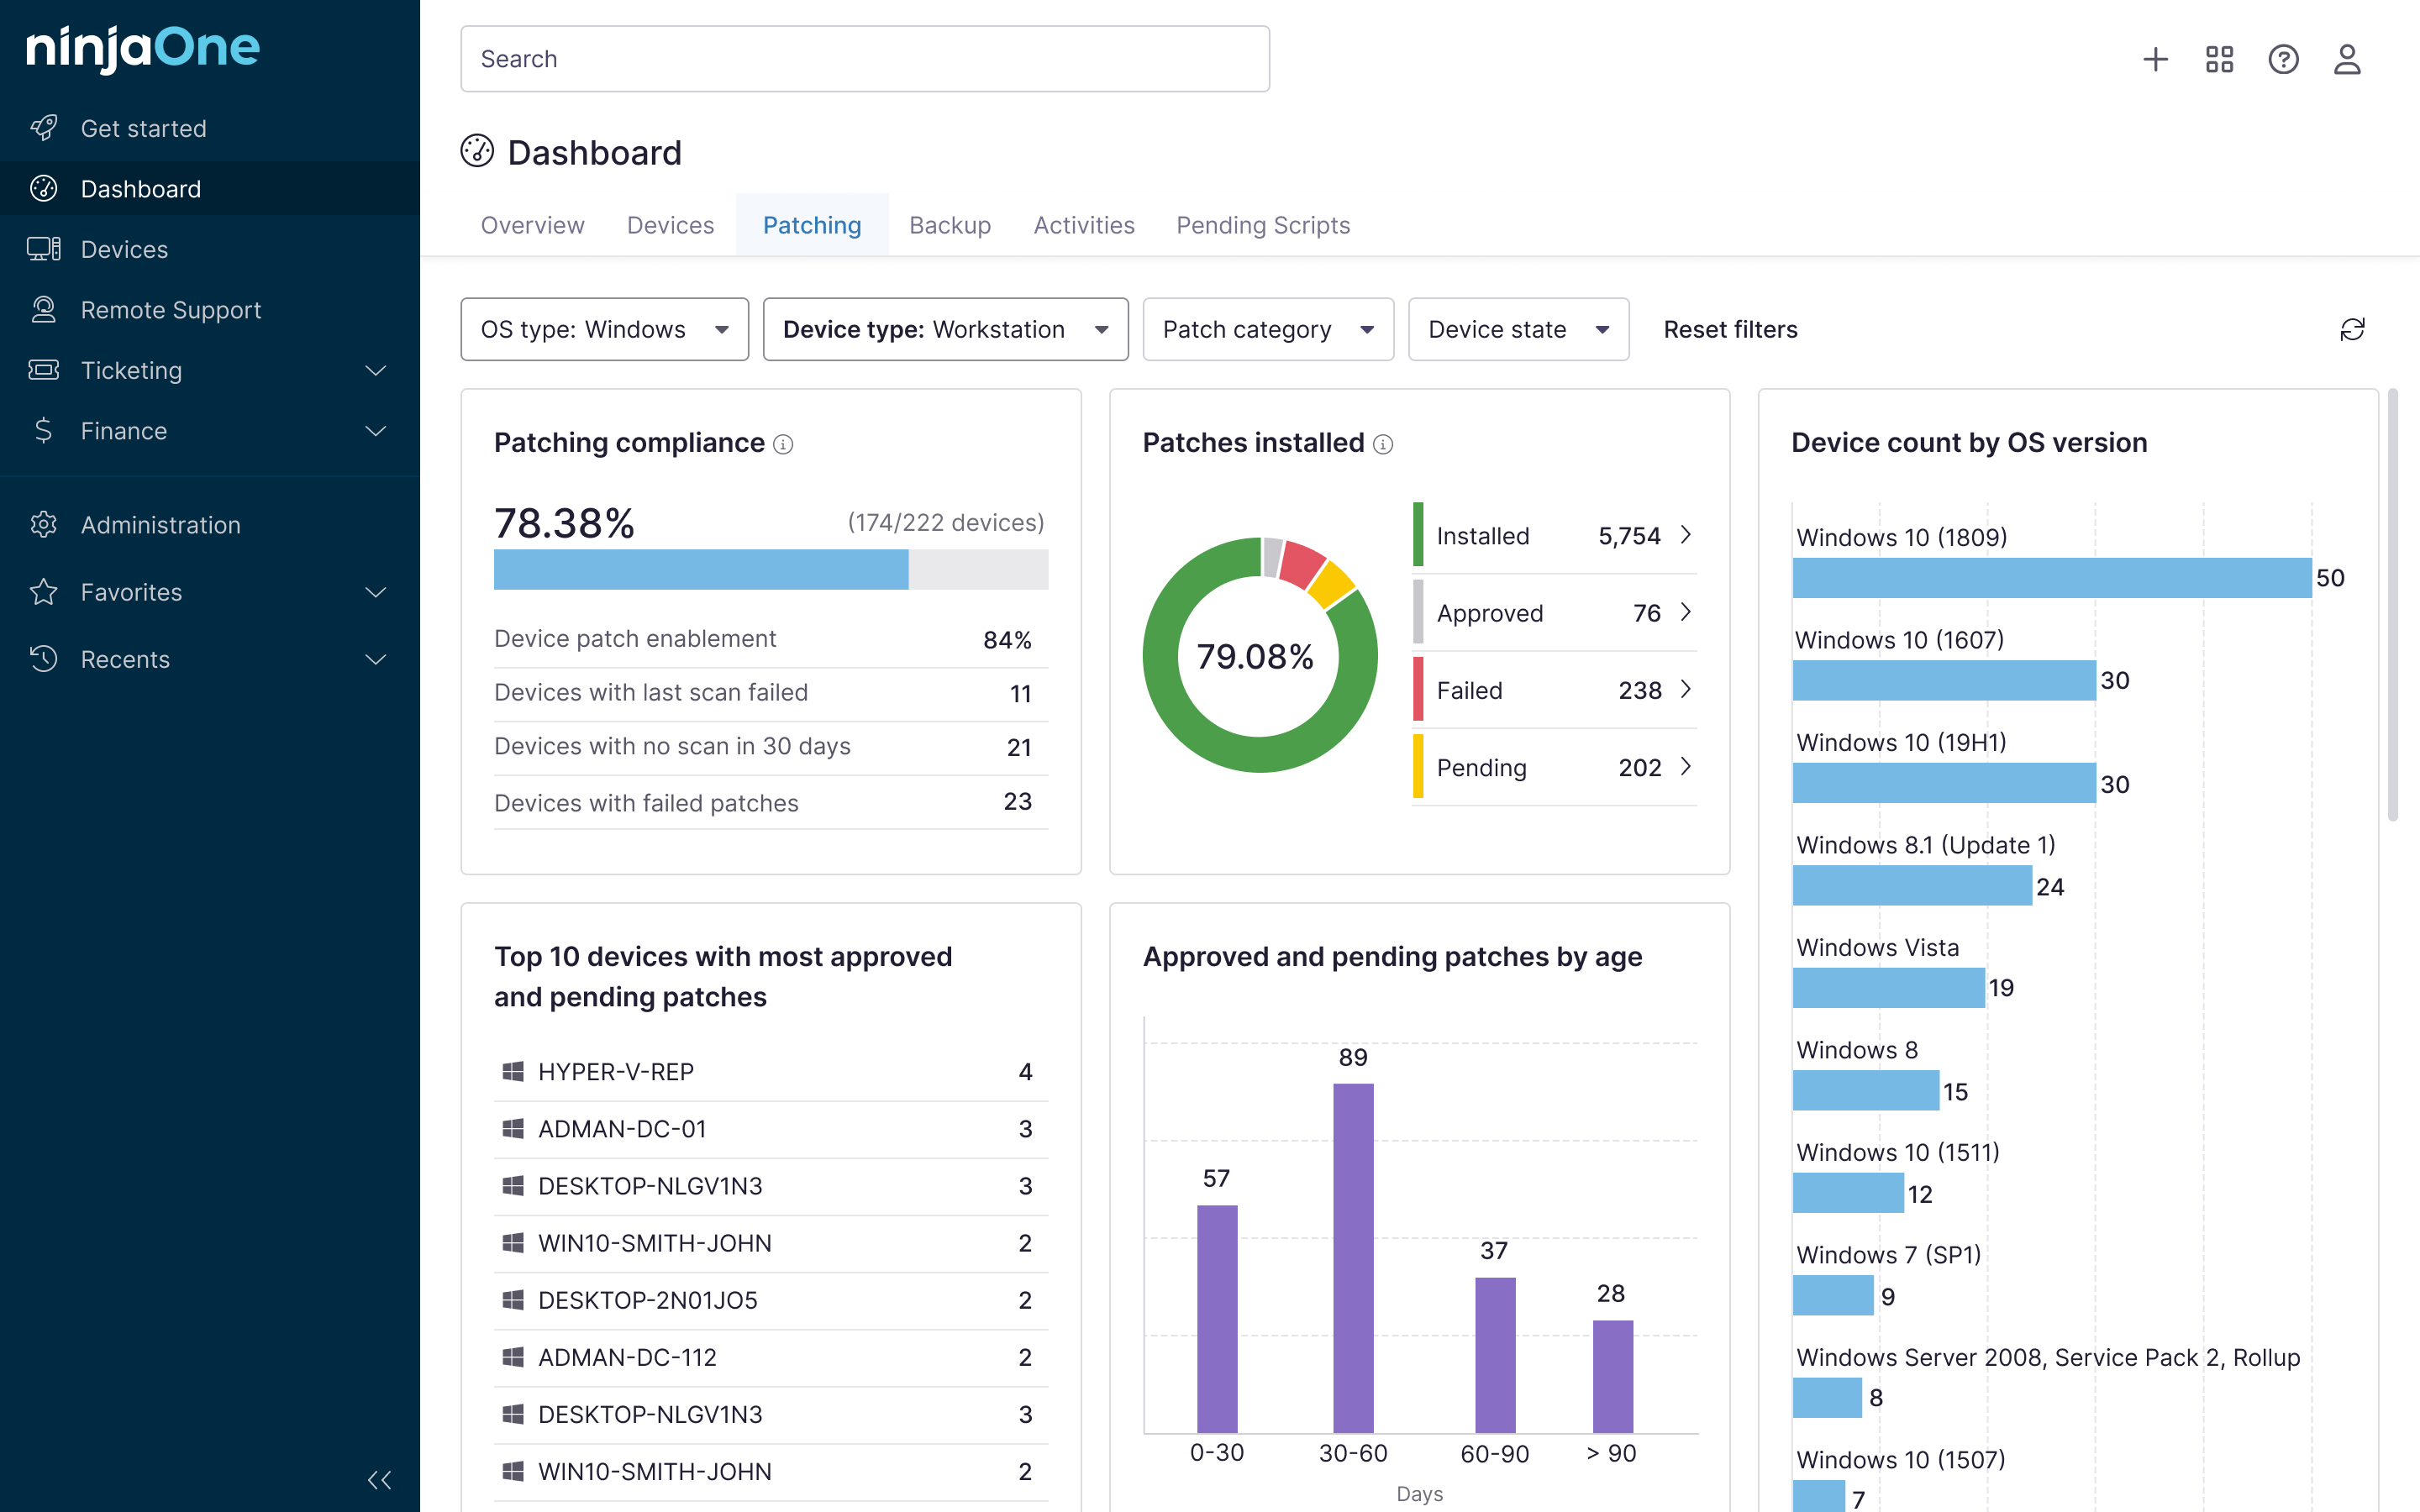
Actively scanning the network to identify, test, and install critical software updates before threats can exploit them. Automated patch management allows IT teams to test and deploy fixes across Windows, macOS, and Linux endpoints. This proactive remediation ensures that CUI(Controlled Unclassified Information) remains protected against known vulnerabilities.
- Enforcing access controls
Restricting user access to only the data required for their specific job is a core CMMC requirement. Mandating multi-factor authentication (MFA) and role-based access control ensures that stolen credentials alone cannot compromise sensitive government information.
- Centralized logging and monitoring
Recording system activity and watching the network 24/7 allows for the rapid detection of suspicious events. Endpoint monitoring provides telemetry and audit logs that support security monitoring and compliance assessments.
Establishing continuous compliance monitoring and reporting
After initial setup, security controls must be continuously maintained and monitored. Managed service providers help organizations maintain security and compliance processes over time through ongoing monitoring and operational support.
To achieve this, IT partners combine active system monitoring with automated reporting mechanisms:
| Operational Goal | Active Monitoring Action | Reporting Output |
| System Integrity | Continuously checks system configurations to ensure settings remain correct. | Provides audit logs and monitoring records that support compliance validation and security oversight. |
| Threat Detection | Detects unauthorized changes and deviations from approved security configurations. | Generates the historical, timestamped records required for third-party audit validation. |
| Vulnerability Remediation Tracking | Tracks remediation activities and vulnerability resolution progress across the environment. | Gives leadership clear, real-time dashboards detailing the company’s current compliance status. |
Continuous monitoring and oversight are important parts of maintaining CMMC Level 2 compliance. Managed service providers support these efforts by helping organizations maintain security controls and generate audit evidence through ongoing monitoring and reporting.
Preparing for audit validation
Achieving formal certification requires proving to an independent assessor that your security controls are fully implemented and functioning daily. A compliance managed service transforms standard IT setups into audit-ready environments.
As the final step in a CMMC level 2 implementation, expert MSP support actively manages audit preparation by:
- Drafting mandatory documents, such as the System Security Plan, which describes how the organization implements and manages security controls to meet federal security requirements.
- Gathering historical system logs and records to provide concrete evidence that security rules are consistently enforced over time.
- Conducting practice assessments to find and fix any remaining vulnerabilities before the official review.
- Participating directly in the formal audit to answer technical questions and present system evidence to the assessor.
Thorough preparation helps organizations improve audit readiness and support their efforts to achieve CMMC certification and maintain eligibility for federal contracts.
Related topic: How to Prepare Clients for a Surprise Compliance Audit (HIPAA, CMMC, SOC 2)
What does an audit-ready IT environment actually look like?
Discover how NinjaOne simplifies CMMC compliance and documentation.
Outcomes and long-term impact of CMMC level 2 MSP support
Organizations that successfully implement federal security controls with expert IT partners experience measurable, long-term business improvements.
Achieving CMMC compliance can help organizations move from reactive security operations toward more structured and consistent security and compliance processes. Common long-term outcomes include:
- Increased visibility: Managed service providers help organizations improve visibility into their systems, security controls, and compliance posture through continuous monitoring and reporting. This helps leadership make more informed security and compliance decisions.
- Improved system consistency: By following a structured CMMC level 2 implementation guide, organizations achieve strict technical consistency. Standardized endpoints and centralized policies support more consistent security management across all hardware and software.
- Reduced compliance gaps: Continuous monitoring helps organizations identify configuration changes, vulnerabilities, and compliance issues more quickly. Managed service providers can support remediation efforts and help organizations maintain ongoing compliance and audit readiness over time.
- Enhanced audit readiness: Organizations improve audit readiness through ongoing documentation, logging, and evidence collection. This continuous preparation helps support third-party assessments by demonstrating the ongoing operation of security controls over time.
Many defense contractors rely on specialized IT and compliance providers to support CMMC requirements. Managed service providers can help organizations maintain security controls, monitoring processes, and audit readiness over time while supporting ongoing federal contract requirements.
Lessons learned from real-world implementations
Real-world implementations reveal that transitioning to federal security standards requires more than basic IT checklists. Here are the most critical lessons learned from actual CMMC audits:
Build a culture of security
Compliance cannot be a temporary IT project. Employees must actively practice secure workflows every day. Teams should emphasize the need for operational discipline, noting that technology is ineffective unless teams translate it into repeatable, daily processes.
Match documentation to reality
Relying on generic policy templates frequently causes assessment failures. Auditors demand proof that your written rules exactly match your system settings. Kaseya highlights that utilizing compliance automation to generate accurate documentation is crucial for proving your actual system configurations.
Implement continuous monitoring
Continuous monitoring helps organizations detect unauthorized changes and security issues more quickly. In addition to collecting logs, organizations should actively review monitoring data and security events.
This ongoing oversight helps provide historical evidence that supports the operation of security controls between formal assessments.
Define shared responsibilities
Clear boundaries prevent critical security gaps. A highly detailed Shared Responsibility Matrix is a “non-negotiable requirement” for audits. Businesses must define exactly which tasks internal teams handle versus what IT partners manage, as the contractor retains ultimate liability.
Prepare early to reduce friction
Early preparation drastically reduces assessment friction. Engaging IT partners early allows businesses to accurately identify where sensitive data lives. This helps internal teams identify and address network vulnerabilities before the formal audit begins.
Secure your defense contracts with CMMC level 2 MSP support
Real-world execution proves that passing federal audits requires structured, daily discipline rather than isolated IT projects. By integrating expert CMMC level 2 MSP support, contractors actively align services, enforce continuous monitoring, and maintain the persistent accountability needed to achieve and sustain compliance.
Related topics: