

Key Points
- Reframing Risk Around Business Impact Reduces Panic: Keep clients engaged, not alarmed, by focusing on what the risk means for business goals rather than on technical terms.
- Visuals and Stories Make Abstract Risk Understandable: Real-world examples and graphs turn technical concepts into something non-technical stakeholders can actually grasp.
- Tone Should Convey Urgency Without Alarm: Tailoring messages to each stakeholder and setting realistic expectations builds trust during a crisis.
- Consistent Governance Keeps Communication on Track: Quarterly reviews and shared security policies prevent risk communication from becoming reactive or inconsistent.
Clear and effective security communication involves translating technical insights into concise messages. These messages should be tailored to stakeholders and influence executive action to meet enterprise needs.
Knowing how to frame incident reports in plain language can be difficult, especially in response scenarios. This article covers best practices on authoritatively communicating cyber risk to business counterparts, provides strategic tips, and answers commonly asked questions by MSPs.
Prefer a video tutorial? Watch “How to Communicate Security Risk Without Alarm: A Guide for MSPs” for a visual walkthrough.
Professionally convey how a cyber risk impacts your organization
Clients do not need every technical detail. All they need to know is what is at stake and what happens next. Follow this framework to build your IT security communication plan.
Reframe the message: From panic to purpose
Start by introducing the risks and explaining how they impact business goals to engage your client. Do this in a way that doesn’t incite fear but inspires actionable steps towards resolution, prevention, and minimized overhead.
Further, using IT terms like “system downtime” and “attack surface” can confuse or potentially scare your non-technical clients (especially during a crisis). Simplify technical IT terms with easy-to-understand examples and eliminate jargon.
Engage with visuals, stories, and context
Keep your client’s attention with graphs, real-world examples, and a larger perspective. Storytelling enhances security communication by making it more relatable, especially today, when threats are evolving faster.
A cybersecurity company wanted to highlight the value of an anti-phishing campaign. Instead of showing statistics, they shared a real incident in which a single employee’s misclick almost triggered a significant data breach. This example, paired with screenshots and visuals, turned something abstract into something real.
So what should you do? Visualize risk with resilience graphs, use narratives and analogies to help clients understand the implications, and properly set expectations regarding cyber risk management and the resources you’ll need.
Use a balanced tone: Urgency without alarm
Communicate cyber risk tactfully to minimize anxiety and keep the client focused on concrete solutions. As a service provider, you play a key part in your enterprise’s cybersecurity, and how you disclose your findings is just as important.
Tailor your messaging to different stakeholders, set realistic goals, and demonstrate your preparedness to reassure your clients. For example: “We’re monitoring business-critical systems 24/7 via RMM.”
Automate calm reinforcement for security communication
Inspire confidence with management platforms that automate risk detection with real-time alerts and centralize control. Moreover, share intelligence on emerging malware with clients and run tabletop exercises or penetration tests across your network to improve resilience.
Governance and consistent communication cadence
Security communication is a collaborative effort. To help mitigate risk, develop security policies with business partners and hold quarterly reviews to summarize system health while highlighting cybersecurity accomplishments.
You should also prepare for the worst-case scenario with emergency training drills and streamlined data backup and recovery tools.
⚠️ Things to look out for
| Risks | Potential Consequences | Recommended Actions |
| Messaging triggers a strong fear response | Client panic, PR nightmare, reduced trust in MSP | Positively position risk reports to emphasize real solutions |
| Overly technical reporting with abstract concepts | Stakeholders misunderstand or ignore your messaging | Use infographics, flowcharts, short stories, and context |
| Overpromise or underperform on cyber risk response | Complacency or panic reduces response effectiveness | Present a clear and direct call to action while avoiding hyperbole |
| Inconsistent follow-ups, a reactive approach instead of a proactive one | Undermined security posture | Set automated updates with calm language via Remote Monitoring and Management (for example, NinjaOne) and regularly reinforce security measures |
| Lack of unified security governance | Confusion, redundant efforts, security gaps | Establish a security steering committee, create support structures, and standardize interdepartmental communication. |
How NinjaOne enhances security communication
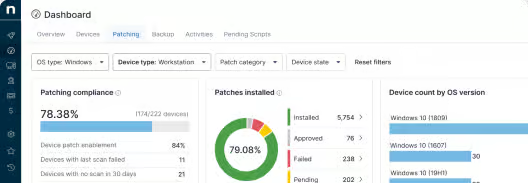
NinjaOne’s powerful endpoint management and backup capabilities empower cybersecurity teams with real-time alerts while providing clear, to-the-point data visualizations.
Client-facing dashboards can be configured for complete transparency and exported for Quarterly Business Review (QBR) needs. The platform’s consolidated features also enable system tagging for susceptible devices, enhancing granular control over end-user workstations.
Streamline security communication and risk management
Aligning system health data reports with client-centric goals helps achieve effective security communication. Consistent performance strengthens stakeholder trust, while a robust IT toolkit can elevate brand reputation in competitive markets.
Related topics: