Linux patch management with NinjaOne Autonomous Patch Management
NinjaOne Autonomous Patch Management scans, approves, and installs OS and application updates on managed Linux endpoints through each distribution’s package manager.
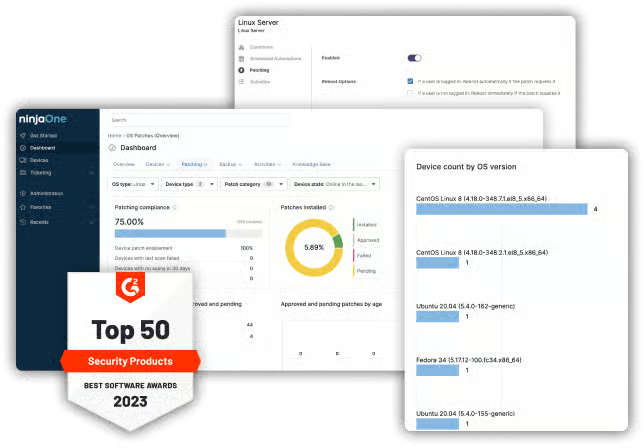
NinjaOne Autonomous Patch Management scans, approves, and installs OS and application updates on managed Linux endpoints through each distribution’s package manager.
Problem | How NinjaOne resolves it |
Linux servers run on several distributions, each with its own package manager. | Patch Management works through the package manager on each device, whether APT, DNF, YUM, or Zypper, so one policy covers mixed distributions. |
Updating Linux servers by hand means logging into each one to run package commands. | Patch Management scans and installs updates on a schedule and shows patch status in one dashboard. |
Unplanned reboots after Linux updates interrupt services that need to stay available. | Reboot behavior is set in the Linux patch policy, so restarts run inside approved maintenance windows. |
An update that depends on another package can leave a device partly updated. | Patch Management relies on the package manager to resolve dependencies and installs dependent updates together. |
Linux server operating system stay up to date without technicians logging into each server to run update commands.
Fleets that mix Debian-based and RPM-based distributions follow one patch policy instead of separate update routines.
Service disruptions are minimized by scheduling Linux reboots within defined maintenance windows.
Failed Linux patches and their failure reasons appear in a centralized dashboard, helping technicians identify and troubleshoot issues more quickly.
improved patch compliance
reduced time spent on patch management
saved time on manual tasks through automation
Consistent, policy-driven patching is core to your Linux security posture. NinjaOne centralizes Linux patch status and streamlines remediation.

The NinjaOne agent runs the package manager on each device to identify available OS updates and installs approved patches according to the policy defined schedule. Updates are sourced from the repositories configured on the endpoint.

Applications available through configured repositories can be patched alongside OS updates using APT, DNF, YUM, or Zypper. Patch Management supports package updates but does not perform major Linux distribution upgrades.

Administrators approve or reject patches through automated rules, or decline a specific patch by hand. Rules apply to every device assigned to the Linux policy, so approval decisions do not repeat device by device.

Linux policies define when patch scans and installations run and when devices reboot after patching. Reboots can be limited to defined maintenance windows to minimize disruption.

Linux servers, workstations, and laptops are patched from the same console as Windows and macOS endpoints. Remote and on-premises devices connect through the agent with no VPN required.
IT teams managing Linux servers alongside Windows and macOS devices can control patch approvals and installation schedules while monitoring patch status across operating systems from a centralized Patching dashboard.
Developers and engineers working with Linux laptops receive OS and application updates over standard internet connections, with no VPN required. A single Linux policy covers devices in the office and at home, with no separate configuration for remote machines. Administrators monitor patch status for off-site devices from the same dashboard used for on-premises servers.
Managed service providers apply a shared Linux patch policy to every client organization and adjust scan and reboot windows to each client’s business hours. Technicians manage separate client environments from one console, which reduces configuration drift between organizations.

Where RMMs should be.
Ninja’s patch management feature blows all other RMM’s out of the water, ease of use is what all other RMM products hope for.”
Matthew Anciaux
Managing Partner,
Monarchy IT LLC
Bring automation to IT Ops.
Patch management in Windows and third-party patching has saved us many man hours of our regular patching. NinjaOne has helped us bring automation to our team.”
Chris Hessler
IT Support,
Crossroad Church
Easily create highly customizable with Linux patch management policies including reboot options, scan schedule, and more to best meet your requirements.
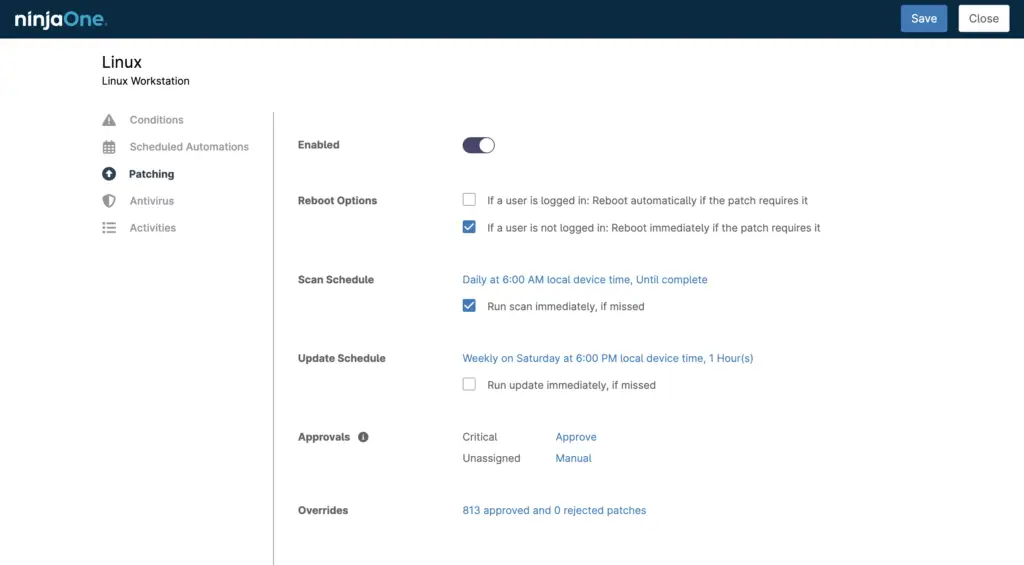
NinjaOne provides clear insight into the Linux distributions that are currently supporting your IT estate. Make faster, more informed decisions to best support your users as well as to maintain a strong security posture.
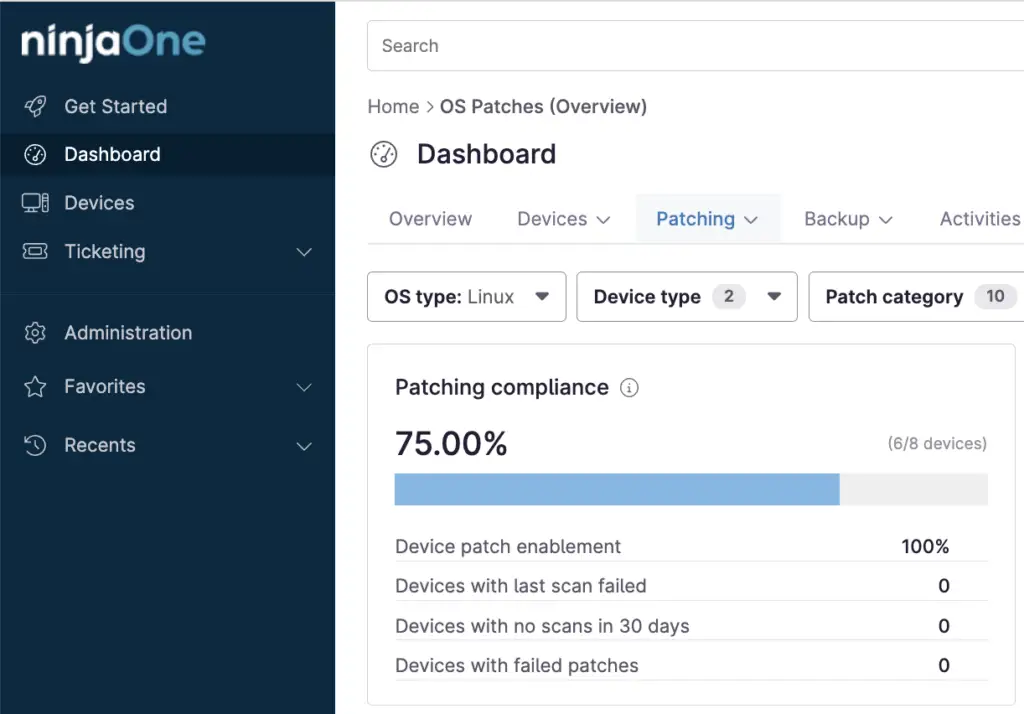
Leverage NinjaOne automation to reduce Linux patching time by up to 90% and reduce risk of human error.
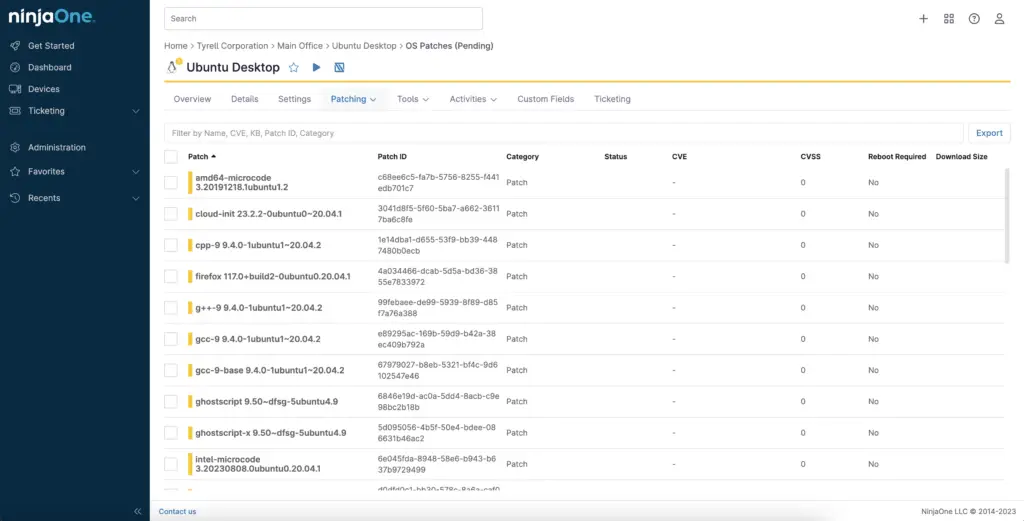
The agent brings each device under management and reports its distribution and installed packages.
Administrators set scan and install schedules, approval rules, and reboot behavior once, and the policy applies to every assigned device.
The agent runs the package manager on each device to identify available updates and installs approved patches on schedule.
The Patching dashboard shows pending, approved, rejected, installed, and failed patches, with the failure reason for any patch that did not install.
See the NinjaOne Linux Policy Setup documentation for step-by-step configuration.
Proven outcomes with NinjaOne patch automation
90 percent reduction in patch time after the City of Sarnia moved to NinjaOne automated patching.
“NinjaOne’s automated patching reduced our patch time by 90%.”
Shawn Southern, IT Infrastructure & Security Architect, City of Sarnia
Automatically evaluate updates, deploy trusted patches faster, and keep every endpoint secure without operational disruption.

Manage, patch, and support Linux endpoints across distributions easily and at scale.
This article describes the patch management features available for Linux endpoints managed by NinjaOne. It also explains how to activate, configure, and view patching activity.
It is the set of Patch Management controls that scan, approve, schedule, and install OS and application updates on managed Linux endpoints. The NinjaOne agent runs the package manager on each device to find available updates and installs approved patches on the policy schedule. Technicians track patch status for Linux, Windows, and macOS from one console.
NinjaOne patches Linux endpoints running the NinjaOne Agent, so distribution coverage follows the agent’s OS support. Fully supported distributions include Amazon Linux 2 and 2023, Red Hat Enterprise Linux 7, 8, 9, and 10, Debian 11, 12, and 13, Oracle Linux 7, 8, 9, and 10, SUSE Linux Enterprise Server 12 and later, Ubuntu 20.04, 22.04, 24.04, and 26.04 LTS, and Raspberry Pi OS. Extended support covers Rocky Linux 8–10, AlmaLinux, CentOS 7, 8, and Stream 8, Fedora 23 and later, Debian 8–10, Ubuntu 16.04, 18.04, and non-LTS releases from 15.10 onward, Kali Linux, Proxmox, and Debian, Ubuntu, and Red Hat derivatives such as Linux Mint, Pop!_OS, Zorin OS, and ClearOS. Extended-support distributions share the same core components as fully supported releases and are expected to function normally. Other 64-bit RPM or Debian-based distributions that use systemd may also be compatible.
No. Patch Intelligence AI currently provides risk analysis for Windows updates. For Linux, administrators use approval rules and patch rejection to stage or hold packages before broad deployment.
No. Patch Management applies package updates within the installed release and does not perform major distribution version upgrades, because they can break services and configuration files. Teams that need a version upgrade can run it through NinjaOne scripting after testing.
Yes. Patch Management updates any application available in the repositories configured on the endpoint, using the same package manager the OS uses. NinjaOne relies on the package manager to resolve dependencies and installs dependent package updates together.
Reboot behavior is set in the Linux patch policy alongside scan and install schedules. Administrators choose whether devices reboot after patching and when, so restarts stay inside approved maintenance windows.
Linux patching runs through the NinjaOne Agent, so the endpoint must first meet the agent’s system requirements. This includes running a supported Linux distribution with systemd as its init system, meeting the required system resources, supporting TLS 1.2, and having the required outbound connectivity. Once the agent is installed on a supported endpoint, patch management can be configured through policy.
The Patching tab on the System, Organization, or Device dashboard filters OS patches by pending, approved, rejected, installed, or failed status. Hovering over a failed patch shows the reason for the failure, and the list can be exported.