Remote PowerShell with NinjaOne Endpoint Management
NinjaOne Endpoint Management‘s remote PowerShell lets technicians run commands and scripts on a managed device in real time, without a VPN or a full remote session.
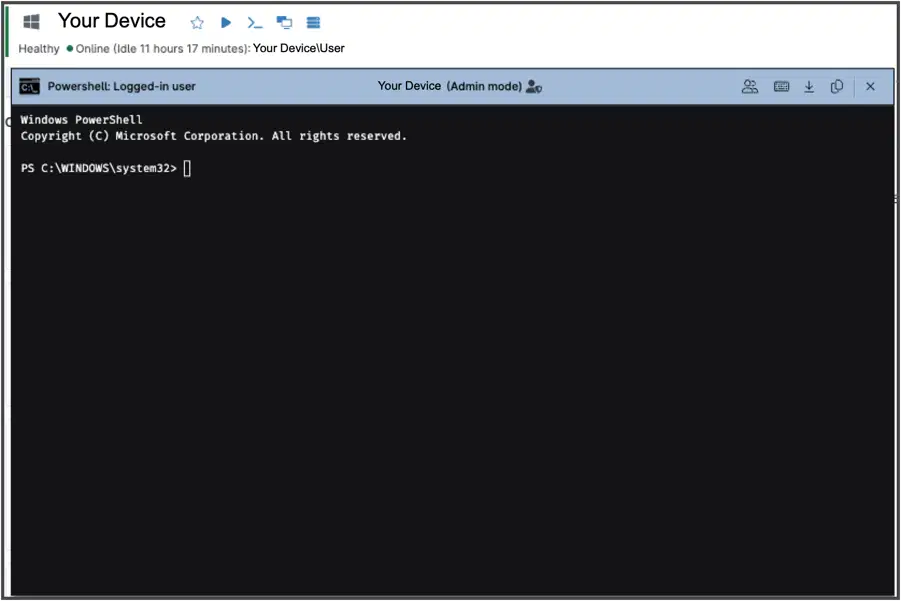
NinjaOne Endpoint Management‘s remote PowerShell lets technicians run commands and scripts on a managed device in real time, without a VPN or a full remote session.

Running a script or command on a remote device often means setting up VPN access or waiting for a full session. Here’s how NinjaOne remote PowerShell addresses the most common cases.
| Problem | How NinjaOne resolves it |
Running a one-off command on a remote device usually means setting up VPN access or waiting for a full remote session just to open a terminal. | NinjaOne opens a remote PowerShell session directly from the console, under a System or logged-in user context, without VPN or a screen-share session. |
Technicians need to run commands with administrator-level privileges without logging in as the end user or disrupting their work. | Sessions default to running as System, or a logged-in user context when needed, separate from whatever the end user is doing on the device. |
Security teams need assurance that remote command execution is restricted to authorized technicians and traceable. | Technician roles control who can open a session, starting one requires multi-factor authentication, and every session is logged for audit and compliance review. |
Running the same script one device at a time through a live console doesn’t scale across a fleet. | The same script can be deployed through the Automation Library across a device policy instead, with a default Run As of System. |
These are the outcomes delivered by NinjaOne remote PowerShell for day-to-day troubleshooting and scripting.
Running a diagnostic or remediation command on a remote device takes seconds, without configuring VPN access or scheduling a session.
Technician roles determine who can open a PowerShell session or use other remote tools on a device, and every session is logged, giving security and compliance teams a clear record of who could access a device and what they ran.
A script that works in a live session can also be deployed across a device policy to reach many endpoints at once.
PowerShell access lives in the same console used for monitoring, patching, and remote tools, so technicians don’t switch context.
The following capabilities describe how NinjaOne remote PowerShell works on a managed device.

Open a PowerShell session on a managed Windows device, or a remote terminal session on a managed Mac or Linux device, directly from the console, without a VPN or a scheduled remote session.

Run commands as System or as the logged-in user, in 32-bit or 64-bit, depending on what the task requires.

Technician roles control who can open a PowerShell session, MFA confirms the technician’s identity at the start of each session, and every session is logged for audit and compliance review.

Run an existing script from the Automation Library inside the session, or write commands directly in the console.

Deploy the same script across a device policy instead of running it one device at a time, with a default Run As of System.

Available as a live PowerShell session on Windows, and as a remote terminal session on Mac and Linux.

Commands run under a system-level or logged-in user context, separate from whatever is on the end user’s screen, so technicians can work without disrupting them.
The following practical applications describe how NinjaOne remote PowerShell gets used in day-to-day support work.
A technician can open a PowerShell session on a managed device to perform troubleshooting actions.
A technician can run a PowerShell command to clear temporary files or old update caches on a device that’s running low on disk space, without scheduling a remote session.
A technician can open a PowerShell session directly from a linked ticket and run a command or script to quickly resolve the issue.
100,000
Endpoints managed
“NinjaOne is a scalable solution. It’s built on a modern SaaS architecture and it’s future-proof.”
40%
More Cost Effective
“NinjaOne’s price point is 40% less than any other endpoint management tool on the market, while being more powerful and easy to use.”
10-15
Tools Replaced
“Before, I needed 10-15 different tools to execute what NinjaOne does in its centralized, single pane of glass.”
30%
Less time for patching
“We observed a 30% reduction in the time taken for patch deployments compared to our previous solution.”
2,000
Endpoints managed
“NinjaOne gives me much more flexibility and security in my work”
30%
Annual ROI
“[NinjaOne] has already shown its value in ROI…it’s at least a hundred thousand dollars annually.”
24x
Faster Endpoint Management
“Our processes have become 24x faster with NinjaOne.”

20-40
Hours Saved Each Week
“Leveraging the automations feature within NinjaOne has enabled me to save upwards of what would likely be 20 to 30 to even 40 hours per week.”
From the device dashboard, hover over the prompt icon to display the drop-down menu, then select PowerShell. Choose the preferred Remote PowerShell session type: System (32-bit), System (64-bit), Logged-in User (32-bit), or Logged-in User (64-bit).
From within a ticket, hover over the play icon next to the device name to reveal the menu, then select PowerShell and then choose the preferred Remote PowerShell session type: System (32-bit), System (64-bit), Logged-in User (32-bit), or Logged-in User (64-bit).
Confirm the session with MFA, then run commands directly or invoke an existing script from the Automation Library.
Every session is logged, so technicians and auditors can review when a technician requested a session.
This overview covers the high-level flow only; full detail is covered in the Command Line Interface (CLI) documentation.
On cutting PowerShell script deployment time:
"Deploying a PowerShell script used to take two hours. With NinjaOne, it takes twenty minutes, plus we can deploy in batches, which we couldn't do before. The time savings is exponential,"
John Pilot, IT Ops Analyst, Major League Baseball Team.
See how NinjaOne lets technicians run PowerShell commands and scripts on managed devices in real time, without a VPN or a full remote session.
Remote PowerShell allows technicians to open an interactive PowerShell session on managed Windows devices directly from the NinjaOne console, without requiring a VPN connection or a remote control session.
Open a Remote PowerShell session from the device dashboard or directly from a ticket. Once connected, enter and execute PowerShell commands on the remote device.
You can run a PowerShell script in a Remote PowerShell session using either of these methods:
Copy and paste: For short, simple scripts, copy the script and paste it directly into the Remote PowerShell session to execute it.
File transfer: For longer or more complex scripts, use the file transfer tool to copy the script to a known location on the remote device, then execute it using one of the following operators:
& (Call operator): Executes the script in its own scope. Variables and functions defined within the script are generally not retained in the current session. Example: & “C:\Scripts\MyScript.ps1”
. (Dot-sourcing operator): Executes the script in the current scope. Variables and functions defined within the script remain available after execution. Example: . “C:\Scripts\MyScript.ps1”
Note: Ensure that the PowerShell execution policy is configured to allow script execution before running a .ps1 file.
No. PowerShell remoting access is built in. Running a script may still require enabling execution for that session with Set-ExecutionPolicy -Scope Process -ExecutionPolicy Bypass.
No. NinjaOne device tags can only be accessed or modified through NinjaOne automation scripts using the Get-NinjaTag, Set-NinjaTag, and Remove-NinjaTag cmdlets. These cmdlets are not supported in interactive Remote PowerShell sessions.
NinjaOne Remote PowerShell is available only for Windows devices. For macOS and Linux devices, NinjaOne provides remote terminal sessions instead.
Yes. Every session requires MFA to start and is logged for audit and compliance review.