Multi-factor authentication with NinjaOne Endpoint Management
NinjaOne Endpoint Management requires multi-factor authentication at sign-in and for administrative actions, with authenticator app, SMS, and security key options
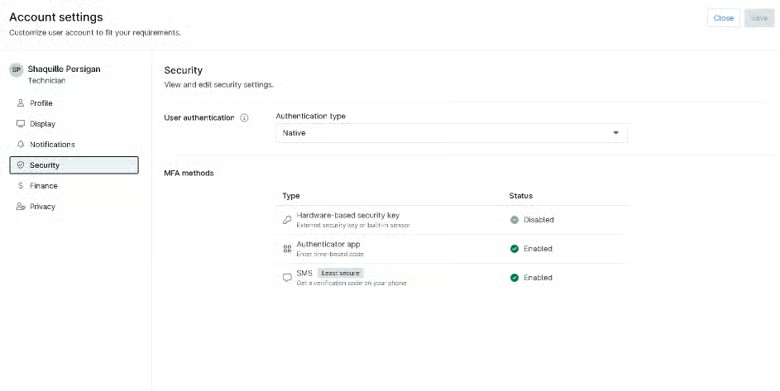
NinjaOne Endpoint Management requires multi-factor authentication at sign-in and for administrative actions, with authenticator app, SMS, and security key options

| Problem | How NinjaOne resolves it |
Passwords alone can leave IT management accounts vulnerable if credentials are stolen or exposed. | NinjaOne requires users to configure and use MFA, adding another verification step at login to help prevent unauthorized account access. |
IT teams need to protect access to sensitive administrative functions, not just the initial login. | NinjaOne requires MFA for administrative actions, adding an additional identity verification step before users can perform sensitive operations. |
Organizations need authentication methods that fit their existing security practices and user workflows. | NinjaOne supports authentication methods including SMS, time-based verification codes, and security keys, giving users options for completing MFA. |
Organizations using single sign-on (SSO) want to maintain strong authentication without unnecessarily repeating MFA challenges. | NinjaOne supports SAML-based SSO integrations and a conditional MFA bypass when the identity provider confirms that MFA was already performed during login, while retaining MFA requirements for administrative actions. |
Reduced risk of unauthorized account access by requiring users to verify their identity with an additional authentication factor, making stolen or compromised passwords less useful to attackers.
Stronger protection for sensitive administrative actions by requiring additional verification when users perform certain actions in NinjaOne, helping reduce the risk of unauthorized changes to managed environments.
More consistent authentication security by requiring MFA for NinjaOne users, helping organizations establish a consistent layer of protection across user accounts.
Fewer blocked sign-ins when users lose access, because system administrators can reset MFA and users set it up again at their next login.
Fewer duplicate prompts for SSO users, because MFA can run once at the identity provider while NinjaOne still requires it for administrative actions.

NinjaOne requires users to configure MFA and verify their identity at login and when performing administrative actions, adding a layer of protection against unauthorized account access.

NinjaOne supports SMS-based verification, time-based authentication, and security keys, giving users different options for completing identity verification.

NinjaOne requires MFA for administrative actions, helping protect sensitive operations even if a user’s password has been compromised.

NinjaOne supports SAML-based single sign-on (SSO) with identity providers, allowing organizations to integrate authentication with their existing identity infrastructure. MFA requirements depend on the identity provider and NinjaOne’s MFA configuration.

NinjaOne can skip its own MFA prompt at sign-in when the identity provider confirms that MFA was completed, which reduces duplicate prompts. MFA cannot be turned off, and NinjaOne still requires MFA for security-sensitive administrative actions after login.
IT teams use multi-factor authentication (MFA) to add another layer of verification when technicians sign in to NinjaOne. Requiring an additional authentication factor alongside a password helps reduce the risk of unauthorized access if login credentials are compromised. This is particularly important for accounts that can access managed devices, remote management tools, and administrative settings.
IT administrators use MFA to add verification when performing sensitive or high-impact actions in NinjaOne. For example, a technician may need to complete an additional authentication step before proceeding with an administrative task, helping reduce the risk of unauthorized changes if an account is misused. This is especially relevant for IT teams and managed service providers (MSPs) whose technicians manage devices and systems across multiple client environments.
IT teams use MFA to help protect access to remote management tools used for troubleshooting and supporting endpoints. By requiring additional verification before accessing applicable remote tools, administrators can add a security check to workflows that may expose sensitive information or allow changes to managed devices. This helps reduce the risk of unauthorized remote access, particularly when combined with appropriate user permissions and configured MFA timeout settings.
100,000
Endpoints managed
“NinjaOne is a scalable solution. It’s built on a modern SaaS architecture and it’s future-proof.”
40%
More Cost Effective
“NinjaOne’s price point is 40% less than any other endpoint management tool on the market, while being more powerful and easy to use.”
10-15
Tools Replaced
“Before, I needed 10-15 different tools to execute what NinjaOne does in its centralized, single pane of glass.”
30%
Less time for patching
“We observed a 30% reduction in the time taken for patch deployments compared to our previous solution.”
2,000
Endpoints managed
“NinjaOne gives me much more flexibility and security in my work”
30%
Annual ROI
“[NinjaOne] has already shown its value in ROI…it’s at least a hundred thousand dollars annually.”
24x
Faster Endpoint Management
“Our processes have become 24x faster with NinjaOne.”

20-40
Hours Saved Each Week
“Leveraging the automations feature within NinjaOne has enabled me to save upwards of what would likely be 20 to 30 to even 40 hours per week.”
All NinjaOne users must perform MFA at login and when performing administrative actions. MFA cannot be disabled. Teams standardize on an authenticator app, SMS, or a hardware security key. NinjaOne prompts each user to set up a primary method after they open the emailed account invitation. Users should add a second method as well, because a hardware key can stop working after a laptop replacement.
System administrators choose how long users can work before NinjaOne asks them to re-authenticate for administrative tasks, including remote connections. The setting applies to every user in the environment and sits under Administration, Accounts, Security Settings.
System administrators can reset MFA for other users, and those users set up MFA again at their next login. Users who saved the key shown under the authenticator QR code can restore access on a new device.
For SSO logins, NinjaOne can skip its own MFA prompt when the identity provider has already completed MFA. This works with supported identity providers, such as Okta and Microsoft Entra ID (formerly Azure AD), and requires the appropriate MFA attribute in the SAML response. Users must still complete NinjaOne MFA for sensitive administrative actions after login.
Strengthening access security for a distributed IT environment
Carahsoft uses NinjaOne’s role-based access controls and single sign-on (SSO) capabilities to support its security requirements while managing thousands of endpoints. These access controls help IT teams manage permissions and protect administrative access as they support a hybrid workforce and maintain compliance with strict security frameworks.
“NinjaOne provides a number of role-based access controls and single sign-on capabilities that allow us to tie into our NIST 800-53 security requirements and deliver a secure platform.”
Ryan Wagoner, Director of Technology, Carahsoft
Protect access to your NinjaOne environment with multi-factor authentication (MFA). Require users to verify their identity at sign-in and during administrative actions, with support for authenticator apps, SMS codes, and hardware security keys. Strengthen account security while helping reduce the risk of unauthorized access if login credentials are compromised.
NinjaOne supports three MFA methods: an authenticator app that generates time-based codes, an SMS code, and a hardware security key. Users choose one as their primary method during setup and add a second as a backup.
Yes. When users sign in through single sign-on (SSO), they can complete MFA once at the identity provider instead of again in NinjaOne.
NinjaOne asks users to verify again before sensitive administrative actions, based on the idle time that system administrators set. This helps protect sensitive actions if a session is left open.
Users add a second method as a backup during setup, so you can sign in with that method if your primary one is unavailable. [CONFIRM: what happens if both methods are unavailable, for example an administrator reset.]
Administrators can run scripts, reboot devices, and perform security actions on managed devices from the NinjaOne console. MFA requires a second verification step, so a stolen password alone is not enough to sign in.