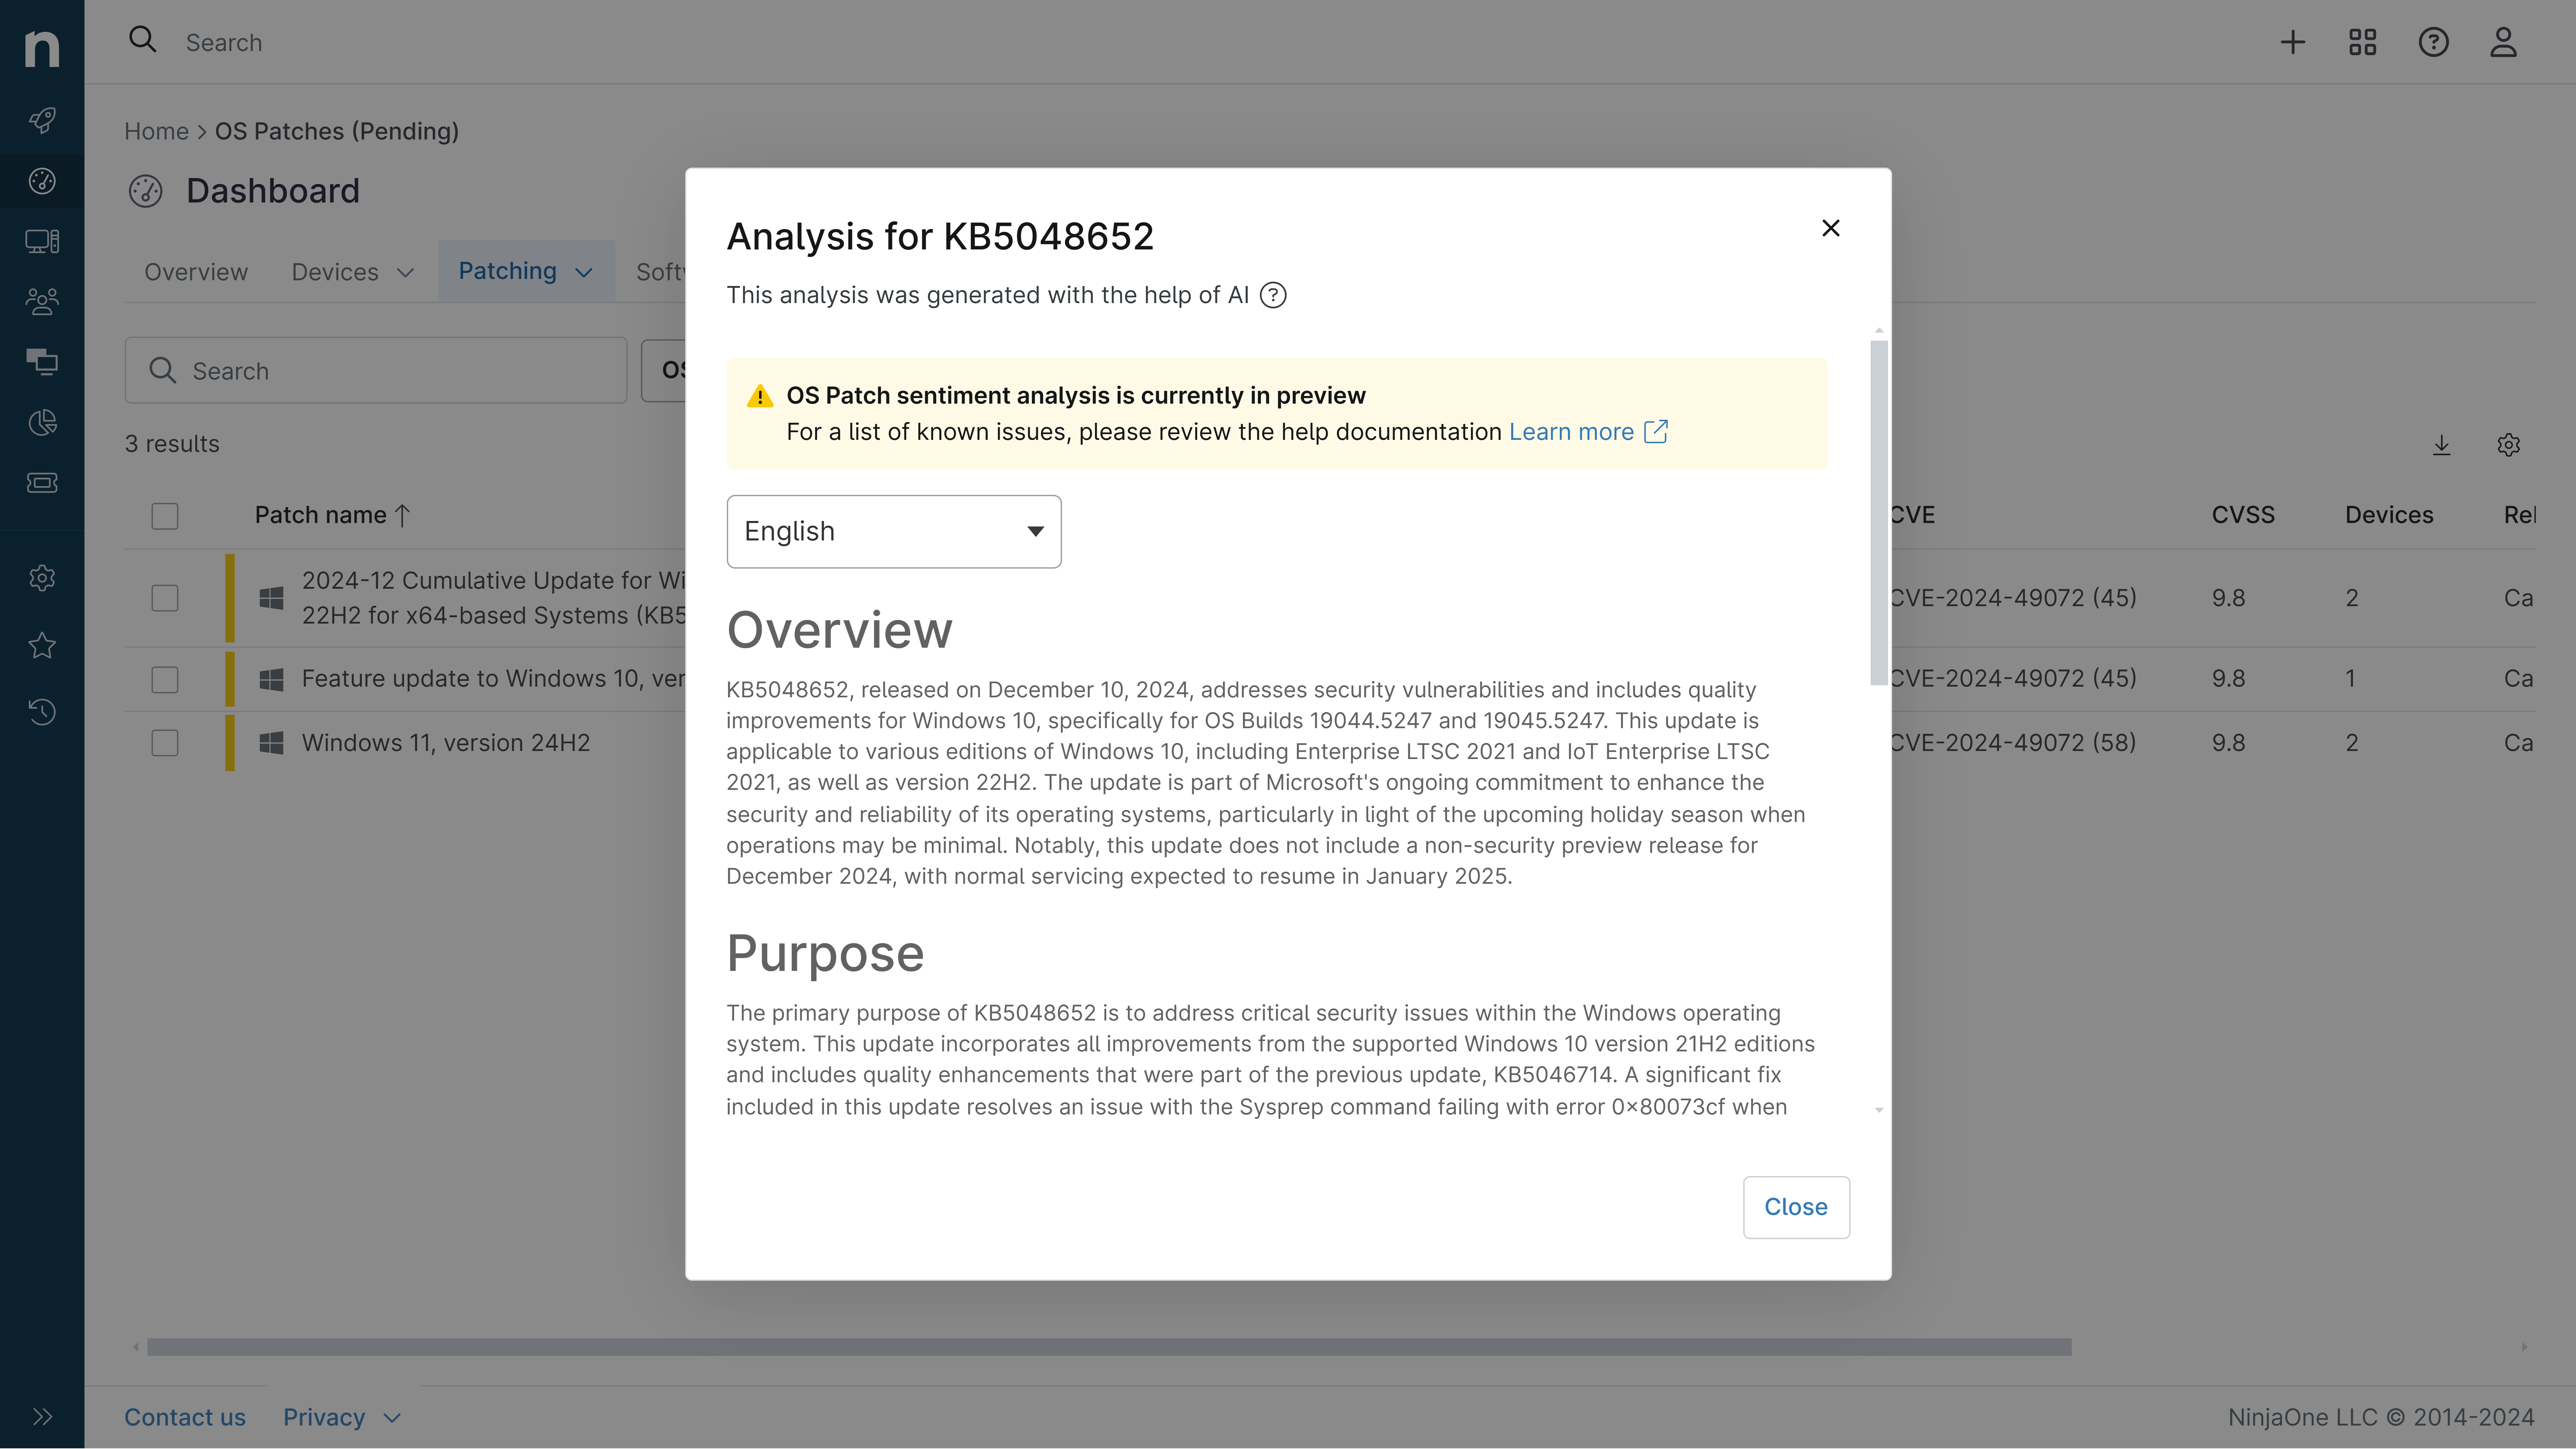
KB5102205: Overview with user sentiment and feedback
Last Updated August 29, 2026
Probability of successful installation and continued operation of the machine
Overview
KB5102205 is a Security and Quality Rollup released on July 14, 2026, addressing vulnerabilities across .NET Framework versions 3.5, 4.6.2, 4.7, 4.7.1, 4.7.2, and 4.8 on Windows Server 2012 R2. This cumulative update targets multiple security flaws including remote code execution, elevation of privilege, denial of service, and tampering vulnerabilities in the .NET Framework.
General Purpose
- Addresses 16 security vulnerabilities including remote code execution (CVE-2026-50649) and elevation of privilege issues (CVE-2026-50646, CVE-2026-50650)
- Resolves multiple denial of service vulnerabilities affecting .NET Framework stability and availability
- Patches a security feature bypass vulnerability (CVE-2026-50304) and tampering vulnerability (CVE-2026-50659)
- Includes quality and reliability improvements for .NET Framework components
- Available through Windows Update, Microsoft Update, and WSUS for enterprise deployment
General Sentiment
Microsoft reports no known issues with this update, indicating confidence in its stability. The patch addresses a substantial number of critical security vulnerabilities, making it a priority security release for organizations running .NET Framework on Windows Server 2012 R2. The availability through multiple distribution channels and automatic deployment options suggests this is considered a safe and necessary update for enterprise environments.
Known Issues
Disclaimer: We take measures to ensure that AI-generated content is of the highest possible quality, but we cannot guarantee its accuracy and recommend that users do their own independent research. Generated on 2026-08-29 01:25 PM