Key Points
- CVE vs. CVSS: CVE identifies vulnerabilities; CVSS scores their severity from 0 to 10.
- Primary Use: Together, they help IT teams assess risk and prioritize patching efforts.
- CVE Info: Provides descriptions, dates, and sometimes solutions for known vulnerabilities.
- CVSS Strength: Quantifies severity to guide remediation order.
- Limitations: CVSS lacks context and updates; CVE may omit fixes and focus only on unpatched software.
- Why It Matters: Despite flaws, CVE and CVSS are essential tools for informed, effective vulnerability management.
Cyberattacks continue to increase significantly year over year. To battle these upcoming threats, effective patching and patch management processes will be essential. Before patching vulnerabilities, there are two main vulnerability assessments that IT teams should focus on: CVE & CVSS scores. Below, we’ll examine the importance of CVE & CVSS scores, along with their uses and benefits in the cybersecurity space.
CVE vs CVSS scores, explained
What is the CVE score?
CVE stands for Common Vulnerabilities and Exposures, and it’s a public list of cybersecurity vulnerabilities. This glossary organizes these security weaknesses by identification number, date, and description..
Well-known examples of vulnerabilities listed in the CVE include CVE-2017-0144 (EternalBlue) and CVE-2014-0160 (the Heartbleed bug of 2014).
What is CVSS
CVSS stands for Common Vulnerability Scoring System, and it’s a numerical score that rates vulnerability severity on a scale from 0 to 10, with 10 being the most severe. It’s often used to rate the severity of the publicly disclosed vulnerabilities listed in the CVE.
Here’s a table showing the CVSS score ranges, arranged by vulnerability severity.
| CVSS Score Range | Severity Level | Description |
| 0.0 | None | No impact; not a vulnerability |
| 0.1 – 3.9 | Low | Minimal impact; low risk to systems |
| 4.0 – 6.9 | Medium | Moderate risk; should be addressed, but not urgent |
| 7.0 – 8.9 | High | Serious risk; requires prompt remediation |
| 9.0 – 10.0 | Critical | Severe risk; immediate action required |
To know how these scores are calculated, you can read more in FIRST (Forum of Incident Response and Security Teams)’s explanation explanation of the CVSS scoring methodology.
Differences between CVE and CVSS scores
CVE and CVSS ratings both assess vulnerabilities. According to the National Vulnerability Database, a vulnerability is “A weakness in the computational logic (e.g., code) found in software and hardware components that, when exploited, results in a negative impact to confidentiality, integrity, or availability.” Before patching a vulnerability, organizations use CVE & CVSS scores to gather more information about the vulnerability and its severity.
| CVE vs CVSS: Key Differences | ||
| Feature | CVE | CVSS |
| Purpose | Identifies vulnerabilities | Scores severity |
| Format | ID (e.g., CVE-2024-1234) | Score (0–10) |
| Managed by | MITRE / NVD | FIRST |
| Output | Description + metadata | Numerical rating |
| Use case | Awareness | Prioritization |
Where to find CVE and CVSS scores
Currently, MITRE manages the CVE database and works closely with the National Vulnerability Database (NVD), which is a part of the National Institute of Standards and Technology (NIST). To find CVSS scores, businesses rely on FIRST, a US non-profit organization.
Uses for CVE and CVSS scores
Today, IT teams rely on CVE & CVSS scores to learn more about security weaknesses before creating strategies to solve them. Some common uses for CVE & CVSS scores include:
-
Quantifying the severity of vulnerabilities
CVSS scores quantify the severity of vulnerabilities. An IT team can use this information to determine which vulnerabilities pose the most serious threats and resolve them first before moving on to more minor weaknesses.
For example, a vulnerability with a CVSS score of 8 is more of a threat than a vulnerability with a score of 3. In this case, the IT team can resolve the vulnerability with a score of 8 first, then resolve the less serious vulnerability with a score of 3.
-
Understanding more about each vulnerability
The CVE provides descriptions, dates, and other information about vulnerabilities. Additionally, the CVE sometimes lists the fixes or solutions for a specific vulnerability. This valuable information allows an IT team to better understand a vulnerability and develop a solution.
-
Supporting patch management efforts
CVE & CVSS scores provide guidance for an IT team and additional support for patch management efforts. These assessments help an IT team to plan, prepare, and resolve vulnerabilities before they become serious issues for an organization.
Have questions about patching? Check out the NinjaOne Patch Management FAQ for detailed answers.
Prioritize and patch the most urgent vulnerabilities with NinjaOne’s automated patching software.
→ Try NinjaOne Autonomous Patch Management for free or watch a demo.
The importance of CVE and CVSS scores
Even though CVE & CVSS scores aren’t perfect, they are currently some of the best assessments to use for vulnerabilities. They allow IT teams to categorize, prioritize, and bring order to pesky vulnerabilities. Additionally, IT teams can rely on both CVE & CVSS scores to gain more insight into security weaknesses and create a plan to resolve them.
Limitations of CVE & CVSS scores
Although some organizations claim that CVE & CVSS scores are overused and overvalued in the cybersecurity space, they remain the best available assessments of vulnerabilities. With that being said, they do have certain limitations as shown below:
CVSS score limitations
-
Inaccurately measures risk
Unfortunately, the CVSS scores assigned to vulnerabilities don’t always accurately measure risk. For example, vulnerabilities scored 7.0 or higher are considered the most serious threats and should be addressed before others. However, are threats scored 6.5 any less dangerous than threats scored 7.0? Sometimes, a 6.5 vulnerability causes more issues than a 7.0 vulnerability.
-
Remains unchanged and unupdated
After a CVSS score is assigned to a vulnerability, it is usually never changed or updated. This static score doesn’t take any changes or new information into account.
-
Omits necessary context
Since a CVSS score is simply a number, it does not provide any context or additional information about a vulnerability. Because of this, it’s difficult to determine how a vulnerability will actually affect a security system.
CVE score limitations
-
Lacks critical information
Although the CVE does provide some information about a vulnerability, it does not provide enough for an IT security team to use to fix the issue. Kenna Security has note CVE records often omit exploit code, known malware, and remediation steps, leaving security teams to track down that information manually across vendor sites and other sources.
-
Ignores threats for patched software
The CVE focuses only on vulnerabilities in unpatched software, ignoring the risks or threats targeting patched software. Just because software is patched does not mean that it’s completely safe from vulnerabilities and threats.
-
Does not always provide a fix
Although it’s common to believe that CVEs offer fixes for vulnerabilities, that’s not always the case. The CVE sometimes provides solutions or fixes for vulnerabilities, but not always.
Explore NinjaOne Autonomous Patch Management
Accelerate vulnerability remediation with intelligent automation powered by Patch Intelligence AI to prevent bad updates and ensure reliable compliance.
Learn more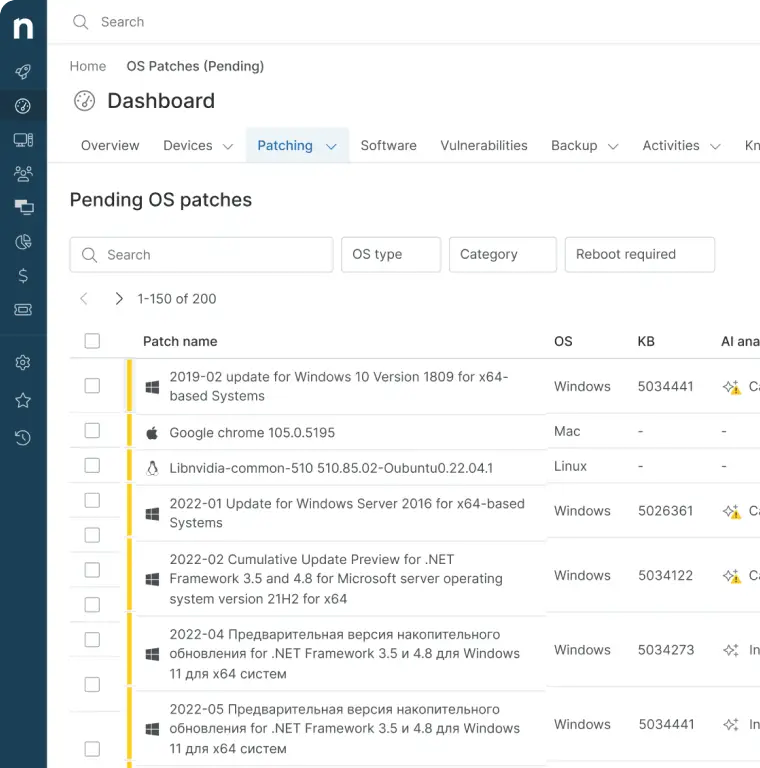
Strengthen your IT security with NinjaOne
Patching and dealing with vulnerabilities is no easy task. That’s why NinjaOne offers an autonomous patch management that automates patching processes from a single pane of glass. With NinjaOne, you can minimize costs, reduce complexity, save time, and remediate vulnerabilities quickly. Get in touch with NinjaOne today to learn more and start your free trial.