Key Points
- Define unmanaged devices as IP-connected endpoints with no installed management agent or endpoint protection.
- Correlate data from network infrastructure, directory services such as Active Directory or Entra ID, and endpoint management tools to find devices missing from your inventory.
- Automate discovery with scheduled scans, because manual comparison of directory and network data is slow and error-prone.
- Prioritize IoT devices, printers, cameras, and BYOD endpoints, which often ship with weak or default security settings.
- Reduce exposure by enforcing onboarding policies, logging unauthorized connections, segmenting the network, and training employees.
Remote and hybrid work environments have compelled businesses to consider how to safeguard their organizations against the increased use of “bring your own device” (BYOD) endpoints and other emerging devices. This is no small challenge, as IT teams and MSPs know. The rise of the remote worker represents one of the biggest changes in the overall cybersecurity landscape we’ve ever seen.
And all these new, remote devices present a unique risk to your clients. When security and IT teams lack full visibility into devices on a network, they can’t set the right security settings and configurations, apply updates, or patch OS and software vulnerabilities.
To discover unmanaged devices, correlate data from your network infrastructure, directory services such as Active Directory or Entra ID, and endpoint management tools, and then use scheduled scans to flag IP-connected devices without a management agent. You can only protect the devices you know about, and unmanaged devices are common entry points for ransomware and infostealers.
In this article, you can learn common methods for identifying and securing undiscovered and unmanaged devices, as well as implementing policies that minimize this particular threat.
What are the risks of unmanaged endpoints?
BYOD and remote workers aren’t a new phenomenon. MSPs have been managing them for years as enterprise networks add a steady stream of new devices outside the IT department’s control. Moves toward mobility and IoT have led to numerous unmanageable endpoints, posing a clear security risk.
Smart lighting, Bluetooth keyboards, smart TVs, surveillance cameras, printers, network switches, and routers are all connected devices that often lack any built-in security. When threat actors probe a network for weaknesses, these devices afford an easily exploitable blind spot.
For instance, unmanaged devices have been proven to be effective entry points for ransomware. A 2024 Microsoft report found that in more than 90% of successful ransomware attacks that reached the ransom stage, attackers used unmanaged devices on the network to gain initial access or to remotely encrypt assets. Likewise, according to Verizon’s 2026 Data Breach Investigations Report, Vulnerability exploitation is now the primary initial access vector at 31% of breaches, and the median time to patch known exploited vulnerabilities rose to 43 days. The numbers prove that an unmanaged device that isn’t tracked and patched stays exposed and is more likely to be exploited by hackers.
What constitutes an “unmanaged device”?
Unmanaged devices are defined as IP-connected devices that lack an installed agent or configuration solution and are not protected by an endpoint agent.
According to a 2025 Enterprise Strategy Group report, respondents said an average of 68% of their organization’s devices are centrally managed by IT or a third-party provider. The remaining devices fall into two categories. “Strategically unmanaged” devices are secured by alternative means, such as zero-trust strategies, VPNs, browser security, or desktop virtualization. “Unintentionally unmanaged” devices go unmanaged because of oversight, lack of visibility, or capability gaps. The research found that 59% of unmanaged devices belong to the unintentional category, which means nearly one in five devices in a given organization is both unmanaged and unsecured.
How to discover unmanaged devices on the network
Finding unmanaged devices isn’t easy. An MSP can’t simply ask Active Directory to show any device not being managed. It’s possible to compare AD data and network management software manually, but this is a time-consuming and error-prone method.
What most MSPs use (or need) is a solution that can automatically correlate and deduplicate data to put them on the fastest road to correcting the problem.
Explore NinjaOne Endpoint Management
Unify visibility and control across all devices to reduce complexity, improve efficiency, and strengthen security all from a single console.
Learn more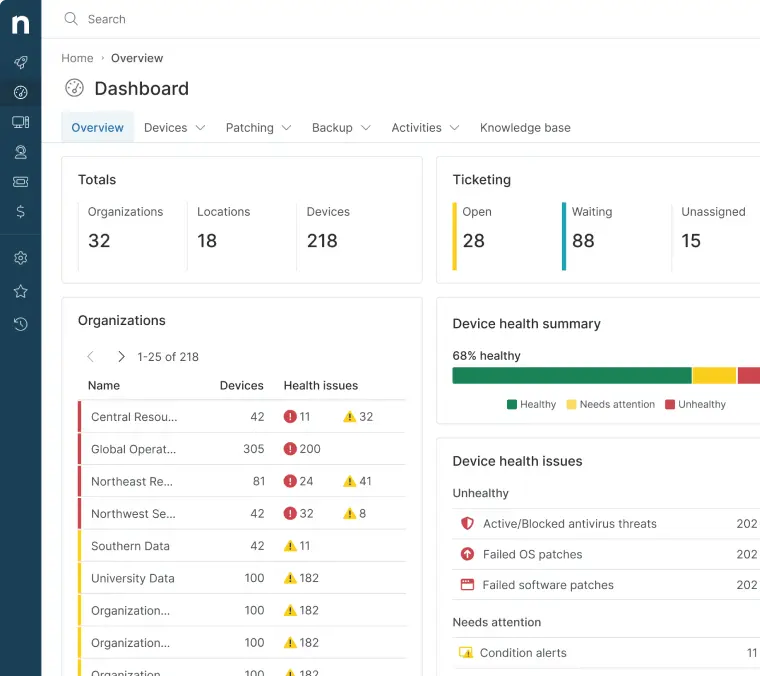
Types of data needed when searching for unmanaged devices
In your typical manual hunt for unmanaged devices, you’ll need the following data sources:
- Network/Infrastructure data: Gain visibility into all devices within an environment by accessing the network infrastructure
- Directory services: Services like Active Directory or Azure AD (rebranded as Entra ID) that authenticate users and devices
- Endpoint management solutions: Like NinjaOne Endpoint Management solution
Using Microsoft Defender to discover unmanaged devices
Microsoft has added the ability to discover and secure unmanaged endpoints and network devices to Microsoft Defender XDR, which consolidates Defender products, including Microsoft Defender for Endpoint, Entra ID (formerly Azure AD), and Security Copilot. Since this is an integrated feature, no hardware or software deployment is required within compatible IT environments.
Once network devices are discovered using this method, IT administrators will receive the latest security recommendations and information on vulnerabilities for those devices. Discovered endpoints can be onboarded to Microsoft Defender for Endpoint.
Native Microsoft solutions carry obvious limitations. Most MSPs require an OS/technology agnostic solution that can discover any device within any environment.
Using NinjaOne to discover unmanaged endpoints
NinjaOne Active Directory Management discovery finds domain-joined computers without an agent and deploys the NinjaOne agent to them, either on demand or on a schedule. For devices that cannot run an agent, such as printers and cameras, NinjaOne IT Asset Management tracks them as unmanaged devices alongside your managed endpoints, with device types defined through custom fields.
NinjaOne network discovery detects other networked devices, including SNMP-enabled hardware. You can group and search every asset by the data NinjaOne collects.
If you want to dive deeper, check out our IT Asset Management FAQ to learn more about ITAM.
How to keep unmanaged endpoints away from the network
In an ideal world, finding and managing unauthorized devices would not be necessary. In real operational networks, however, new devices will always find their way onto the network. MSPs and their clients can take steps to reduce the number of unauthorized and unmanaged devices on the network and identify who is responsible for these devices.
According to the CISA access management FAQ, the following IT inventory management best practices can reduce the number of unauthorized and unmanaged devices that appear on the network:
- Policy can require administrators to put new devices in the desired state inventory before adding them to the network. Often, system administrators connect new devices, then patch and configure them on the production network. This provides a window for the devices to be compromised. Additionally, the devices are often added to the network before being recorded in Active Directory (or any other source of data for the desired state). Getting administrators to keep the desired state up-to-date (edited before the machine appears) will reduce the number of Hardware Asset Management risk conditions.
- Logging can track when unauthorized and unmanaged devices connect to the network, where they connect, and who has logged onto them. All this data can help investigate who connected the devices. Once the person is found, letting them know what is expected can prevent the creation of these risk conditions.
- Employees will need to be trained. There should be consequences for individuals who frequently connect unauthorized devices, even after receiving due warning. While such actions won’t eliminate all unauthorized and unmanaged devices, they can lower the incidence rates, which is a positive step.
Get a clear visual overview—watch the quick video guide: ‘How to Discover Unmanaged Devices (Video)‘.
Unmanaged devices are common entry points for threat actors.
Learn how to automate network discovery for 24/7 protection
Challenges around unmanaged devices
While unmanaged devices pose inherent security risks, several factors can influence the extent of the danger they represent. IT providers and organizations should be aware of these challenges and threat multipliers:
Failure to conduct risk assessments
As with the rest of the network, it’s vital to perform risk assessments on unmanaged devices. Are there any known vulnerabilities or configuration issues? This can be difficult when you can’t put an agent on the device, so a flexible (and tech-agnostic) device discovery tool and agent can be invaluable.
Innately risky devices
Certain devices come with serious issues that will be tough to guard against.
Peer-to-peer networks are notoriously difficult to secure, and research has shown that such devices can be accessed remotely over the internet, even through a firewall, because they are configured to continuously find ways to connect to a global shared network.
It’s essential to evaluate IoT tools and hardware to identify potential risks and prevent P2P exploits. You should also investigate the device’s firmware update policy and keep these devices up to date (as always).
Default configurations/misconfiguration
Configuration issues have led to many data breaches. Widely known default configs can hand cybercriminals the keys to your network. Simple steps, such as changing or deleting the default admin login for your security cameras, can significantly enhance your security. Passwords and credentials should be carefully managed, and users should be wary of undocumented backdoor accounts.
Misconfiguration is another big problem. Aside from access control mishaps, users often leave unnecessary features enabled, such as Universal Plug and Play (UPnP), or inadvertently open ports that can serve as entry points for attackers.
Lack of network segmentation
Putting a firewall between every device and the internet can prevent hackers from side-stepping through the network. IT professionals should implement network segmentation by categorizing unmanaged devices into their own network segments, separate from corporate devices and the guest network. This will stop threat actors from using an unmanaged device as an entry point and then moving laterally to exfiltrate data or install malware. There are ways to bypass segmentation, even if you follow all the network segmentation best practices, but this measure is still worth pursuing.
Poor asset management
Any list of cybersecurity best practices, including NIST’s Cybersecurity Framework, will tell you that identifying all the devices on your network is foundational to security. That’s why IT hardware and software inventory best practices start with a complete, continuously updated list of every asset on the network. It’s not enough just to scan your network for physically connected devices; devices that connect via Wi-Fi and Bluetooth must also be managed.
Lack of continuous monitoring
The majority of unmanaged devices are more difficult to scan than traditional computers connected to a network, so it’s all the more important to monitor their usage and behavior and look for anything suspicious. Log collection, machine learning, and SIEM/SOC all play a role in the modern cybersecurity stack for this key reason.
Start a free trial of the #1 endpoint management software on G2
No credit card required, full access to all features.
Partnering with NinjaOne
Complete visibility is critical to effective management. NinjaOne is here to help IT teams and MSPs manage their business efficiently and securely. Thousands of users rely on our cutting-edge IT operations platform to navigate the complexities of modern IT management.
NinjaOne unifies IT to simplify work for nearly 40,000 customers in 140+ countries. MSPs use the NinjaOne platform to discover unmanaged devices, bring them under management, and track the rest in NinjaOne IT Asset Management.