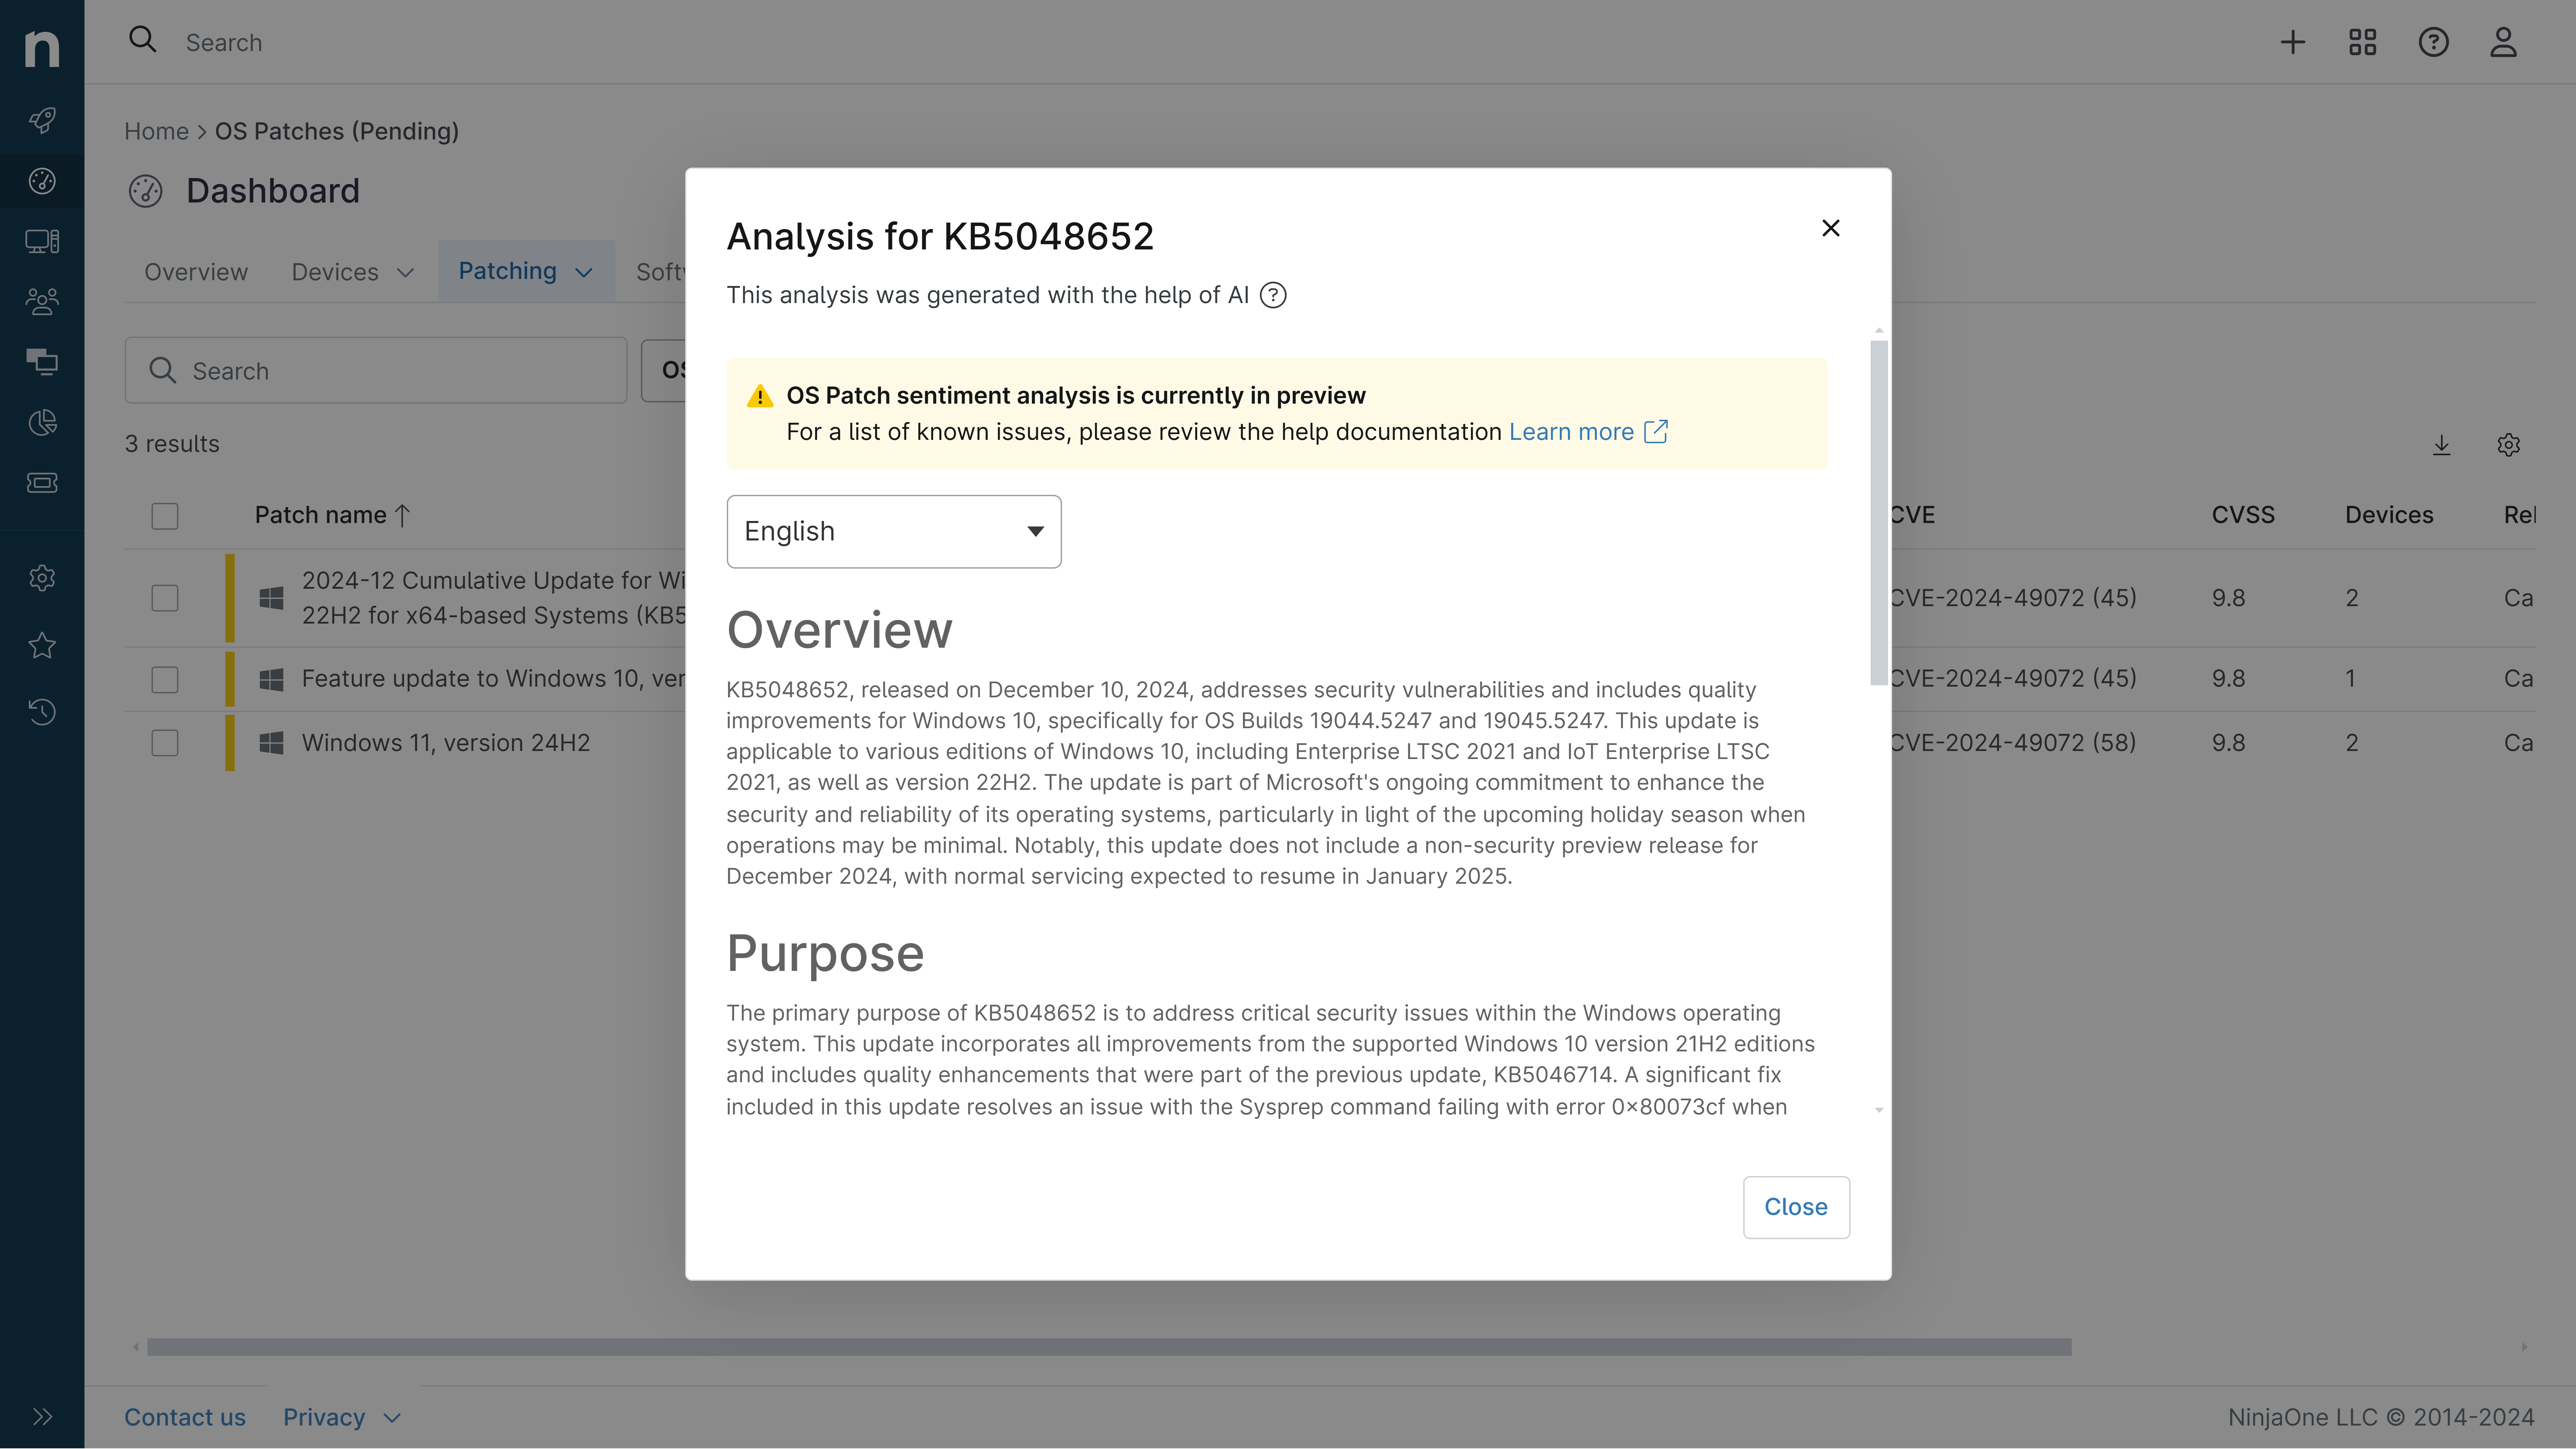
KB5101010: Overview with user sentiment and feedback
Last Updated August 31, 2026
Probability of successful installation and continued operation of the machine
Overview
KB5101010 is a cumulative security and reliability update for .NET Framework 3.5 and 4.8 released on July 14, 2026, targeting Windows Server 2022 systems. This patch addresses multiple critical vulnerabilities including remote code execution, elevation of privilege, and denial of service issues affecting .NET Framework components. The update is recommended as part of regular maintenance routines for affected systems.
General Purpose
- Resolves 16 security vulnerabilities including remote code execution (CVE-2026-50649) and elevation of privilege issues (CVE-2026-50646, CVE-2026-50650)
- Addresses multiple denial of service vulnerabilities across .NET Framework libraries
- Fixes a synchronous HttpWebRequest hang issue occurring in specific secure connection scenarios with certain server configurations
- Includes security feature bypass vulnerability remediation (CVE-2026-47304)
- Provides tampering vulnerability fix (CVE-2026-50659)
General Sentiment
No community feedback or reported issues are currently documented for this patch. The absence of reported problems combined with the comprehensive security coverage suggests this is a standard cumulative update with no widespread adoption concerns. Microsoft has confirmed no known issues at the time of release, indicating a stable initial deployment window.
Known Issues
Disclaimer: We take measures to ensure that AI-generated content is of the highest possible quality, but we cannot guarantee its accuracy and recommend that users do their own independent research. Generated on 2026-08-31 07:30 PM