

Key Points
- Map and audit all personal data stored across endpoints, cloud systems, and third-party SaaS to maintain complete visibility.
- Establish a valid lawful basis and transparent consent mechanisms before collecting or processing any personal data.
- Enforce fundamental security controls, including encryption, automated patch management, and centralized browser monitoring to prevent Shadow IT leakage.
- Conduct Data Protection Impact Assessments (DPIAs) and maintain human oversight when deploying AI models or automated workflows under Article 22.
- Formulate an automated breach response protocol to meet the mandatory 72-hour notification timeline for supervisory authorities.
- Leverage unified endpoint management and backup tools to streamline Data Subject Access Requests (DSARs) and right-to-erasure workflows.
Any organization that collects or processes the personal data of people in the EU must comply with GDPR, regardless of where the business is based. Falling short risks fines of up to 20 million euros or 4 percent of global annual revenue, plus the disruption of an unplanned audit or breach response. This guide breaks down what GDPR compliance requires and how to build a program that meets it.
Ensure GDPR compliance with NinjaOne to streamline data security and incident response.
What is GDPR compliance?
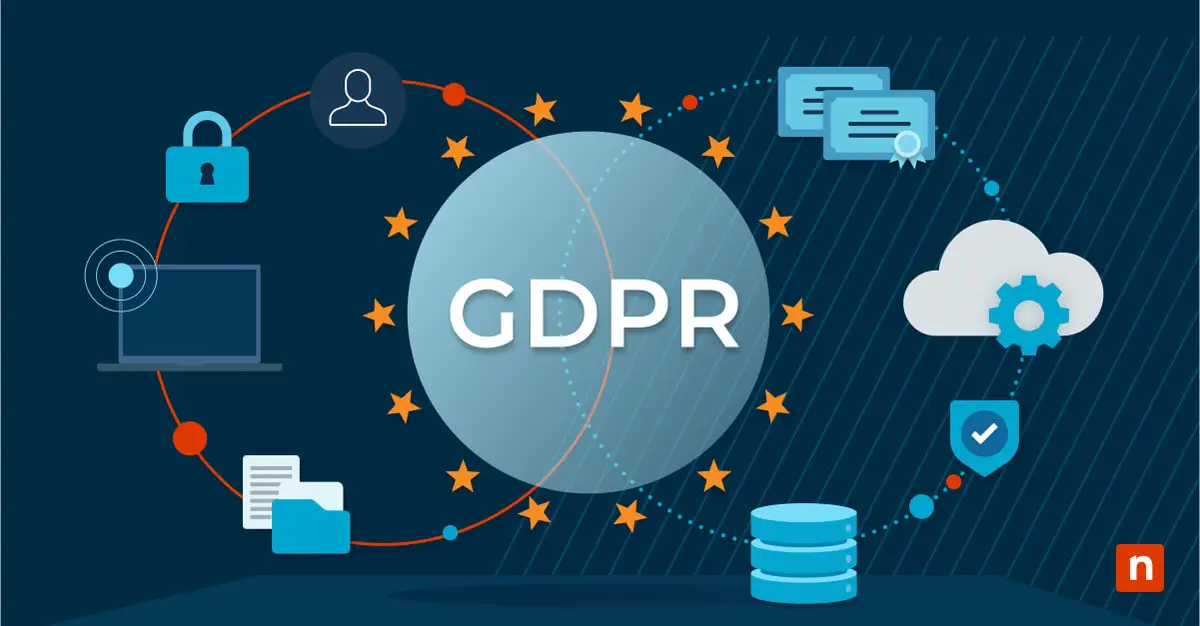
GDPR compliance refers to an organization’s adherence to the rules and requirements outlined in the General Data Protection Regulation (GDPR), a comprehensive data protection and privacy regulation implemented by the European Union (EU) in May 2018. It is designed to give individuals more control over their personal data and to establish consistent data protection rules and practices across the EU member states.
What is the purpose of GDPR?
The primary purpose of the General Data Protection Regulation (GDPR) is to protect the privacy and personal data of individuals. To that end, it sets a comprehensive framework for how organizations should handle personal data and grants individuals greater control over their own data. Here are some of the main purposes and objectives of GDPR:
- Protecting individual privacy: GDPR aims to protect individuals’ privacy and fundamental rights by establishing that their personal data should be processed transparently, fairly, and lawfully.
- Data rights: It empowers individuals with several rights, including the right to access their data, the right to have their data erased (the “right to be forgotten”), the right to data portability, and the right to know how their data is being used.
- Consent: GDPR requires organizations to obtain clear and informed consent from individuals before collecting and processing their data, ensuring that individuals have a say in how their data is used.
- Data security: It mandates that organizations implement appropriate security measures to protect personal data from breaches and sets strict reporting requirements in case of data breaches.
- Accountability and governance: Organizations are required to establish and maintain data protection policies, appoint Data Protection Officers (DPOs), and conduct Data Protection Impact Assessments (DPIAs) to ensure data protection compliance.
- Global impact: GDPR’s scope means that it affects organizations worldwide that process data of individuals within the European Union, making it a global standard for data protection and privacy.
- Penalties and enforcement: The EU GDPR enforces strict penalties for non-compliance, including substantial fines.
Looking at the big picture, GDPR aims to create a more transparent and accountable environment for the processing of personal data, fostering trust between individuals and the organizations that handle their information, and giving individuals greater control over their personal data.
What counts as personal data under GDPR?
Under Article 4 of the GDPR, personal data is defined as “any information relating to an identified or identifiable natural person,” which organizations process either through automated or manual means.
To avoid confusion and misinterpretations, here are some specificities about the given definition.
- Individual vs. company data: As personal data pertains to an individual, data of companies and organizations, usually referred to as “legal persons,” is not considered personal data. Additionally, per the definition of “natural person,” information of a deceased individual does not qualify as personal data.
- Any information: This part implies that personal data can comprise anything, from objective, quantifiable characteristics (ex., Weight, height) to subjective qualities (ex., Testaments, evaluations).
- False, outdated, or incorrect information: Data, regardless of its accuracy, can still count as personal data, as long as it pertains to a specific individual. If the information is wrong to the point that the person cannot be identified, only then does it not count.
Who are affected by the GDPR regulations?
The General Data Protection Regulation (GDPR) affects a wide range of individuals and organizations. Its reach is not limited to the European Union (EU), as it has an extraterritorial scope. Here are some of the key entities that are affected by GDPR:
EU data subjects
GDPR directly benefits and affects individuals who are citizens or residents of the European Union. It grants them enhanced rights and protections regarding their personal data.
Data controllers
Any organization, regardless of its location, that determines the purposes and means of processing personal data is considered a data controller. This includes businesses, nonprofits, government agencies, and any other entity that meets the criteria.
Data processors
Organizations or entities that process personal data on behalf of data controllers are known as data processors. This includes IT service providers (MSPs), cloud services, and marketing agencies, among others.
Data Protection Officers (DPOs)
Certain organizations, particularly those involved in extensive data processing or handling sensitive data, are required to appoint a Data Protection Officer to ensure compliance with GDPR.
EU member state Data Protection Authorities
Each EU member state has its own Data Protection Authority (DPA), responsible for enforcing GDPR within that member state.
International organizations
GDPR applies to organizations outside the EU that offer goods or services to individuals within the EU or monitor their behavior. This means businesses and websites worldwide may need to comply if they deal with citizens of the European Union.
Data subjects’ representatives
Organizations not established within the EU but subject to GDPR may need to appoint a representative within the EU to act as a contact point for data protection matters.
Data subjects’ legal representatives
In certain cases, when data subjects are minors, incapacitated, or deceased, GDPR recognizes their legal representatives who may exercise data protection rights on their behalf.
Third parties
Organizations may need to ensure that third-party vendors and service providers also comply with GDPR when handling personal data on their behalf.
Key GDPR requirements to know
Understanding the key requirements of the General Data Protection Regulation (GDPR) is essential for organizations that process personal data. Here are some of the most important GDPR requirements to be aware of:
- Lawful basis for data processing: Data processing must have a lawful basis, which can include consent, contractual necessity, compliance with a legal obligation, protection of vital interests, the performance of a task carried out in the public interest or in the exercise of official authority, or legitimate interests pursued by the data controller or a third party.
- Principles of data processing: GDPR outlines key principles for processing personal data, including lawfulness, fairness, transparency, purpose limitation, data minimization, accuracy, storage limitation, integrity, and confidentiality.
- Transparency and consent: Organizations must provide clear and easily understandable information to data subjects about how their data will be used. Consent to process data must be freely given, specific, informed, and unambiguous. Data subjects have the right to withdraw consent at any time.
- Data subject rights: A GDPR privacy policy grants individuals several rights, including the right to access their data, the right to have their data erased (the “right to be forgotten”), the right to data portability, and the right to object to certain types of data processing.
- Data Protection Impact Assessments (DPIAs): Organizations must conduct DPIAs when processing operations are likely to result in high risks to data subjects’ rights and freedoms, such as when processing sensitive data or using new technologies.
- Data protection by design and default: Data protection should be integrated into the design and default settings of systems, products, and services. This means privacy considerations should be part of the development process.
- Data breach notification: Organizations must notify the relevant supervisory authority of a data breach within 72 hours of becoming aware of it, and they may need to inform affected individuals in certain cases.
- Data Protection Officers (DPOs): Some organizations are required to appoint a DPO to oversee data protection matters. DPOs should be experts in data protection and independent in their role.
- International data transfers: When transferring personal data outside the EU/EEA, organizations must ensure an adequate level of protection. This might involve using standard contractual clauses or other approved mechanisms.
- Accountability and documentation: Organizations are required to maintain records of data processing activities, have policies and procedures in place for data protection, and conduct regular assessments of compliance.
- Privacy impact assessments: Conducting assessments to evaluate the impact of data processing on individuals’ privacy rights is a key requirement, particularly when introducing new technologies or processes.
- Fines and penalties: GDPR allows supervisory authorities to impose fines for non-compliance, which can be quite substantial, depending on the severity of the violation.
- Consent for children: Special rules apply when processing the personal data of children. Parental consent is usually required for children under the age of 16 (although this age limit may vary by EU member state).
GDPR & AI Governance
With the rollout of the EU AI Act (EUR-Lex AI Act Text) and stricter enforcement around automated data handling, GDPR compliance directly intersects with artificial intelligence (EDPB & IAPP AI Guidance). Under GDPR Article 22, individuals have the right not to be subject to decisions based solely on automated processing or profiling (GDPR Article 22 Text). When deploying AI models or automated workflows that process employee or customer personal data, IT teams must ensure human oversight, clear transparency, and documented Data Protection Impact Assessments (DPIAs).
These are some of the fundamental requirements of GDPR, but the regulation is comprehensive, and organizations should conduct a thorough analysis to ensure compliance.
Ensuring GDPR compliance: checklist and practical steps
Our practical GDPR compliance checklist can help organizations systematically work toward and maintain compliance. Here is a simplified checklist of steps to consider for EU GDPR compliance:
- Data mapping and inventory:
- Identify what personal data your organization collects, processes, stores, and shares.
- Document the purposes for data processing and the legal basis for processing.
- Privacy policies and notices:
- Review and update privacy policies and notices to ensure they are clear and transparent.
- Include information on data subjects’ rights, how to contact your Data Protection Officer (if applicable), and the lawful basis for processing.
- Consent and opt-in mechanisms:
- Ensure that consent mechanisms are explicit, unambiguous, and easy for individuals to withdraw.
- Regularly review and refresh consent where necessary.
- Data subject rights:
- Establish processes for handling data subject requests (e.g., access, rectification, erasure, and data portability).
- Train staff to recognize and respond to data subject rights requests.
- Data Protection Impact Assessments (DPIAs):
- Identify and assess high-risk data processing activities.
- Document the assessments and implement measures to mitigate risks.
- Data security & Shadow IT:
- Implement appropriate technical and organizational measures to protect personal data, including encryption, access controls, and employee training.
- Enforce centralized browser management and SaaS monitoring. Unapproved browser extensions and unsanctioned web apps (Shadow AI) can unwittingly stream EU personal data to third-party servers, causing an unintended GDPR breach.
- Data breach response:
- Develop a data breach response plan, including procedures for reporting and notifying authorities and affected individuals.
- Test the plan through simulations.
- Data processing records:
- Maintain records of data processing activities.
- Include information on data transfers and data protection impact assessments.
- Data Protection Officer (DPO):
- Appoint a DPO if required by GDPR or as a best practice.
- Ensure the DPO is adequately trained and independent.
- Vendor management:
- Review and update contracts with third-party data processors to ensure GDPR compliance.
- Ensure that vendors follow the same data protection standards.
- International data transfers:
- Implement appropriate safeguards for international data transfers, such as Standard Contractual Clauses (SCCs) or Binding Corporate Rules (BCRs).
- Training and awareness:
- Provide GDPR training to employees to ensure they understand their responsibilities.
- Promote a culture of data protection and privacy awareness.
- Records retention and erasure:
- Establish data retention and erasure policies to ensure data is not retained longer than necessary.
- Document erasure requests and actions taken.
- Regular compliance audits:
- Conduct periodic internal audits and assessments to verify compliance.
- Identify and address areas of non-compliance.
- Reporting to supervisory authorities:
- Be prepared to report any data breaches to the relevant supervisory authority within the mandated time frame.
- GDPR documentation:
- Maintain a repository of GDPR-related documentation, including policies, procedures, and records.
- Regular review and update:
- Continuously monitor changes in GDPR regulations and update your compliance efforts accordingly.
- Impact of emerging technologies:
- Stay informed about the impact of emerging technologies on data protection and adapt your policies and practices as needed.
This checklist provides a simplified overview of how to stay GDPR compliant. To ensure comprehensive compliance, it is advisable to consult with legal and data protection experts.
Risks of non-compliance
Non-compliance with the General Data Protection Regulation (GDPR) carries significant financial, legal, and operational risks. Under GDPR Article 83, the regulation utilizes a two-tier penalty structure depending on the severity and nature of the violation:
- Standard Tier (Up to €10 million or 2% of global annual turnover, whichever is higher): Applies to administrative and operational omissions, such as failing to maintain data processing records, omitting required Data Protection Impact Assessments (DPIAs), neglecting data protection by design/default, or missing vendor data processing agreements.
- Higher Tier (Up to €20 million or 4% of global annual turnover, whichever is higher): Reserved for severe infringements impacting core data processing principles, processing data without a lawful basis or valid consent, violating data subject rights, or executing unauthorized international data transfers.
Beyond financial penalties, non-compliance can result in damaged reputation, loss of customer trust, and potential legal actions from affected data subjects. Organizations failing to meet GDPR requirements may also face restrictions or outright bans on data processing.
High-profile enforcement actions highlight the scale of potential regulatory penalties:
- Meta (€1.2 Billion): In May 2023, Ireland’s Data Protection Commission (DPC) issued the largest GDPR fine on record against Meta for unlawful cross-border transfers of EU user data to the U.S. without adequate safeguards (DPC Ireland Meta Decision).
- TikTok (€530 Million): Ireland’s DPC sanctioned TikTok over unauthorized personal data transfers to servers located in China and inadequate transparency policies (DPC Ireland TikTok Decision).
- LinkedIn (€310 Million): Ireland’s DPC fined LinkedIn over concerns regarding valid consent, fairness, and transparency when processing user data for behavioral analysis and targeted advertising (DPC Ireland LinkedIn Announcement).
- British Airways (£20 Million): The UK Information Commissioner’s Office (ICO) fined British Airways following a major data security breach affecting over 400,000 customers (UK ICO British Airways Penalty Notice).
The complexity of GDPR compliance and the potential consequences underscore the importance of taking data protection and privacy regulations seriously, both within the European Union and for entities worldwide that handle the personal data of EU citizens.
Understand how GDPR shapes data protection. Watch what is gdpr compliance? how to stay compliant now.
Take charge of IT and compliance with NinjaOne
As you can see, GDPR emphasizes the importance of taking data protection and privacy regulations seriously. This single regulation, while comprehensive, represents a drop in the bucket of data protection. IT professionals can expect growing expectations regarding privacy and security from their stakeholders, clients, and government agencies as new regulations roll out worldwide.
NinjaOne assists organizations with GDPR compliance by connecting endpoint visibility, security automation, and data protection into a unified platform:
- Data Subject Access Requests (DSARs) & Right to Erasure: NinjaOne’s endpoint backup, file search, and data management tools help IT teams quickly locate, retrieve, or purge specific personal data stored across managed devices to honor user rights efficiently.
- 72-Hour Data Breach Response: Automated patch management, real-time vulnerability monitoring, and endpoint security controls allow teams to remediate security risks proactively. In the event of an incident, continuous auditing and reporting provide immediate forensic data to meet mandatory 72-hour breach notification timelines.
- Browser & SaaS Visibility: Centralized software inventory and policy management give IT teams granular visibility into browser extensions and unsanctioned applications, helping restrict unauthorized web tools and prevent accidental data leakage to unvetted third parties.
By streamlining data mapping, system hardening, and compliance documentation, NinjaOne provides the operational foundation businesses need to navigate GDPR requirements with confidence.
Ready to simplify your data protection workflow?
Schedule a Demo or Start Your 14-day Trial to see why thousands of IT teams choose NinjaOne as their endpoint management partner.
Want more actionable IT guides and industry updates?
Explore the NinjaOne blog for comprehensive technical walkthroughs, or subscribe to the MSP Bento Newsletter to get weekly tools, tips, and inspiration delivered straight to your inbox.