Key points
- Intune manages cloud-based device updates through configuration policies, enabling BYOD and mobile device patching but without direct, granular control.
- WSUS handles direct update distribution; SCCM manages on-prem devices; Intune focuses on cloud-managed endpoints and mobile devices.
- Intune relies on Windows Update for Business to automate updates through policies rather than deploying patches directly, making it best suited for cloud-managed Windows devices.
- Intune is best for organizations with Microsoft-only ecosystems seeking lightweight, cloud-based management for Windows and mobile devices already integrated with Microsoft services.
- Intune alone does not provide comprehensive cross-platform or third-party application patching, so many organizations pair it with a dedicated patch management solution for broader coverage.
- Using Intune for mobile and Windows updates alongside NinjaOne for broader OS and application coverage ensures autonomous patch management and compliance protection.
Yes, Microsoft Intune has some patch management capabilities, but it lacks direct granular patch control and works best for Windows and mobile devices already inside the Microsoft ecosystem.
Patching is a major concern within IT environments. In fact, attacks that exploit unpatched vulnerabilities make up 95% of all cyberattacks. IT teams want to ensure that the IT management tools they choose reliably deploy patches before attackers can exploit security vulnerabilities.
Microsoft’s Intune product family focuses on endpoint management in the cloud, while Microsoft Configuration Manager is used for on-prem management. Intune is also Microsoft’s mobile device management (MDM) and modern management solution.
Prefer video? Watch our visual guide: Does Microsoft Intune Do Patch Management?
→ Learn why NinjaOne is G2’s highest-rated patch management solution
Watch a free demo of the software in action.
Does Microsoft Intune have patch management?
Microsoft Intune does have patch management capabilities. But to help you better understand the product, let’s break down other Microsoft patch management products, like WSUS and Microsoft Configuration Manager, so you can understand where Intune patch management fits into all this.
What is WSUS?
WSUS, which stands for Windows Server Update Services, is a free default role that enables you to distribute and deploy patches using push-style patching. It can be used on the cloud with Microsoft Azure.
Since September 2024, Microsoft has deprecated WSUS, which remains supported and functional through the Windows Server 2025 lifecycle. However, WSUS is no longer receiving new features as Microsoft is steering organizations toward cloud-based alternatives, such as Windows Autopatch, Intune, and Azure Update Manager, for new deployments. Read more about the impact of WSUS deprecation.
What is SCCM?
SCCM, now officially called Microsoft Configuration Manager (ConfigMgr or MECM), is an on-prem endpoint management tool that supports patch management. It relies on WSUS behind the scenes to update metadata and content. IT teams use ConfigMgr to target devices and schedule deployment windows. On its own, WSUS provides limited targeting and reporting, which is why MSPs and enterprises pair it with ConfigMgr.
What is Intune?
Microsoft Intune is an endpoint management tool that works in the cloud and was designed for endpoint bring-your-own-device (BYOD) and MDM. In a roundabout way, it provides patch management using policies and configurations. Unlike WSUS, it operates through the cloud and doesn’t require an on-prem infrastructure, and it doesn’t offer any direct form of patching. It also differs from SCCM because it’s designed for mobile devices, not other endpoint devices.
The product enables you to configure an endpoint, whether it’s a server or a mobile device, and essentially give it directions on how to update itself. This is accomplished using Windows Update for Business. Instead of keeping track of individual updates, you would just need to configure update settings on devices and assign update policy assignments to software. Compared to Microsoft Intune alternatives, this solution lacks granular control over patch management. IT administrators need to integrate Intune with WSUS and SCCM for more advanced patching capabilities.
Additionally, Intune focuses on device enrollment and further user management and control of each device. Though this isn’t related to patching, it’s another way to ensure the safety and security of endpoint devices.
What can Intune patch?
Intune’s patch management capabilities extend past basic update policies and now support:
- Update rings that let users stagger Windows update rollout across device groups, with configurable deferral windows and deadlines.
- Windows Autopatch, a managed service that automates update rings for Windows quality and feature updates, Microsoft 365 Apps, Edge, and Teams.
- Driver and firmware update management for supported OEM hardware.
- Cross-platform update policies for macOS, iOS, iPadOS, and Android, though non-Windows systems have less functionality. However, Intune does not support OS or third-party application patching for Linux systems.
Despite its expanded scope, Intune still lacks the granular control and detailed patch-level reporting that dedicated patch management platforms provide. Intune also lacks native support for patching third-party applications.
Who should use Microsoft Intune’s patch management?
Businesses with an IT environment that relies solely on Microsoft Windows devices benefit from using Intune patching to keep their mobile devices continually updated in the cloud. Additionally, if you’re already using Microsoft tools to monitor and maintain your devices, your organization may find it less of a hassle to add another Microsoft product than to find and implement a new MDM tool.
Advantages of Intune patch management:
- Updates BYODs and mobile devices
- Can set predefined policies for device updates
- Active user management and control of off-prem devices
Microsoft Intune’s patch management functionality is fairly limited. Intune was designed for the management of remote mobile devices, so it lacks support for other types of endpoint. With no direct control over how patches or updates are deployed and applied, a lot is left up to the configurations that were initially set up. Being able to patch the mobile devices most commonly used outside the workplace is crucial for IT teams to safeguard data, secure endpoints, and meet compliance requirements.
Disadvantages of Intune patch management:
- Lacks granular control for patching
- Focus on remote devices leaves general endpoint management
Tools commonly used alongside Microsoft Intune to fill gaps in patch management and remote support
For patching gaps, the most commonly cited pairings are dedicated patch management software that allows users to schedule and deploy third-party applications. Patch management software also gives IT teams greater control over pushing out updates, offers more detailed audit logs of patch status, and often includes vulnerability management tools that can scan for unpatched devices.
When it comes to remote support, Intune has a limited built-in remote access tool, so organizations with more complex help desk requirements typically add a dedicated remote support tool. Some endpoint management solutions, such as NinjaOne, consolidate patch management and remote access capabilities into a single pane of glass, enabling IT professionals to ensure every device has the latest security patches installed and for technicians to troubleshoot and remediate missing patches and other issues remotely.
Complement Intune with NinjaOne Patch Management
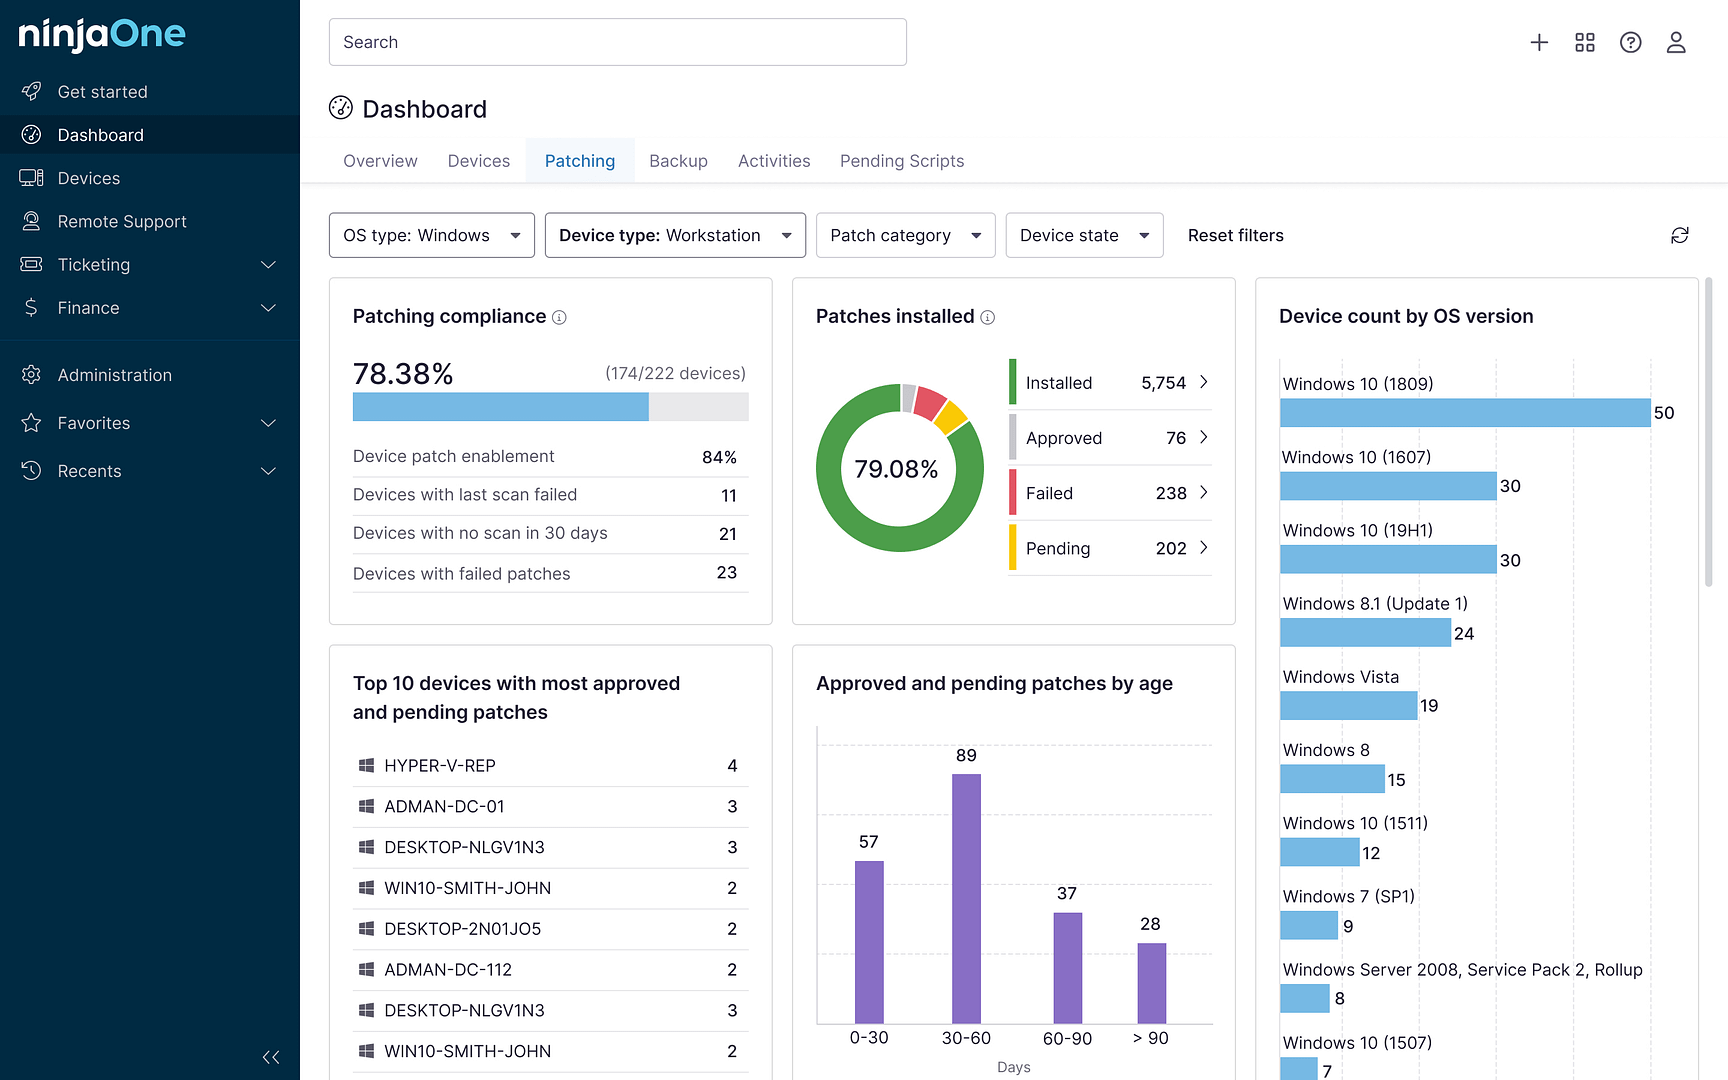
While Intune covers the patching needs of Windows devices in your IT environment, NinjaOne offers autonomous patch management to help you secure the rest of it—endpoints across different operating systems and over 6,000 third-party applications.
Through NinjaOne’s comprehensive and autonomous patching, organizations can
- reduce manual endpoint maintenance on the part of IT teams,
- ensure that their devices are not only secure from cyber threats but also compliant with the latest data protection regulations, and
- focus on more strategic tasks as a result of fewer disruptions and shorter (or even eliminated) downtime.
More notably, NinjaOne’s patching solution comes with Patch Intelligence AI, which detects and pauses unstable or risky updates before they’re deployed, providing additional security and marking a step beyond the usual “set and forget” approach.
Patch management with NinjaOne also serves a different purpose from that of Microsoft patch management. NinjaOne focuses on identifying and remediating endpoint vulnerabilities, while Intune focuses on keeping mobile device systems up to date.
Overall, major features that stand out about NinjaOne’s Patch Management are that it:
- identifies patches for you,
- lets you decide what you do and don’t want to patch in a direct manner,
- reports on patching outcomes, and
- gives you direct control of the overall patching process
In conjunction with Microsoft Intune, NinjaOne provides comprehensive patch management endpoint infrastructure.
Start your free trial of NinjaOne Patch Management today
Get started with NinjaOne Patch Management
Patch management protects your IT environment from external cyber threats. Learn more in our patch management overview, and find out why it’s such a necessary process and component.
NinjaOne’s patch management solution helps you mitigate risk and harden your endpoints. With features like patch automation, patch reporting, remediation tools, and more, you can ensure that you’ve taken the necessary precautions against malware.
See for yourself how much smoother patch management can be with NinjaOne, and sign up for a free trial.