Key points
- Audits get easier with transparent alignment: Compliance mapping is essential for streamlining audits by implementing transparent alignment of policies and controls.
- How to build a compliance map: Catalog controls, map them to frameworks, apply lightweight GRC practices, tagging automation, adding visuals, and regular review.
- Common compliance mapping mistakes: Starting without a complete control inventory, relying on error-prone spreadsheets, leaving control ownership unclear, using unreliable script logs, and presenting outdated visuals.
- RMM software enhances compliance mapping by supporting control inventory with centralized asset and configuration data, reducing manual data collection and spreadsheet maintenance, supporting control ownership tracking, collecting script execution logs, and providing current operational data for reporting.
Facing growing client demands to prove security compliance? Manually tracking controls across multiple frameworks, such as NIST and ISO 27001, often creates confusion and inconsistencies.
This guide will walk you through building a clear compliance mapping of a security framework strategy that simplifies audits and strengthens client relationships through transparent alignment.
Steps to building your cybersecurity framework
A structured approach to cybersecurity framework mapping transforms compliance from a chaotic chore into a scalable, repeatable process that grows with your business.
Use case: Use this methodology when onboarding new clients with specific compliance requirements, preparing for audits, responding to security insurance questionnaires, or whenever you need to demonstrate how your security controls meet industry standards systematically.
Step 1: Build a unified control catalog
Create a master list of your existing security controls to build the foundation of your compliance mapping efforts.
Start documenting your existing security controls, along with their supporting internal policies and technical configurations, grouping them into clear operational categories. Essential controls you need to catalog include:
- Access Control: These are password policies and multi-factor authentication (MFA).
- System Defense: These are your patch management and endpoint protection/encryption standards.
- Data Recovery: These are your documented incident response and backup procedures.
- Monitoring: These are your team’s security logging and alerting practices.
This process organizes your security posture into a structured, reusable library. With a unified catalog, you will have a clear inventory view of your security measures, ready to be aligned with client requirements.
Step 2: Create a spreadsheet mapping matrix
A spreadsheet matrix visually connects your internal controls to specific framework requirements, creating a clear compliance roadmap.
Use this simple table format to cross-reference your controls:
| Internal Control | ISO 27001 Control | NIST CSF Control | SOC 2 Principle |
| Password Policy Enforcement | A.9.4.3 | PR.AC-1 | CC6.1 |
| Vulnerability Management | A.12.6.1 | ID.RA-1 | CC7.1 |
| Endpoint Encryption | A.10.1.1 | PR.DS-1 | CC6.7 |
This completed matrix turns your control catalog into an actionable compliance tool, instantly revealing where single controls meet multiple requirements and highlighting any coverage gaps for your next audit.
Step 3: Apply GRC thinking without the expensive tools
After building your matrix, use your spreadsheet to support key Governance, Risk, and Compliance (GRC) principles and build a stronger, audit-ready system.
Integrate these four lightweight tactics directly into your mapping matrix:
- Gap Analysis: Add a “Status” column to mark framework requirements such as Mapped, Partial, or Gap, for immediate visibility.
- RACI Matrix: Add columns for Responsible (R) and Accountable (A) point persons for every control to clarify ownership.
- Version Control: Use a Last Updated column with dates and initials to record when the mapping was last modified and by whom.
- Review Frequency: Add a Review Cycle column (for example, Quarterly, Annually) to schedule ongoing policy maintenance.
By adding these GRC tactics, your spreadsheet becomes a managed compliance workflow that proactively identifies risks and ensures clear ownership.
Step 4: Automate compliance tagging with PowerShell
Add automated traceability to your compliance documentation with simple PowerShell scripts that link policies to framework controls.
Use this PowerShell script to create an automatic alignment log for your policy files:
$policy = "EncryptionPolicy.docx"$frameworks = @{ "ISO27001"="A.10.1.1"; "NIST_CSF"="PR.DS-1" }foreach ($f in $frameworks.GetEnumerator()) {"$(Get-Date -Format 'yyyy-MM-dd') - $policy maps to $($f.Name): $($f.Value)" | Out-File .\PolicyMapping.log -Append} |
Note: This script creates an automated, timestamped log (PolicyMapping.log) of predefined policy-to-framework mappings. Each entry includes the system date (Get-Date), providing a basic record of when the mapping was logged.
After running this script, you’ll have a log that is updated each time the script runs and records predefined mappings between policies and framework requirements. This log can support documentation of these mappings for client and audit reviews.
Step 5: Use visual aids for reporting and stakeholder reviews
Visual summaries transform complex compliance data into clear, immediate insights for technical and non-technical audiences alike. Use these three visual formats to communicate effectively:
- Venn Diagrams: Show how core controls satisfy multiple frameworks at once.
- Heat Maps: Color-code compliance status (such as Green, Yellow, Red) to highlight coverage gaps in your security policies.
- Spider Charts: Display maturity scores across security domains like Access Control and Detection.
These visuals provide an accessible summary of control mappings and identified coverage gaps. Use them during client onboarding, executive briefings, or audit presentations to communicate your cybersecurity framework mapping without technical overwhelm.
Step 6: Maintain review cadence and client collaboration
Regular reviews ensure your compliance mapping remains accurate and aligned with evolving requirements and client needs.
Schedule mapping reviews during these key moments:
- Quarterly Business Reviews (QBRs) or annual audit cycles
- When frameworks update (for example, new NIST CSF 2.0 requirements)
- After major internal policy changes or security control upgrades
This continuous process creates a compliance system that acts like an ongoing conversation rather than a one-time project. It involves framework reviews directly into your client engagement cycle, keeping it adaptable to changes and client needs.
5 common compliance mapping mistakes to avoid
This section highlights potential challenges to keep in mind while following this guide.
- Skipping the control inventory: Don’t start mapping without a complete list of your security controls, or you’ll miss critical gaps that lead to audit failures.
- Relying on error-prone spreadsheets: Manual data entry creates alignment mistakes that undermine your entire compliance effort.
- Assigning unclear ownership: Controls without designated owners quickly become neglected, creating compliance vulnerabilities.
- Using unreliable script logs: PowerShell scripts without error handling can corrupt your audit trail when permissions or files fail.
- Presenting outdated visuals: Stale diagrams and charts mislead stakeholders and lead to poor security decisions.
Stay compliant by maintaining accurate, current mappings with clear ownership throughout your organization.
5 ways an RMM simplifies compliance mapping
RMM platforms like NinjaOne can automate data collection and monitoring for certain technical controls, supporting compliance mapping and evidence collection.
- Centralize policy documentation: RMM tools, such as NinjaOne with NinjaOne Documentation, can help you store security policies in organized, client-specific folders for easier audit access and document management.
- Tag assets by compliance status: Automatically label endpoints that meet framework criteria (like “NIST-Encrypted” or “HIPAA-Compliant”) for immediate visibility into controls.
- Automate evidence collection: Schedule regular snapshots of patch status, antivirus coverage, and configuration settings to support your control mapping with real-time data.
- Track controls with custom fields: Use custom fields to link assets directly to framework requirements, creating searchable compliance metadata across your entire environment.
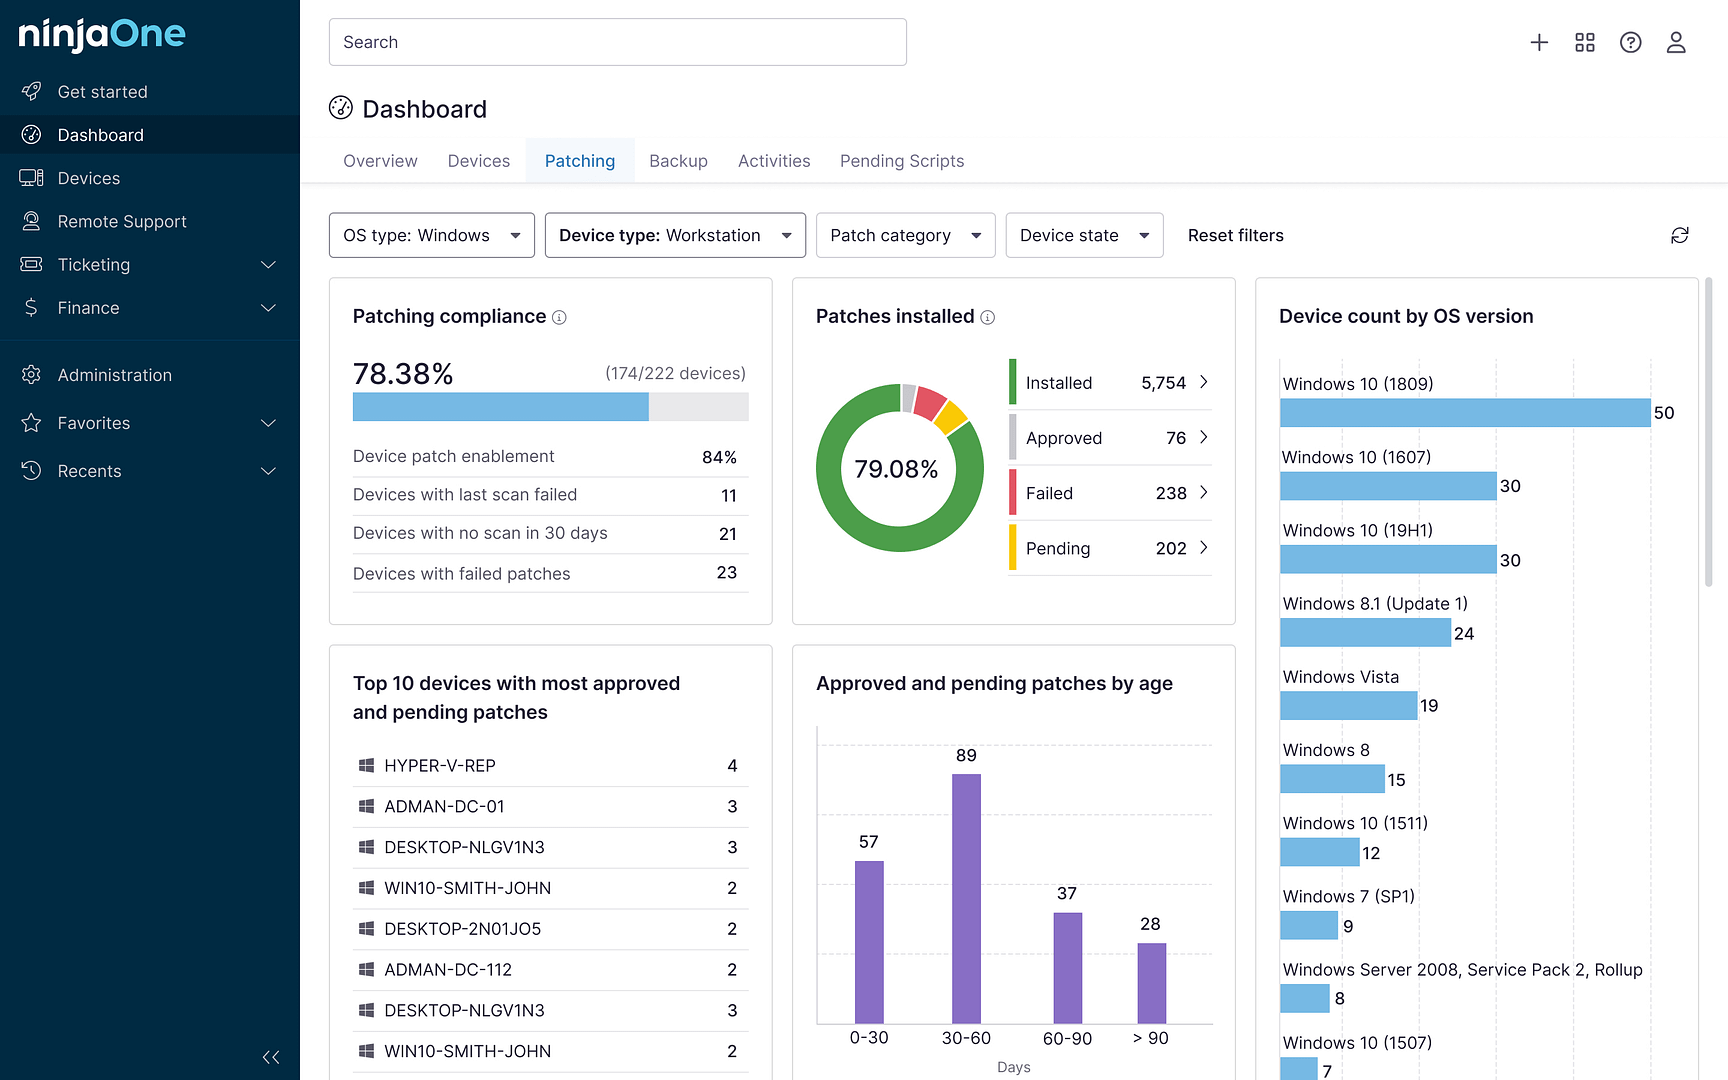
- Generate visual compliance reports: Build dashboard summaries that show how your technical controls map to framework requirements for stakeholder reviews.
NinjaOne turns your manual compliance mapping into a more dynamic system in which operational data can help validate the implementation of technical controls, moving from documented mappings to evidence-supported practice.
🎥 Watch the video guide on Compliance Mapping of Security Framework for MSPs and IT Teams: Align Policies and Controls Without Heavy GRC Tools for a concrete reference.
Ready to turn compliance mapping into proof? NinjaOne can centralize policies, auto-tag control status, and capture audit evidence on schedule.
→ See how NinjaOne automates compliance mapping
Streamline your compliance mapping for lasting success
Effective compliance mapping doesn’t require expensive software, just a structured approach. You can clearly demonstrate how your services meet framework requirements by building a unified control catalog, creating visual spreadsheet matrices, and applying lightweight automation.
This practical methodology transforms compliance mapping from a confusing chore into a scalable process, building client trust and support, and audit readiness through transparent alignment.
Related topics:
- How to Create a Modern Cybersecurity Strategy for IT Departments
- MSP Cybersecurity Checklist 2026: Protect Against Ransomware and Threats
- How To Generate MSP-friendly Compliance Reports From Microsoft Secure Score
- AI Compliance: Balancing Innovation and Governance
- How Human Error Relates to Cybersecurity Risks
Quick-Start Guide
Compliance Mapping Capabilities
NinjaOne offers several features that support compliance mapping and security framework alignment for MSPs and IT Teams:
- Policy Management
- Robust policy management tool with flexible configuration
- Ability to create, inherit, and apply policies across different device types
- Supports granular policy conditions and controls
- Vulnerability Management
- Inventory scanning tool that identifies vulnerabilities
- Compares operating systems and installed applications against the National Vulnerability Database (NVD)
- Supports vulnerability importing and tracking
- Security Framework Support
- Supports various security standards and compliance references
- Provides terminology and management for:
- CVE (Common Vulnerabilities and Exposures)
- CVSS (Common Vulnerability Scoring System)
- Compliance standards like GDPR, HIPAA, PCI-DSS
- Device Policy Enforcement
- Allows policy assignment by location
- Supports inherited policies
- Enables detailed device and application management
- Provides monitoring and reporting capabilities