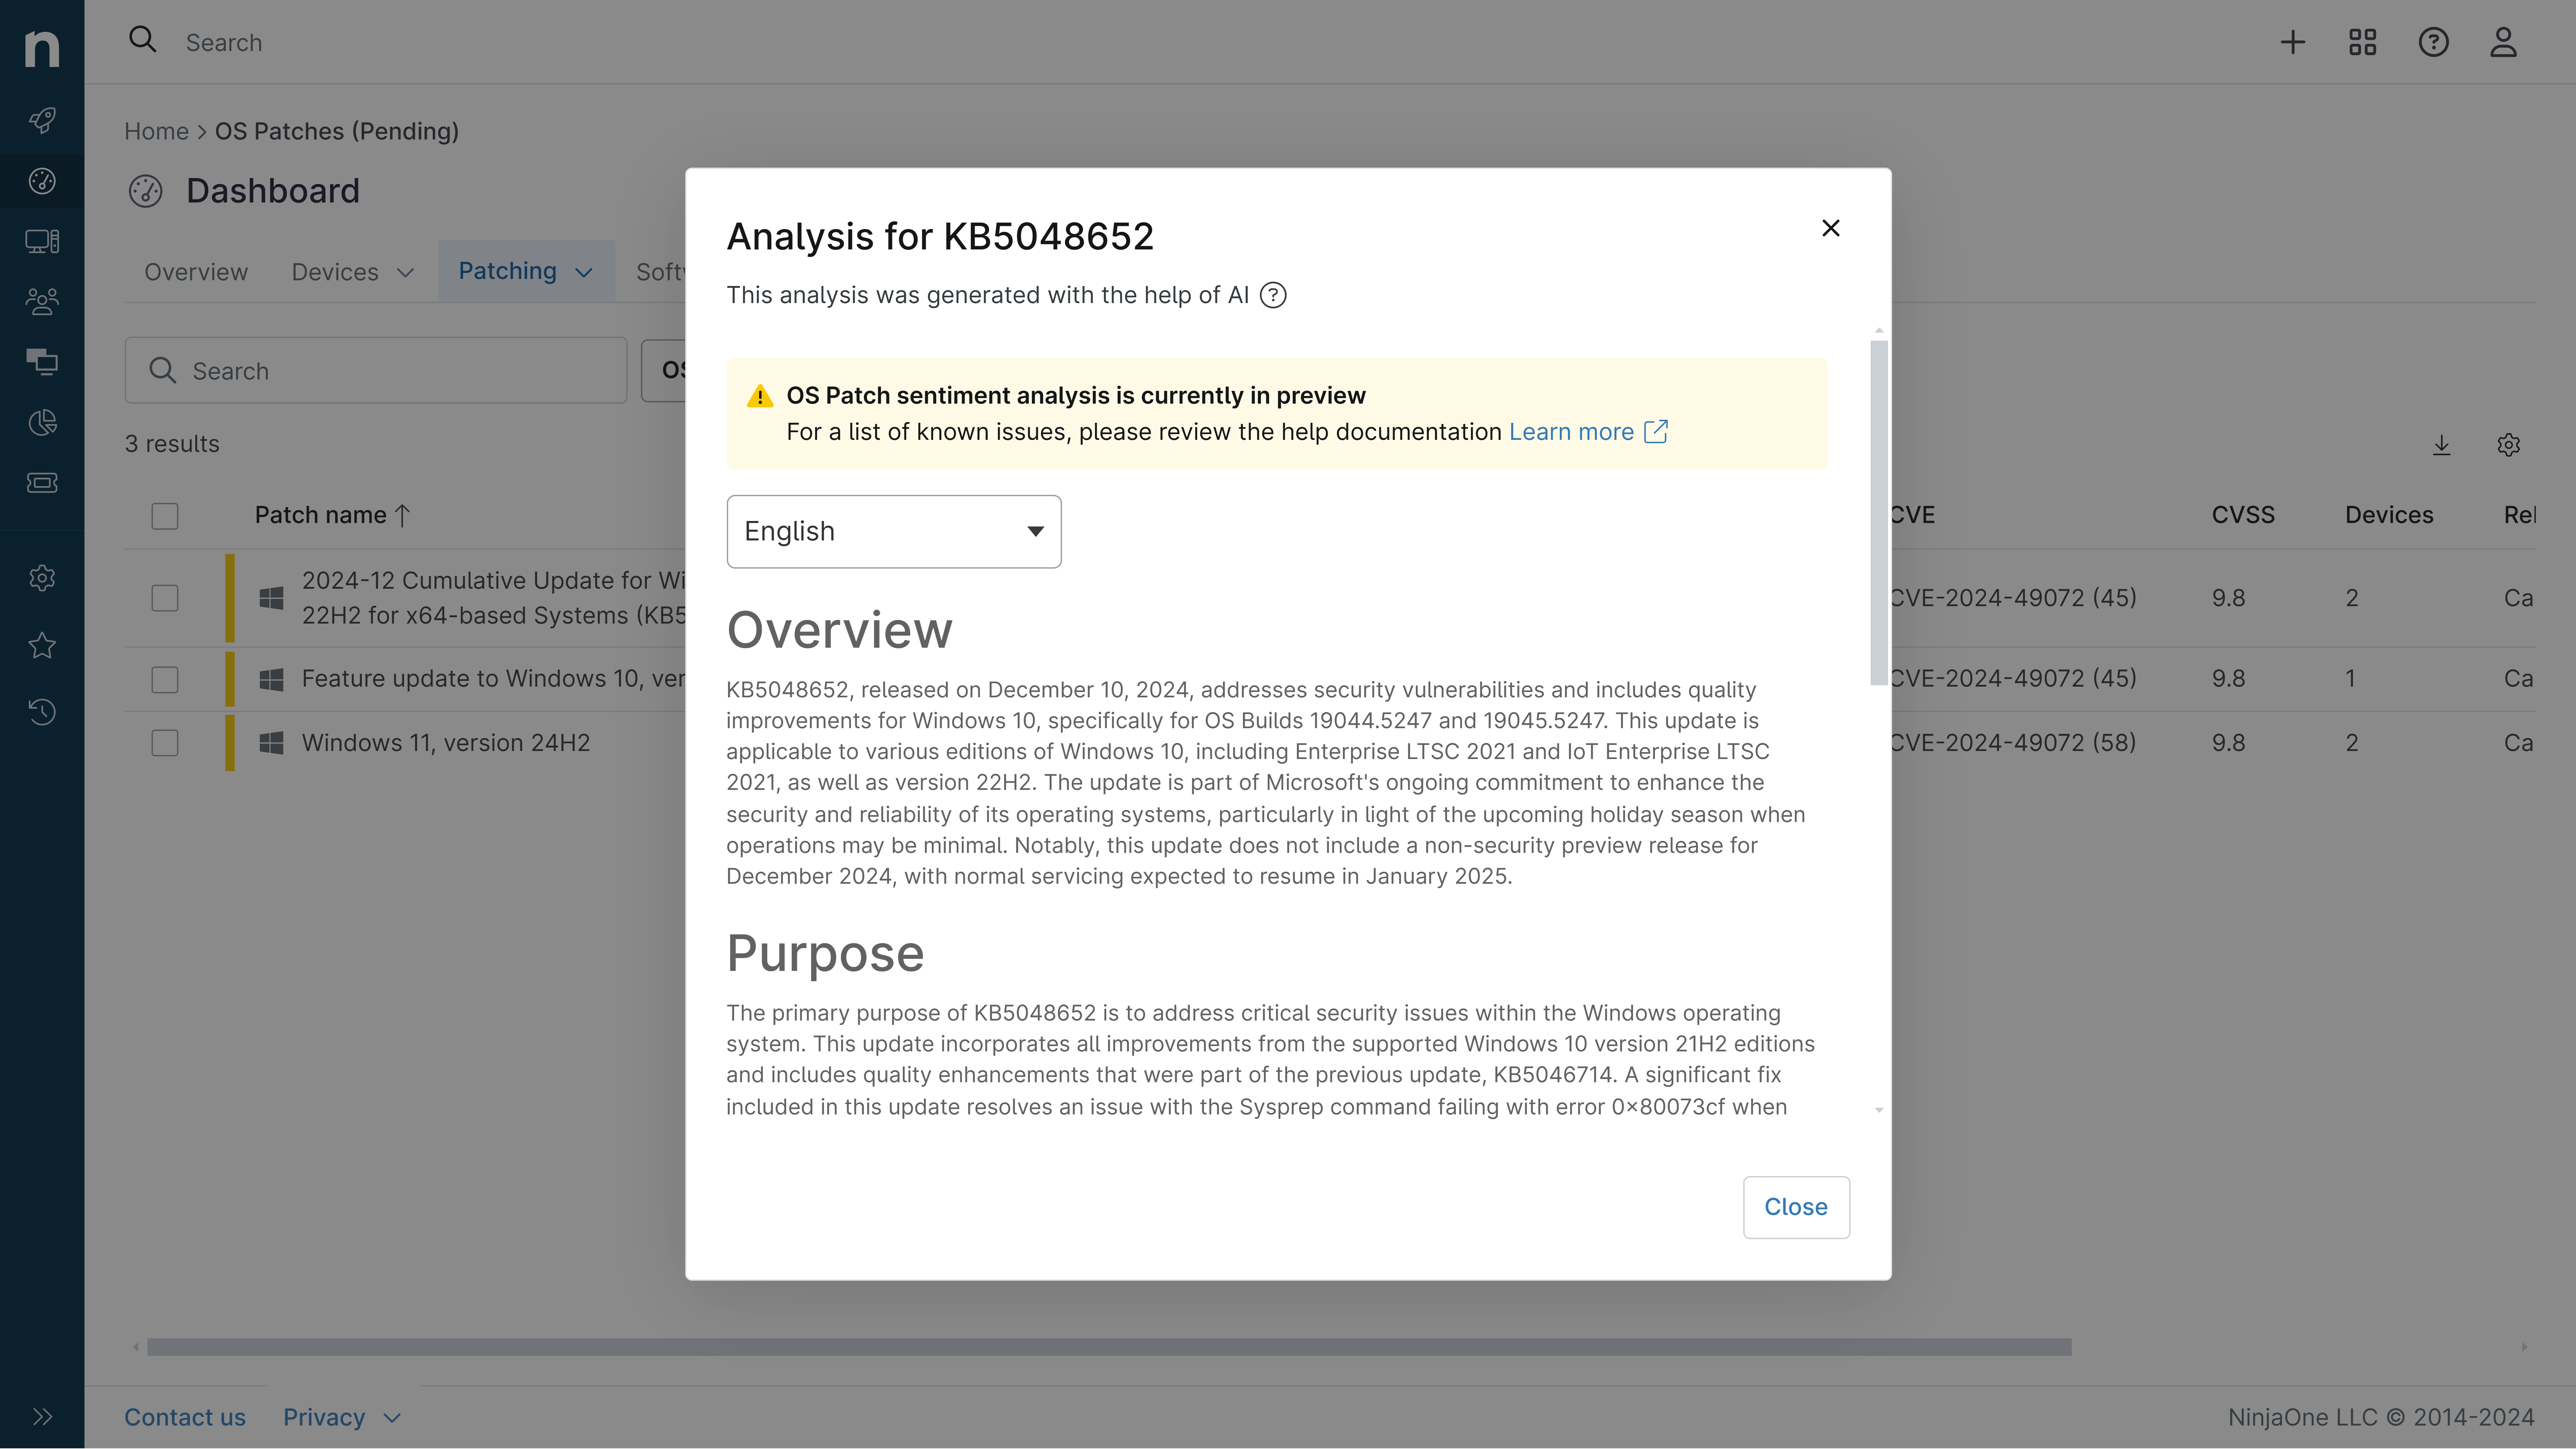
KB5126045: Overview with user sentiment and feedback
Last Updated October 1, 2026
Probability of successful installation and continued operation of the machine
Overview
KB5126045 is a Security and Quality Rollup for .NET Framework 4.6.2, 4.7, 4.7.1, and 4.7.2 released on September 8, 2026, for Windows Server 2012 R2. This update addresses critical security vulnerabilities and provides cumulative reliability improvements to the .NET Framework runtime environment. The patch is part of Microsoft's Extended Security Updates (ESU) program, which provides continued security coverage for Windows Server 2012 R2 until October 13, 2026.
General Purpose
- Addresses CVE-2026-62886: Elevation of Privilege vulnerability in .NET Framework
- Addresses CVE-2026-69522: Remote Code Execution vulnerability in .NET Framework
- Provides cumulative security and reliability improvements for .NET Framework versions 4.6.2, 4.7, 4.7.1, and 4.7.2
- Includes updates to core runtime components (CLR, JIT compiler, and system libraries)
- Available through Windows Update, Microsoft Update Catalog, and Windows Server Update Services (WSUS)
General Sentiment
Limited community discussion is available for this patch, which is typical for infrastructure-focused .NET Framework updates. The patch addresses two significant security vulnerabilities (privilege escalation and remote code execution), making it a priority security update. Microsoft reports no known issues post-installation, indicating a stable release. Organizations running Windows Server 2012 R2 with dependent .NET applications should prioritize this update to close critical security gaps before the ESU support window closes.
Known Issues
Disclaimer: We take measures to ensure that AI-generated content is of the highest possible quality, but we cannot guarantee its accuracy and recommend that users do their own independent research. Generated on 2026-10-01 01:26 AM