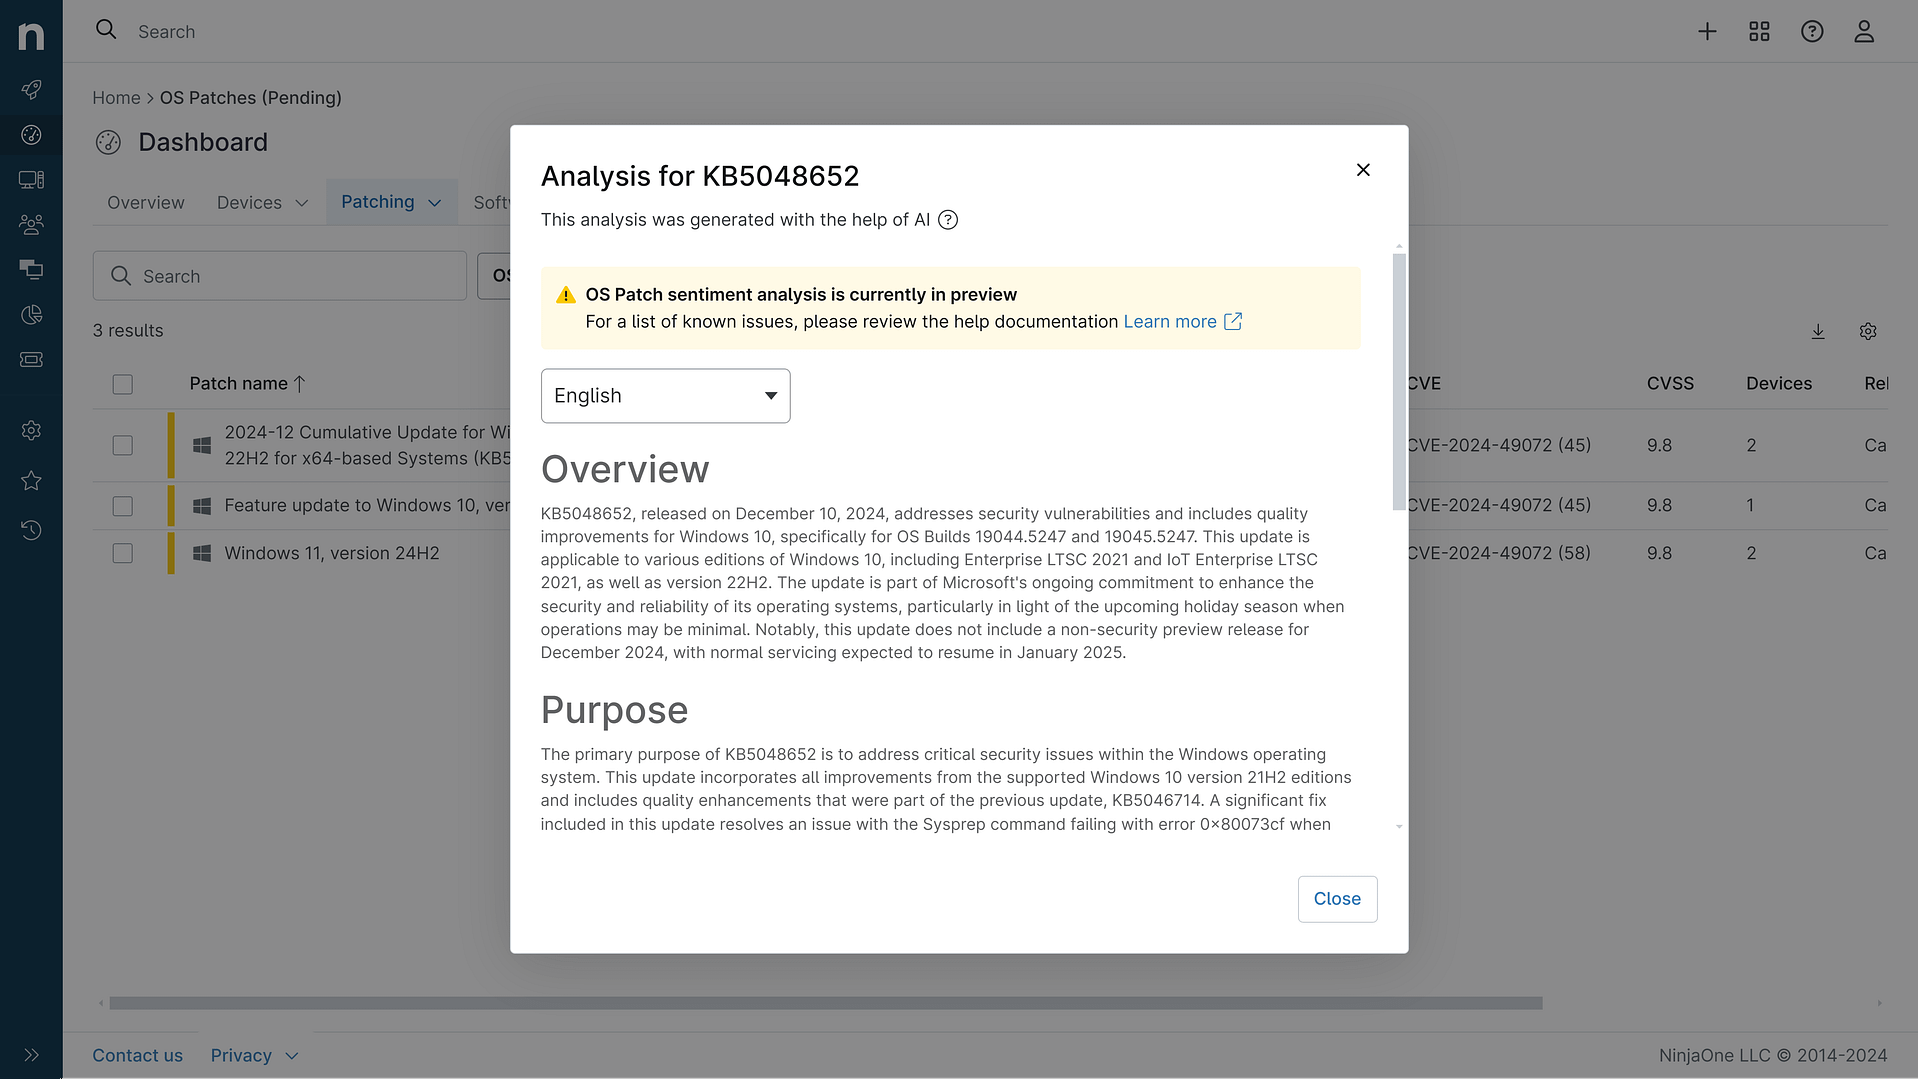
KB5099445: Overview with user sentiment and feedback
Last Updated August 31, 2026
Probability of successful installation and continued operation of the machine
Overview
KB5099445 is a monthly cumulative security update for Windows Server 2012 released on July 14, 2026. This patch addresses multiple security vulnerabilities and quality improvements, including fixes for OLE Automation compatibility issues, Distributed Key Manager (DKM) hardening in AD FS, networking security enhancements, and Remote Desktop Protocol (RDP) security improvements. The update is part of the Extended Security Updates (ESU) program, as Windows Server 2012 reached end-of-support on October 10, 2023.
General Purpose
- OLE Automation Fix: Corrects a compatibility issue in oleaut32.dll affecting applications using IDispatch::Invoke with BYREF parameters, resolving parameter marshaling and automation call failures
- AD FS Security Hardening: Introduces automatic detection and optional remediation for insecure Distributed Key Manager container ACL configurations (CVE-2026-56155)
- Networking Security: Enforces TDI transport registration requirements to strengthen security posture
- RDP Security Enhancement: Adds SHA-2 certificate thumbprint support for trusted RDP publishers while maintaining SHA-1 backward compatibility
- Recycle Bin Fix: Resolves an issue where deletion confirmation dialogs displayed internal file names instead of original file names
- File Explorer Fix: Corrects OneDrive shortcut functionality when File Explorer runs in administrative mode
General Sentiment
This update addresses critical compatibility and security issues discovered in the June 2026 security update. The OLE Automation fix and Recycle Bin correction specifically target regressions from the previous patch, suggesting Microsoft is actively responding to user-reported problems. However, the networking security change introducing TDI transport registration enforcement may cause compatibility issues for applications relying on unregistered third-party TDI transports, which could negatively impact some enterprise environments. The RDP security improvements align with industry best practices for certificate management.
Known Issues
- Applications using sockets over unregistered third-party TDI transports may stop working after installation
- Secure Boot certificate expiration may affect device boot capability if certificates are not updated in advance (separate from this patch but noted as a critical concern for the timeframe)
Disclaimer: We take measures to ensure that AI-generated content is of the highest possible quality, but we cannot guarantee its accuracy and recommend that users do their own independent research. Generated on 2026-08-31 01:34 PM