Key Points
How to Configure Azure AD Connect for Hybrid Identity
- Azure AD Connect integrates on-premises Active Directory with Azure AD, enabling secure hybrid identity and seamless access to cloud services.
- \ Azure AD Connect benefits: It streamlines user management, enhances security, supports SSO, and simplifies cloud adoption by unifying identity across environments.
- How to configure Azure AD Connect: Choose Express for simple, single-forest deployments, or Custom for multi-forest, large-scale, or federated environments, then complete guided setup.
- Use Azure AD Connect Health, sync logs, and force sync options to maintain system health, and regularly update for security and feature fixes.
Azure AD Connect is the Microsoft tool that synchronizes on-premises Active Directory with Azure Active Directory, providing users with a single identity across on-premises and cloud services. Configuring it means choosing an express or custom setup, connecting it to Active Directory, and confirming synchronization, covered step by step below.
What is Azure AD Connect?
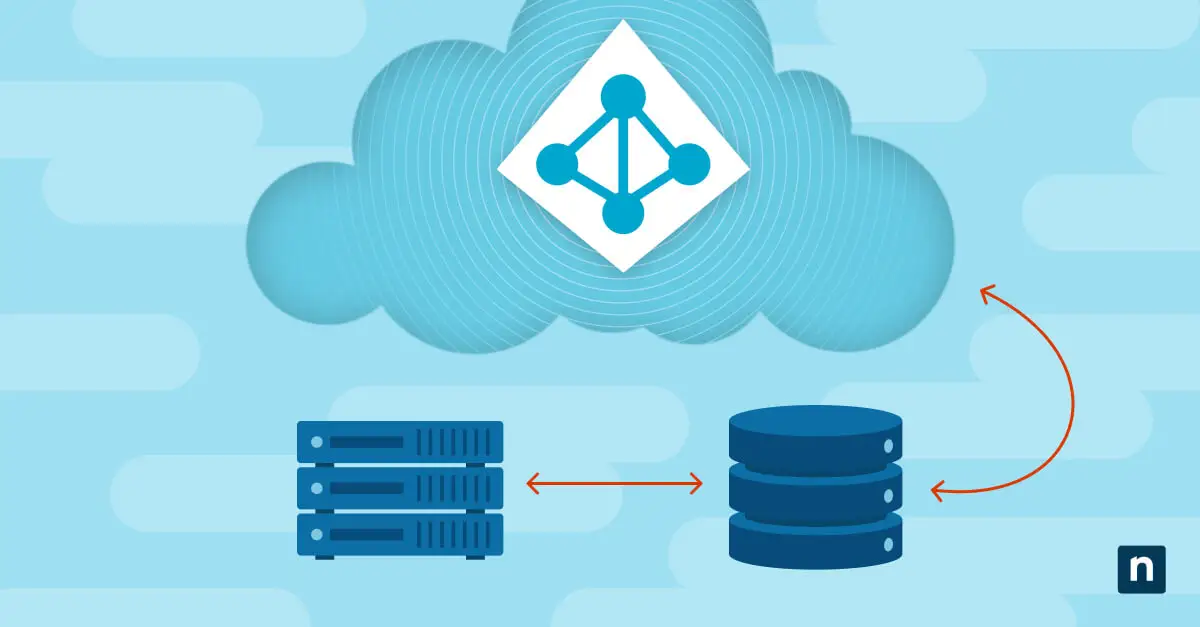
Azure AD Connect, now called Microsoft Entra Connect, is a Microsoft tool that synchronizes an on-premises Active Directory with Microsoft Entra ID (formerly Azure Active Directory). Organizations still running a pre-2.5.79.0 install must upgrade before September 30, 2026, or synchronization will stop; see Microsoft’s version history for the current requirement. It connects the identities and access controls of your local network with Microsoft’s cloud services, providing a consistent user experience across on-premises and cloud directory services. This integration is fundamental to setting up a hybrid cloud strategy and infrastructure that combines the strengths of on-premises and cloud-based identity solutions. Azure AD Connect offers integration, federation, health monitoring, and synchronization.
The benefits of hybrid identity
Hybrid identity is the embodiment of a modern identity and access management strategy, wherein users and resources are managed consistently across on-premises and cloud environments. This approach not only enhances security but also simplifies user experiences. The benefits are substantial:
- Enhanced security: A seamless identity management strategy reduces security risks by providing consistent access controls and authentication across on-premises and cloud-based resources.
- User convenience: With Azure AD Connect, users enjoy a single set of credentials across on-premises and cloud services, resulting in a simplified, intuitive experience.
- Optimized productivity: Centralized identity management streamlines user provisioning and de-provisioning, thereby improving IT efficiency.
- Reduced costs: Hybrid identity removes the need for redundant identity infrastructure, resulting in operational cost reduction.
- Compliance and audit: Compliance is simplified with uniform identity policies across environments, and audit capabilities are centralized.
- Painless cloud adoption: Hybrid identity makes the transition to the cloud painless by reducing disruption from legacy connectivity.
Key features of Azure AD Connect
Azure AD Connect offers features that make it an indispensable part of identity integration infrastructure, including:
User and group synchronization
Azure AD Connect achieves identity synchronization between on-premises Active Directory and Azure Active Directory, ensuring that user accounts, groups, and attributes are consistent and in both environments. This ensures that users have the same access rights and group memberships in both locations, minimizing inconsistencies and improving security. Synchronization can be unidirectional (from on-premises to the cloud) or bidirectional, allowing for a more flexible configuration.
Password hash synchronization
To further enhance security, Azure AD Connect supports password hash synchronization. This feature allows users to sign in with their on-premises passwords when accessing cloud resources, without exposing the actual password. Password hash synchronization is a crucial element in maintaining a secure hybrid identity environment.
Seamless single sign-on (SSO) experience
Azure AD Connect provides a seamless single sign-on experience for users, eliminating the need to remember multiple passwords for on-premises and cloud resources. With SSO, users can log in once, and Azure AD handles authentication for all connected services, optimizing user experience and security by reducing the overhead of password management.
Support for multi-forest and custom configurations
Azure AD Connect is a versatile integration tool that caters to the diverse configuration requirements of modern organizations. It supports advanced Active Directory deployments, including multi-forest scenarios, enabling synchronization from multiple Active Directory forests to Azure AD. Additionally, it offers a number of custom configuration options to tailor the synchronization process to specific organizational requirements.
Best practices for Azure AD Connect implementation
Before we get into the setup of Azure AD Connect, proper planning should also consider established best practices. The following will provide a solid foundation upon which to build and operate your hybrid identity infrastructure:
- Verify network connectivity and firewall settings: Ensure that the required ports and protocols are allowed through firewalls and that reliable communication exists between your on-premises Active Directory and Azure AD. A secure and robust network setup is fundamental for a successful implementation.
- Review synchronization results: Conduct continuous monitoring and review of synchronization results and error reports to maintain a healthy hybrid identity environment. Timely detection and resolution of issues ensure that user identities and access controls remain consistent and secure.
- Backup configuration settings and customizations: Regularly back up your Azure AD Connect configuration settings and customizations. In the event of a failure or the need to reinstall Azure AD Connect, having configuration backups ensures you can quickly restore your synchronization setup, minimizing disruption.
Setting up Azure AD Connect
Prerequisites and system requirements
Before beginning an Azure AD Connect installation, it is vital to understand the prerequisites and system requirements. These include:
- Azure subscription: An Azure subscription is mandatory to utilize Azure AD Connect.
- On-premises server: A domain-joined server running Windows Server 2016 or later.
- Active Directory: A functional on-premises Active Directory to synchronize with Azure AD is also required. It must be running a schema version and forest functional level of Windows Server 2003 or higher.
- Software: The .NET Framework 4.6.2 and PowerShell 3.0 or later must be installed on the Azure AD Connect server.
- Azure AD tenant: An Azure AD tenant should be set up and configured to provide a synchronization partner for on-premises Active Directory. A verified domain name is also required.
- Minimum system requirements: Ensure that the server on which Azure AD Connect will be installed meets the system requirements, including operating system compatibility, disk space, and memory.
Downloading the latest version of Azure AD Connect
Staying current with software versions is crucial for security and feature updates. You can download the latest version of Azure AD Connect from the official Microsoft website. It is especially important to stay vigilant about updates and security patches for identity and access management systems, as patches often include critical enhancements and bug fixes that address vulnerabilities that might otherwise undermine your security posture.
Installation process step-by-step
The installation process for Azure AD Connect is straightforward, but attention to detail is essential to ensure a smooth setup. The first decision to make is whether to choose an express or custom installation:
- Express: Azure AD Connect Express setup is suitable for environments with a single Active Directory forest and fewer than 100,000 objects. Express setup enables single sign-on by using password hash synchronization from on-premises to Azure.
- Custom: Azure AD Connect custom setup is required for deployments with multiple on-premises AD forests or more than 100,000 objects in a single forest. The custom setup option also enables federation, pass-through authentication, and group-based filtering.
The following steps provide a basic overview of the express installation process:
- Launch the installation wizard: Run the Azure AD Connect installation wizard.
- Accept terms and conditions: Review and accept the license terms and conditions.
- Installation type: Select the installation type, with options for custom configurations if needed.
- Azure AD sign-in: Sign in with your Azure AD global administrator account. It may be necessary to add URLs to trusted sites to avoid errors.
- Connect to AD DS: Establish a connection to your on-premises Active Directory.
- Azure AD sign-in configuration: Using single sign-on requires a verified 365 domain. If the installation fails to detect a qualifying UPN suffix, setup can continue without matching all suffixes by checking a box.
- Ready to Install: Review the configuration settings and click ‘Install’ to proceed with the installation.
Configuration options and custom settings
During installation, you have the opportunity to configure various settings to tailor Azure AD Connect to your organization’s needs. These options include selecting the source anchor attribute, configuring user and group filtering, and defining custom settings for user provisioning and password writeback.
Configuring synchronization
After the initial setup, Azure AD Connect needs to connect to your on-premises Active Directory. This connection is crucial for synchronization to work correctly. The configuration wizard guides you through this process, allowing you to specify the domain controllers to use for synchronization.
Filtering options allow you to control which users and groups are synchronized to Azure AD. This is essential for organizations with large directories or complex Active Directory structures. You can filter based on organizational units, domains, and specific attributes.
Synchronization schedules can be configured to ensure that changes in your on-premises Active Directory are regularly and promptly reflected in Azure AD. Scheduled synchronization helps maintain consistency, minimize delays in user provisioning and deprovisioning, and optimize security throughout the hybrid identity infrastructure.
The initial synchronization process may take some time to complete, especially for organizations with large directories. Azure AD Connect is designed to handle this scenario efficiently, but it is wise to monitor the process and ensure it progresses without issues.
Advanced configuration and customization
Azure AD Connect provides several configuration and customization options for more complex environments, each catering to specific use cases. Some of the more popular options are:
Password writeback for self-service password reset
Azure AD Connect offers the option to implement password writeback, a feature that allows users to reset their passwords through Azure AD, and have the new password written back to the on-premises Active Directory. This feature enhances user self-service capabilities and streamlines password management.
Attribute mapping and transformations
Organizations often have specific attribute requirements for their users in Azure AD. Azure AD Connect enables fine-tuning of attribute mappings and transformations, ensuring that user attributes align with your organization’s needs, previous customizations, and security policies.
Group writeback and device registration
Azure AD Connect supports optional features such as group writeback and device registration. Group writeback allows groups created in Azure AD to be synchronized back to the on-premises Active Directory, while device registration ensures seamless integration of devices into your hybrid identity solution.
Monitoring and troubleshooting
Azure AD Connect provides several; tools for monitoring performance, each playing a vital part in the efficient operation of hybrid identity services:
- Azure AD Connect Health: Azure AD Connect Health is a vital tool for monitoring the health and performance of your Azure AD Connect installation. It provides insights into synchronization status, alerts for potential issues, and performance data. Monitoring with Azure AD Connect Health is essential for maintaining a healthy hybrid identity environment.
- Synchronization logs: Synchronization logs contain valuable information about the status of your synchronization process. Understanding these logs and addressing common errors is essential for troubleshooting. Common synchronization issues may include conflicts in attribute mapping, network problems, or issues with the Active Directory schema.
- Force sync: In some cases, you may need to trigger synchronization outside the regular schedule. Azure AD Connect provides options to force synchronization when needed.
Updating Azure AD Connect
Staying current with Azure AD Connect is crucial ito benefit from security enhancements, new features, and bug fixes. Microsoft regularly releases updates to address vulnerabilities and improve functionality. Keeping your installation up to date is vital for a secure identity management solution.
Check regularly for the latest version of Azure AD Connect and associated updates on the official Microsoft website. Review the release notes to understand the changes and improvements in each version. Once you decide to upgrade, plan the process carefully to minimize downtime.
Note: Any installation running a version earlier than 2.5.79.0 will stop synchronizing entirely on September 30, 2026. This is a mandatory security-hardening upgrade, not an optional feature update. If you’re below 2.5.79.0, download the latest release from the Microsoft Entra admin center, as the installer is no longer distributed outside of it.
Once the cutoff hits, sync fails until you update, with no grace period.
If you manage this for clients or your own environment, check your installed version now:
- Open the Synchronization Service Manager console
- Go to Help > About
- Alternatively, you can also check Windows Settings > Apps > Installed apps and search for “Microsoft Entra.”
Establish robust hybrid identity services
This comprehensive guide has equipped you with the knowledge needed to understand Azure AD Connect and to configure it securely. With these tools, you can establish and maintain a robust hybrid identity environment that enhances security, user experience, and organizational productivity.