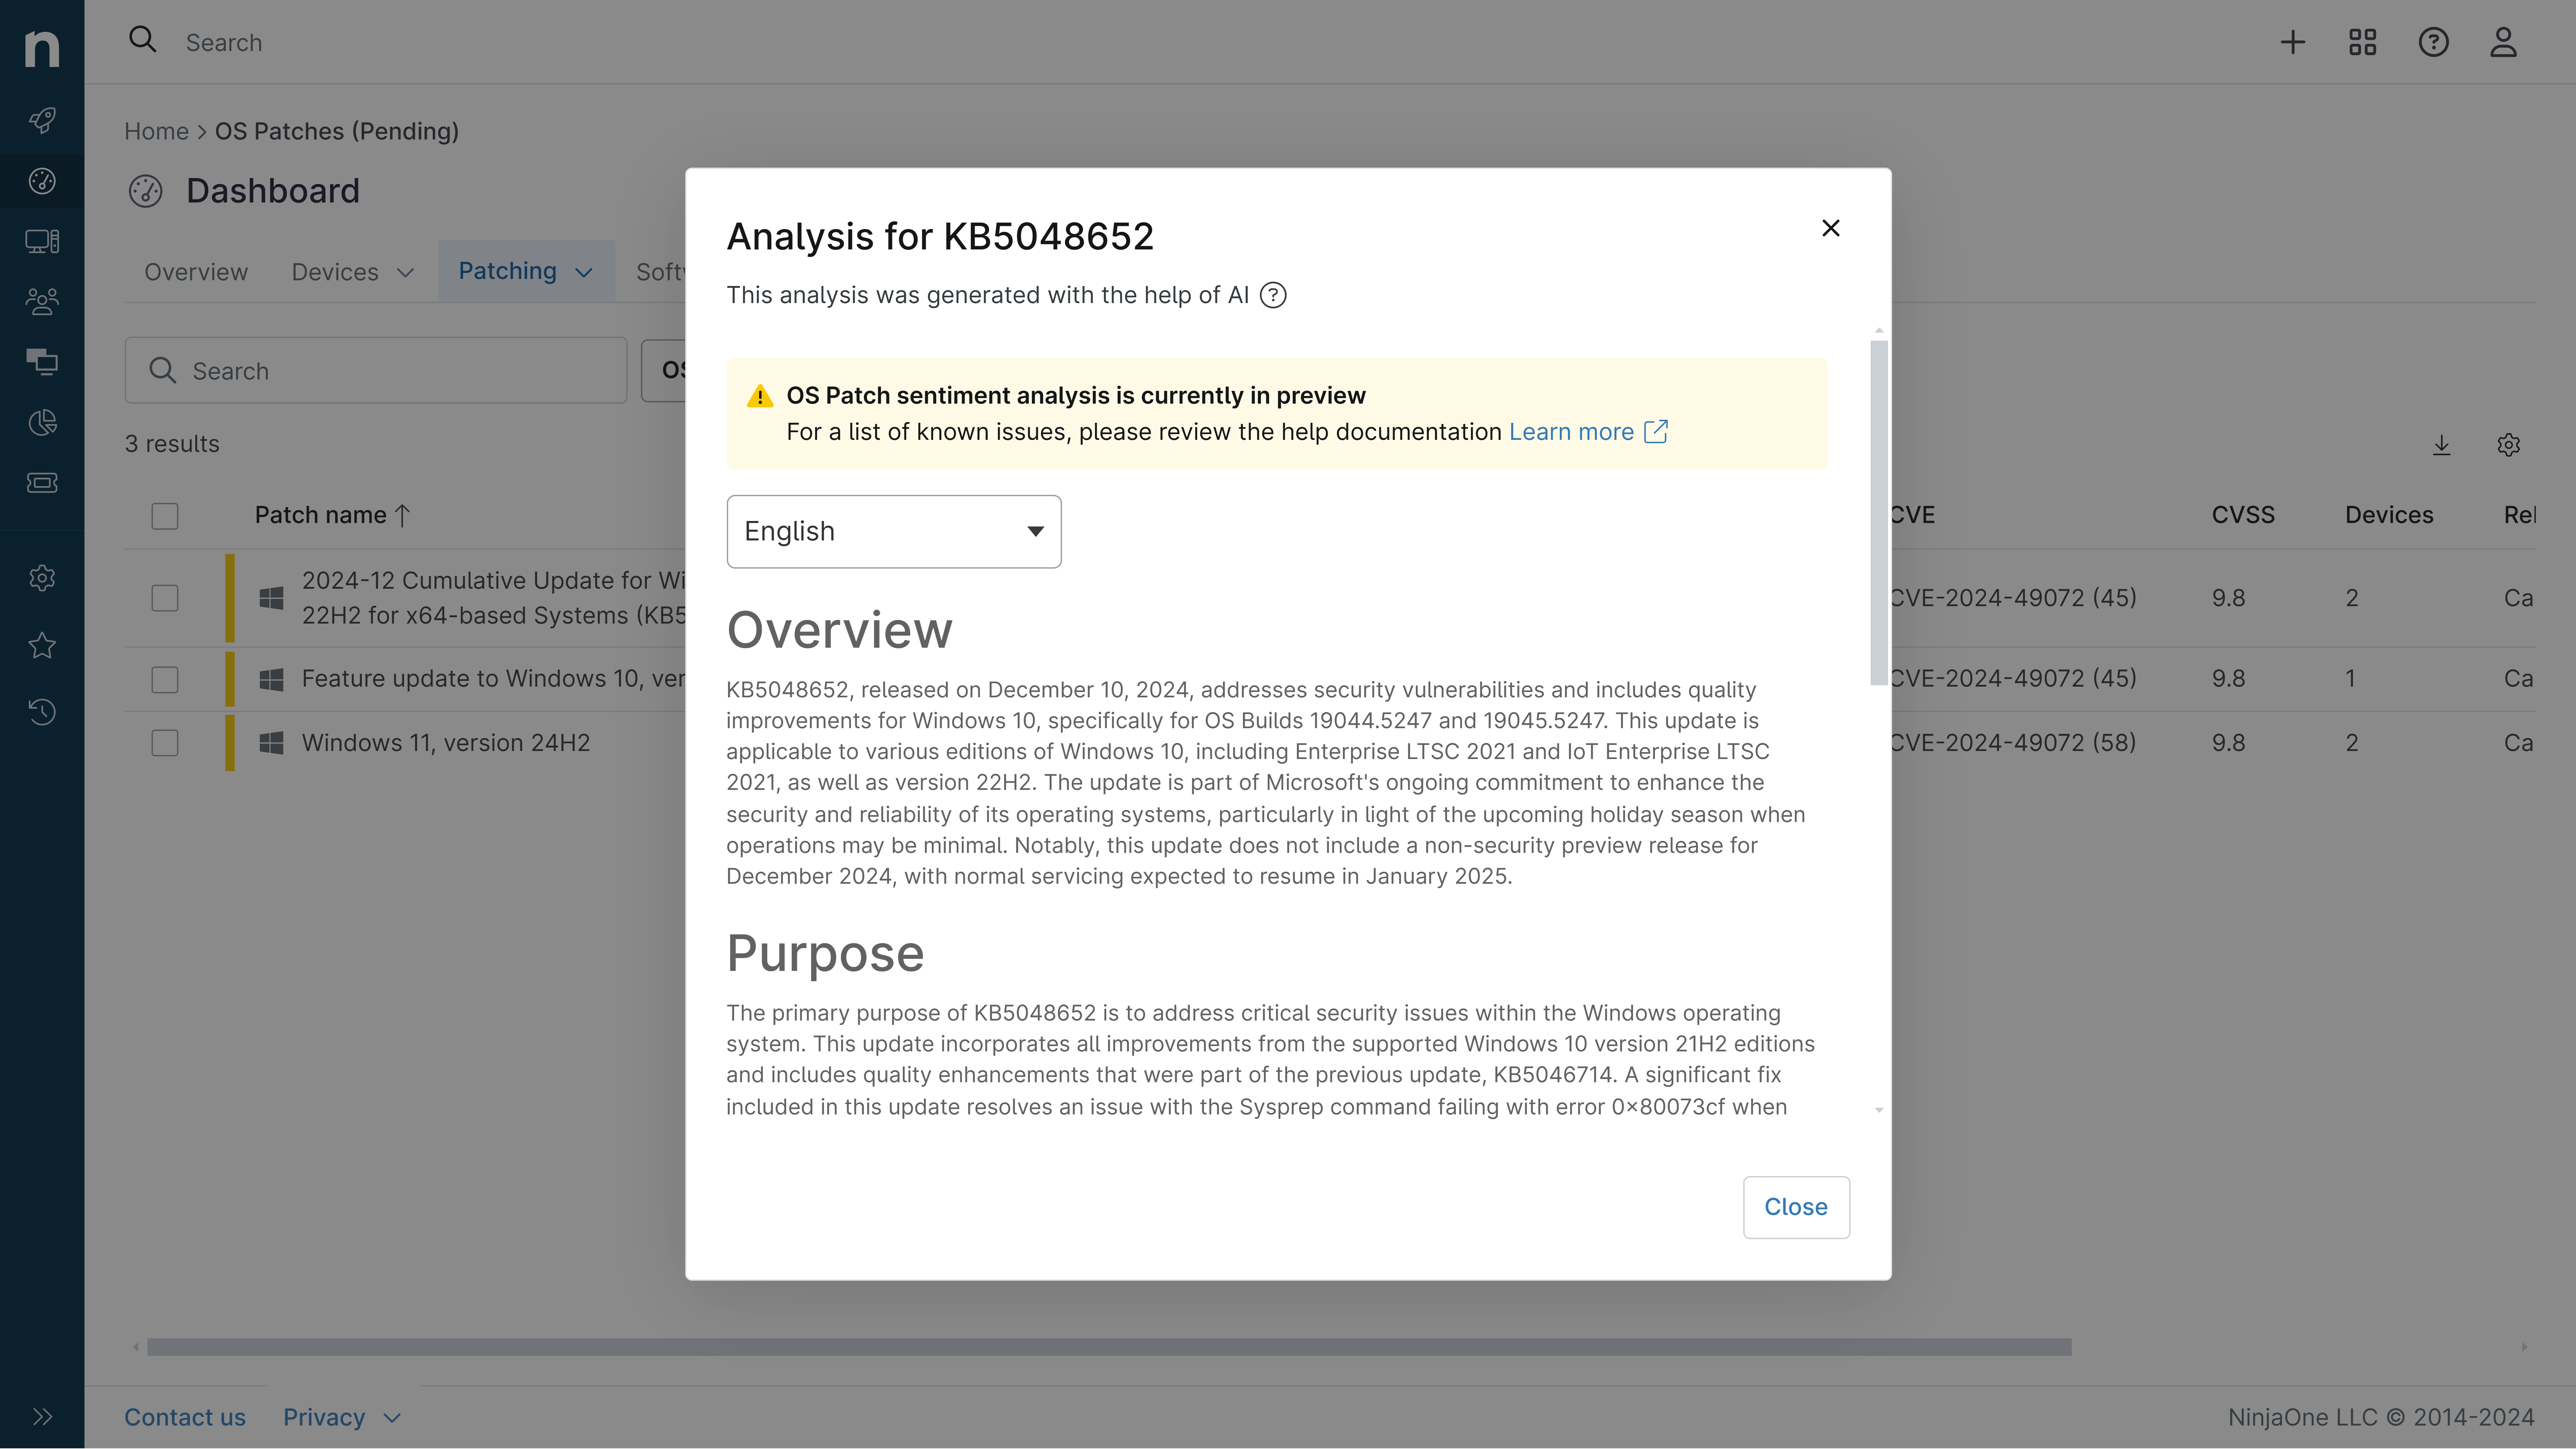
KB5120695: Overview with user sentiment and feedback
Last Updated September 30, 2026
Probability of successful installation and continued operation of the machine
Overview
KB5120695 is a Security and Quality Rollup for .NET Framework 3.5 targeting Windows Server 2012 R2, released on September 8, 2026. This update addresses six security vulnerabilities affecting .NET Framework 3.5, including elevation of privilege and remote code execution issues. The patch is part of Microsoft's Extended Security Updates (ESU) program for systems that have reached end-of-support status.
General Purpose
- Addresses CVE-2026-65810 and CVE-2026-62872 elevation of privilege vulnerabilities in .NET Framework
- Resolves three remote code execution vulnerabilities (CVE-2026-62886, CVE-2026-62897, CVE-2026-70354)
- Patches CVE-2026-62902 information disclosure vulnerability
- Cumulative security and reliability improvements for .NET Framework 3.5
- No new quality and reliability improvements included in this release
General Sentiment
Limited public discussion is available regarding this patch, which is typical for targeted .NET Framework updates on legacy systems. The update addresses critical security vulnerabilities affecting an end-of-support operating system, making it essential for organizations still running Windows Server 2012 R2. Microsoft explicitly notes this is an Extended Security Update requiring active subscription, indicating this is intended for organizations committed to maintaining security on legacy infrastructure.
Known Issues
Disclaimer: We take measures to ensure that AI-generated content is of the highest possible quality, but we cannot guarantee its accuracy and recommend that users do their own independent research. Generated on 2026-09-30 07:39 PM